Conduct
Governance for AI agents. Ship in 60 seconds.
Built for engineering teams. Install in 10 minutes. Evidence for the CISO from day one.
60-second trial (no install)
curl -fsSL conductai.ai/install | sh
Prompts for email + company, provisions a 7-day trial workspace, drops ~/.conduct/env with ANTHROPIC_BASE_URL + OPENAI_BASE_URL + a trial token (200 requests/day shared across both providers). Any Anthropic- or OpenAI-SDK client on the machine (Cursor, Claude Code, LangChain, LiteLLM, raw SDK) now routes through the Guard proxy. A blocked call comes back with a Receipt: https://conductai.ai/theguard/blocks/… URL — click it to view the block, ask Lens follow-up questions, and log in to the dashboard via the magic-link the installer prints.
Full install (for daily use)
pip install conduct-cli
conduct login
conduct sync
Every Claude Code, Cursor, Copilot, and Codex session on that machine is now governed. Blocks, warnings, and a hash-chained audit trail show up at conductai.ai.
Self-host
git clone https://github.com/sseshachala/conductai && cd conductai && docker compose up
# API: localhost:8000  ·  Canvas UI: localhost:3000
What Conduct is
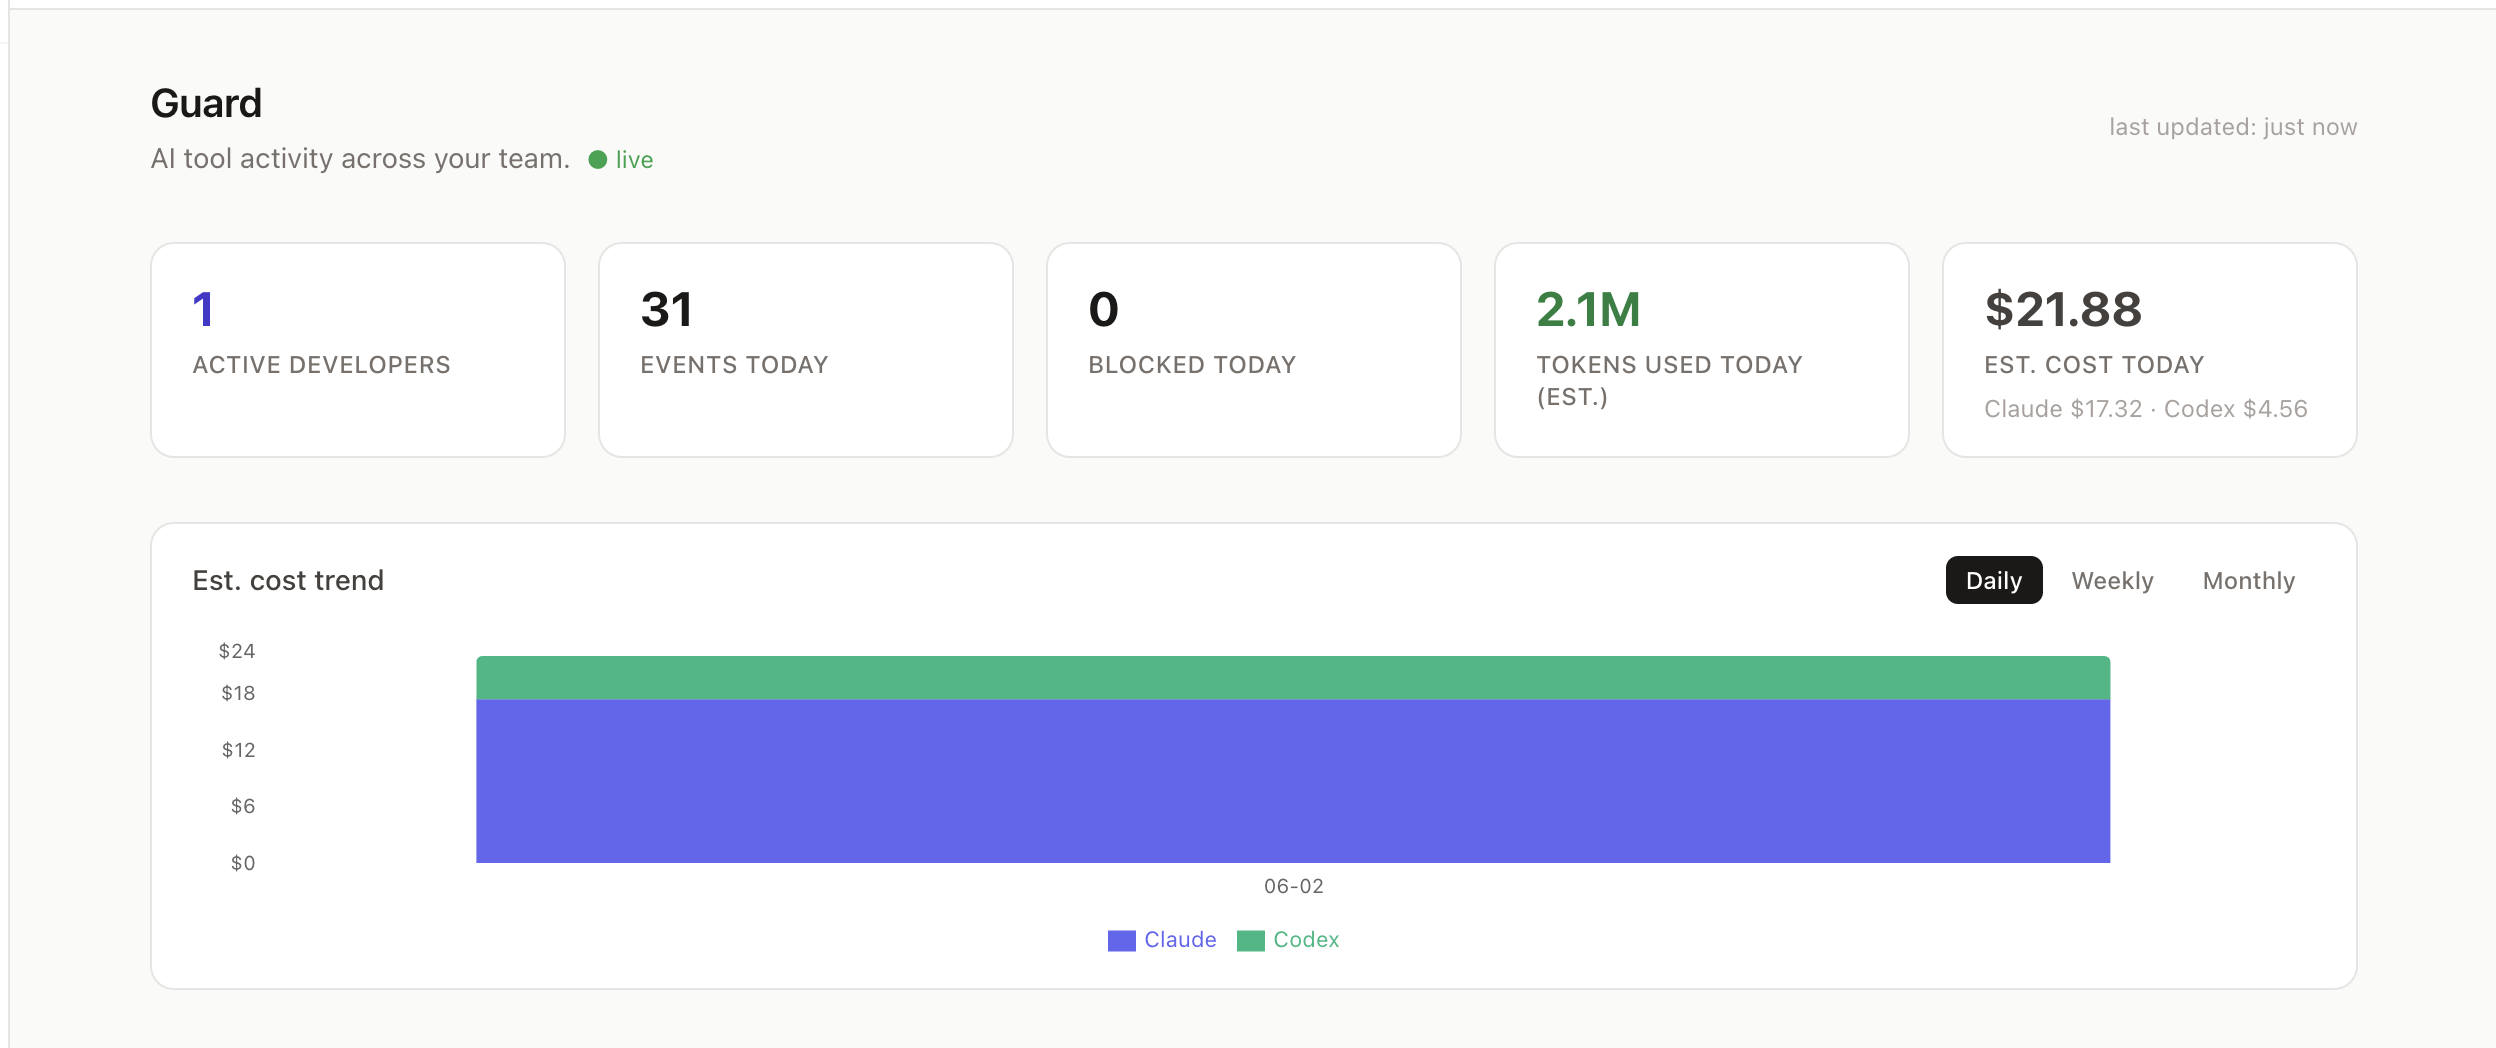
A control plane for AI agents. One policy decides block / warn / audit / inject for every LLM call, every shell tool, every MCP invocation, before the action runs. Same policy applies to a scheduled agent, a developer running Cursor, and a chat session on the platform.
Three surfaces, one policy:
| Surface | What it does |
|---|---|
| Guard | Policy engine. Signed config, hash-chained audit, fail-closed. |
| Router | LLM proxy. Any SDK (Anthropic, OpenAI, Perplexity) points at it. |
| Lens | Chat surface. Ask your workspace anything, every tool call runs through Guard. |
Ask Lens
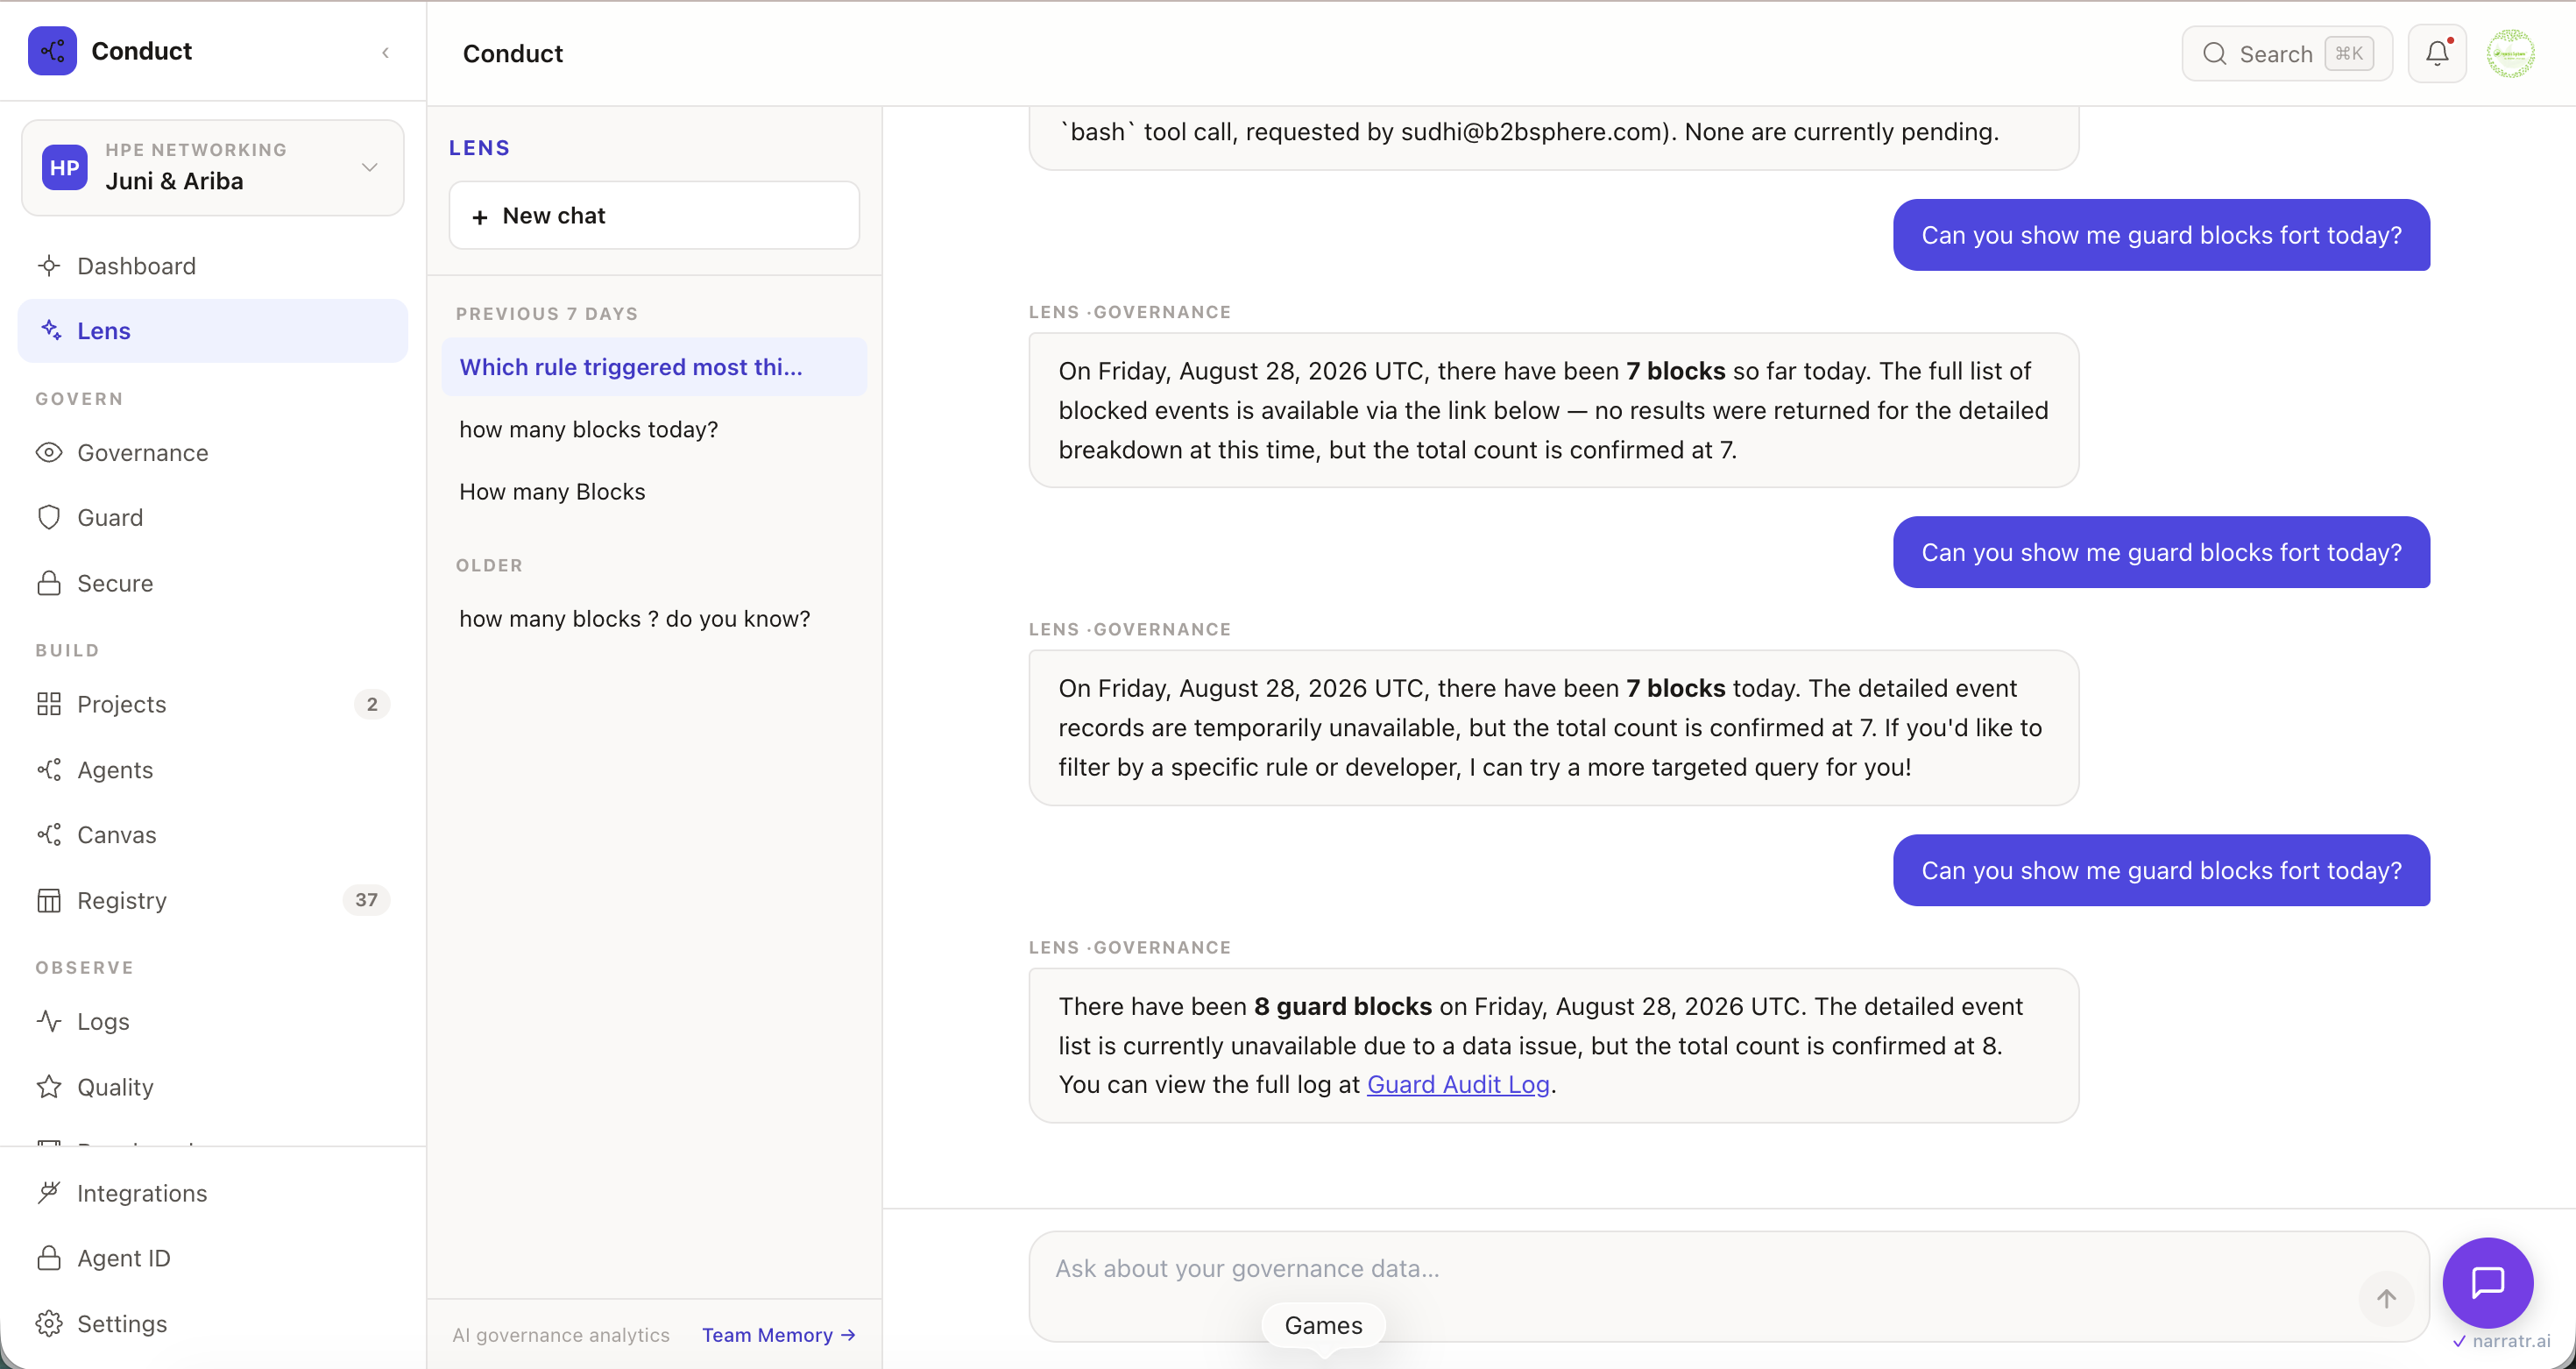
Lens is the chat surface for the whole platform. One input covers Guard activity, workflow state, compliance status, agent spend. Answers come from your workspace data, not a general model. Ask "who got blocked today" and get a table with per-row drilldown links. Lens itself runs through Guard, so the assistant is bound by the same rules as the agents it reports on.
Governance, not observability
Runtime firewalls like Straiker and Lakera tell you what an agent did. Conduct decides what it can do.
| Runtime firewalls | Conduct Guard | |
|---|---|---|
| Timing | After the action | Before the action |
| Config integrity | Trust the pack | Workspace-signed |
| Audit | Log stream | SHA-256 hash chain |
| Coverage | LLM calls only | LLM, shell, MCP |
| Failure mode | Fail-open | Fail-closed |
Three properties make the audit trail hold up in a room with an auditor:
- Signed config. Every workspace signs its active policy set. Every Guard check verifies the signature before enforcing. A tampered pack is rejected before it can decide anything.
- Hash-chained audit. Every decision appends to a SHA-256 chain rooted at workspace genesis. Missing or altered entries break the chain. Verifiable in one click.
- Policy-first, not detection-first. Rules decide before the action runs, with structured reasons. Not anomaly scoring after the fact.
Start free with Discovery
Discovery mode is read-only visibility into every AI action your team takes for 14 days. No policy to author, no upstream install, no cost. When you see something worth blocking, promote a rule from what Discovery already saw.
Router — one endpoint for any SDK
curl https://gateway.conductai.ai/gateway/v1/anthropic/v1/messages \
  -H "Authorization: Bearer cond_agt_..." \
  -H "Content-Type: application/json" \
  -d '{"model":"claude-sonnet-4-6","max_tokens":1024,"messages":[{"role":"user","content":"Hello"}]}'
Every request runs through Guard (policy, budget, audit) before it reaches the upstream provider. Works with any SDK that speaks the provider's HTTP API.
What ships in this repo
| Component | Path |
|---|---|
| Guard runtime | apps/api/app/modules/guard/ |
| Router (proxy) | apps/api/app/modules/guard/routers/proxy.py |
| Compliance packs | apps/api/app/modules/guard/skill_packs/ |
| Canvas UI | apps/web/ |
| Playbook DSL loader | apps/api/app/dsl/ |
| Playbook library | apps/api/playbooks/ (35 pre-built) |
| CLI | packages/conduct-cli/ |
15 compliance packs out of the box: OWASP, SOC 2 CC7.3, HIPAA §164.312, PCI DSS 4.0, EU AI Act Art. 15/16, NIST AI RMF, ISO 42001, plus Python, Node, and Terraform.
20 governed-response playbooks: incident response, approved production changes (release gating, Terraform, network config), AI-risk monitoring, autopilot fixes, and Guard demos. One YAML file each. Edit and run.
Architecture at a glance
   Developer / agent                     Guard control plane
   ─────────────────                     ───────────────────
   Claude Code   ──┐                     ┌── Canvas UI (Next.js)
   Cursor        ──┤   CLI hook  ────►   ├── FastAPI + policy engine
   Copilot       ──┤   (cond_cli)        ├── Postgres (state, audit)
   Codex         ──┘                     ├── Redis (workers, queues)
                     ┌──── MCP  ────►    └── Hash chain (SHA-256)
   Any SDK       ────┤
   (Anthropic,       └── Router ────►    Upstream provider (Anthropic,
    OpenAI,             /gateway/v1/*    OpenAI, Perplexity, ...)
    Perplexity)
Guard checks fire at three chokepoints:
- CLI hook — every Claude Code / Cursor / Copilot / Codex tool call.
- MCP layer — every MCP tool invocation.
- Router — every LLM call by any SDK.
One policy, three enforcement surfaces.
Deployment
- Self-host with docker compose — the command above. Runs everything locally.
- Self-host on Kubernetes — deployment templates ship in issue #1149.
- Hosted — conductai.ai. Free tier includes Discovery; paid tiers unlock enforcement + Router + hash-chain verification API.
Documentation
Full docs live under docs/ — organized by goal (Start · Reference · Concepts · Orientation · Operate · Automate · Policy · Integrations · Examples · ADRs).
Quick paths:
- New to Conduct → Start
- See what's possible → Examples: 20 playbooks
- Write a playbook → Block reference
- Wire into CI, MCP, tools → Automate
- Governance & compliance → Guard rule packs — 183 rules
Security & Trust
- SECURITY.md — vulnerability reporting policy, scope, coordinated disclosure, and safe harbor.
- Threat model — system context, trust boundaries, attacker goals, mitigations, and residual risks.
- Policy decision contract —
guard_checkdecision semantics and fail-mode behavior. - Audit log verification — independent
prev_hash/entry_hashchain verification procedure and example script. - API versioning — proxy/MCP compatibility, deprecation windows, and OpenAPI publication guidance.
License
Apache License 2.0 — the entire repository, including the CLI, Guard, Router, Agent Booster, playbooks, and packs.
- Free for commercial and non-commercial use, modification, and redistribution.
- Includes an explicit patent grant from all contributors (Apache 2.0 §3).
- Trademark rights are not granted; see NOTICE — "Conduct", "Conduct AI", and "Conduct Guard" remain trademarks of Conduct AI.
- Redistribution must preserve the
LICENSEandNOTICEfiles.
The hosted control plane at conductai.ai (canvas UI, team RBAC, marketplace, managed Guard) is a commercial offering built on top of this repository.
For enterprise support, indemnification, or licensing questions, email hello@conductai.ai.
Contributing
We accept bug reports, docs fixes, new playbooks, new packs, tests, and code. Read CONTRIBUTING.md first.
- Everyone participating agrees to the Code of Conduct.
- Security vulnerabilities: don't open a public issue. See SECURITY.md.
- Anything else: GitHub Discussions or SUPPORT.md.
Links
- Product: conductai.ai
- Guard landing: conductai.ai/guard
- Router landing: conductai.ai/router
- Docs: conductai.ai/docs
- Discussions: github.com/sseshachala/conductai/discussions
- Changelog: CHANGELOG.md + Releases
- Book a demo: cal.com/sudhi-seshachala-pks7pd
⭐ If Conduct saves your team time, star it — it helps other teams find it.