
TechTide Harness Kit
The enterprise skill platform for AI coding agents.
385 production skills. 348 specialist agents. 6 cloud providers. 7 harnesses. One repo.

Get Started · Harnesses · Cloud Coverage · Trust · Anatomy · Full Catalog · Contribute
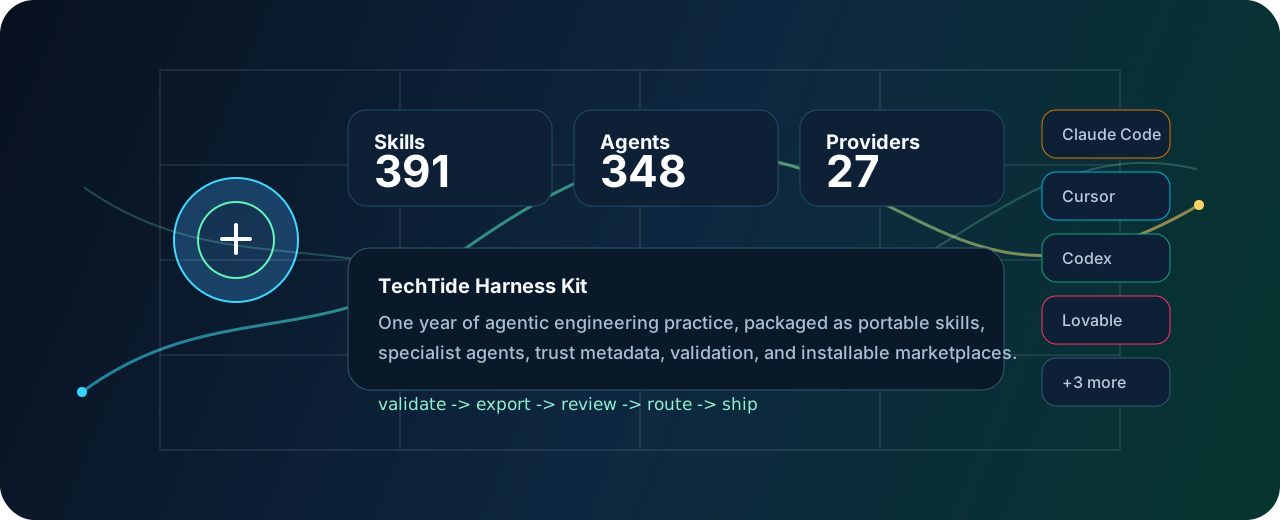
Not an awesome-list. Every skill ships with YAML-frontmatter tool scoping, inline assessment questions, safety checklists with blast-radius checks, and 9 JSON Schema contracts enforcing shape at CI time. Built for teams that answer to auditors, not just developers.
Why this exists
What it does. Ships 385 skills and 348 specialist agents as a schema-validated catalog (skills/, agents/, catalog/, schemas/), exporters that package them for Claude Code, Codex, Cursor, Copilot, Gemini CLI, Kiro, and Lovable (scripts/export-marketplace-agents.mjs, plugins/, powers/, .claude-plugin/), and a npm run validate chain of 25+ gates that checks frontmatter, tool scopes, link syntax, asset integrity hashes, MCP trust matrices, and plugin manifests before the package is published to npm as @techtideai/harness-kit.
Who it serves. Platform, cloud, and security engineers who want agent skills with declared tool permissions, approval gates, and provenance they can show an auditor, and maintainers who need one source tree exported to several agent harnesses without copying files by hand.
Why Alex built it. The repository opened on 2026-05-18 as a "showcase release" (bbc5aad). AGENTS.md states the purpose: a "cloud and zero-trust agentic marketplace for skills, agents, rules, MCP references, and npm distribution" that optimizes for "evidence-backed security workflows: least privilege, source grounding, manifests, validation, and safe automation". TRUST.md records the reasoning behind the gates: "skills are treated as behavior packages that can influence tool use, so every public asset needs source evidence, scoped permissions, security notes, and human accountability." Four days in, a dedup pass removed 96 harness-clone skills and added a hash-collision CI gate (f93e8bb, 2026-05-22: "487 -> 391 unique production skills"), and the Agent Plugins 1.0 distribution landed on 2026-09-05 (894952c). Built by Alex Cinovoj, Founder & CTO of TechTide AI.
Real-world use case (2025-2026 evidence). Verified in this repository. A team adopts Agent Skills, the folder-plus-SKILL.md format Anthropic introduced on 2025-10-16[^1] that is now an open specification with required name and description frontmatter and an optional allowed-tools field[^2], and installs this catalog into Claude Code through a plugin marketplace, the distribution mechanism Anthropic shipped on 2025-10-09[^3]. Before every release npm run validate fails if any skill's allowed-tools, metadata, or integrity hash drifts, and the OpenSSF Scorecard workflow (.github/workflows/scorecard.yml; Scorecard v5.6.0 was released 2026-10-12[^4]) publishes the supply-chain posture reported by the badge above. The install paths and the packed npm artifact are exercised on every push by .github/workflows/install-paths-smoke.yml and .github/workflows/packed-artifact-smoke.yml, which is the evidence behind the verified label.
[^1]: https://github.com/techtideohio/techtide-harness-kit/blob/HEAD/Anthropic, "Introducing Agent Skills", https://claude.com/resources/articles/skills, published 2025-10-16. [^2]: https://github.com/techtideohio/techtide-harness-kit/blob/HEAD/Agent Skills, "Specification", https://agentskills.io/specification, updated 2026-08-04. [^3]: https://github.com/techtideohio/techtide-harness-kit/blob/HEAD/Anthropic, "Customize Claude Code with plugins", https://claude.com/resources/articles/claude-code-plugins, published 2025-10-09. [^4]: https://github.com/techtideohio/techtide-harness-kit/blob/HEAD/ossf/scorecard, release v5.6.0, https://github.com/ossf/scorecard/releases/tag/v5.6.0, published 2026-10-12.
 Works With
|
Anthropic Claude Code Native plugin marketplace. One command installs 348 agents with full trust metadata. |
Cursor AI IDE Plugin directory integration. Clone once, get schema-validated skills across every provider lane. |
OpenAI Codex Marketplace plugin with dual-plugin architecture. Full agent catalog plus MCP trust references. |
Lovable One ZIP per skill. Generate archives, upload to workspace. Vibe-coding with enterprise guardrails. |


More harnesses: GitHub Copilot, Gemini CLI, Kiro
| Harness | Install | Format |
|---|---|---|
| GitHub Copilot | copilot plugin marketplace add TechTideOhio/techtide-harness-kit |
.github/plugin/ manifest |
| Gemini CLI | npx thk-export-agents --platform gemini --all --repo . |
Workspace skill adapters |
| Kiro | Add powers/techtide-* directories in Kiro panel |
Powers packages |
Full comparison and install paths: docs/integrations/installation-guide.md
 Get Started
npm install @techtideai/harness-kit

# Validate everything (25+ gates, no secrets required)
npm run validate

# Export agents for your harness
npx thk-export-agents --platform claude-code --provider aws --repo .
npx thk-export-agents --platform codex --role cloud-security-engineer --repo .
npx thk-export-agents --platform gemini --all --repo .
 By The Numbers
| 385 | 348 | 6 | 33 |
| Production skills | Specialist agents | Cloud providers | Provider lanes |
| 9 | 25+ | 7 | 12 |
| JSON Schema contracts | Validation gates | Harness adapters | Core agent skills |
 Cloud Coverage
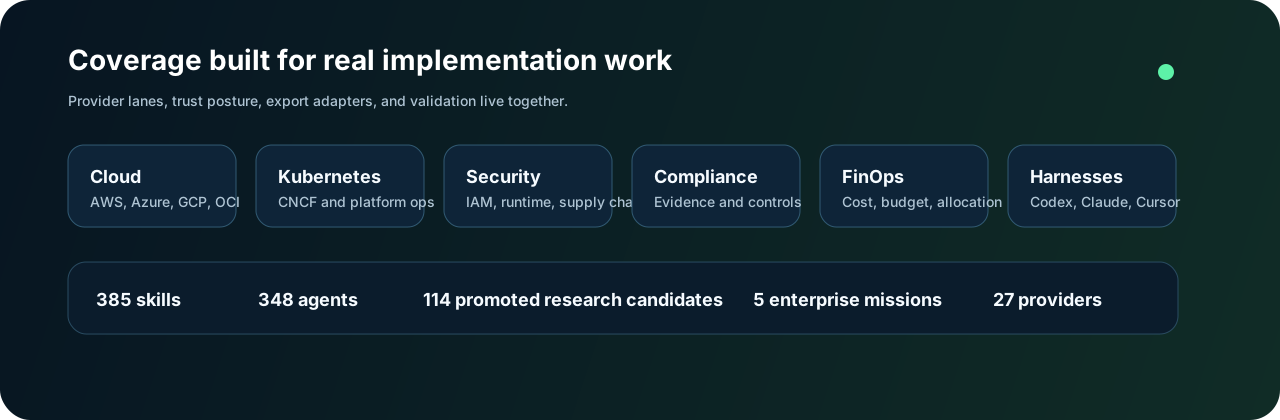
Every cloud has deep, provider-specific skills with inline assessment questions and validation checklists -- not generic templates with names swapped.
|
Major Cloud Providers
|
Infrastructure & Governance
|
 Skill Anatomy
Every skill follows a consistent, agent-optimized structure with least-privilege tool scoping:
skills/<provider>/<skill-id>/
  SKILL.md            # YAML frontmatter + workflow + assessment questions + checklist
  metadata.json       # Schema-validated: id, version, harnesses, official_docs
  references/         # Safety checklists, official sources, extended guidance
|
Frontmatter declares tool scope No |
Inline assessment questions + checklists |
 What Ships
| Surface | Purpose |
|---|---|
skills/ |
Portable task workflows with frontmatter, assessment questions, and guardrails |
agents/ |
Specialist roles with harness-specific adapters |
rules/ |
Harness-specific operating guidance |
mcp/ |
Trusted MCP server integration references |
catalog/ |
Machine-readable indexes, trust metadata, roles, and integrity hashes |
schemas/ |
9 JSON Schema contracts enforcing skill and agent shape |
powers/ |
Kiro Power packages |
plugins/ |
Codex and Claude Code plugin packages |
 Enterprise Trust
|
Security & governance layers
|
Trust documentation
|
 Security
Report vulnerabilities through SECURITY.md. The findings below were open on the repository's Dependabot and code-scanning dashboards as of 2026-10-20. They are documented here rather than dismissed.
| Finding | Status |
|---|---|
braces 3.0.3, GHSA-vfj7-8cjw-p6xm (stack-exhaustion denial of service through deeply nested patterns) |
Known upstream advisory with no fixed release as of 2026-10-20. It reaches this repository only as a devDependency transitive (@semantic-release/commit-analyzer -> micromatch -> braces in package-lock.json) used by the release workflow; the published npm package declares no runtime dependencies, so consumers do not install it. The Scorecard Vulnerabilities check reports the same advisory. No code-level mitigation exists in this repository. |
OpenSSF Scorecard Code-Review |
Scorecard found 0 of the last 19 changesets with an approving review from a second account. That is an accurate description of a single-maintainer project: changes land through pull requests with CI gates, but no independent reviewer approves them. It is a process finding, not a code defect, and it stays open until a second maintainer reviews changes. |
OpenSSF Scorecard Pinned-Dependencies |
.github/workflows/packed-artifact-smoke.yml installs the tarball it just built with npm install inside a throwaway consumer project. There is no registry version to pin because the artifact comes from the same job. |
OpenSSF Scorecard Fuzzing and CII-Best-Practices |
The repository runs property-based tests with fast-check (npm run test:fuzz) but is not registered with OSS-Fuzz, and it has not applied for an OpenSSF Best Practices badge. |
CodeQL js/unused-local-variable (two notes in scripts/proof-layer.mjs) |
Dead code, not a security defect: an unused posix() helper and an unused proofSources list of external references. Left for a deliberate code change by the maintainer because the list may be intended for future use. |
 vs Alternatives
| Feature | TechTide Harness Kit | Awesome lists | Toolkit repos |
|---|---|---|---|
| Production skills | 385 | Links only | 35-184 |
| Cloud providers | 6 | 0 | 1-2 |
| Schema validation | 9 schemas, 25+ gates | None | None |
| Trust metadata | Per-skill scopes + approval gates | None | None |
| Safety checklists | Blast radius + rollback | None | None |
| Multi-harness | 7 adapters | 1 | 1-2 |
| Assessment questions | Provider-specific banks | None | None |
| Enterprise governance | OpenSSF, CodeQL, provenance | None | None |
| European cloud | 5 providers, 30 skills | None | None |
| NVIDIA / GPU | CUDA, TensorRT, Triton | None | None |
 Common Commands
# Validate everything (25+ gates)
npm run validate

# Check trust + proof layer
npm run trust:check && npm run proof-layer:check

# Export agents
npm run agents:export -- --list
npm run agents:export -- --platform claude-code --provider aws --repo .
npm run agents:export -- --platform codex --all --repo .

# Regenerate artifacts
npm run proof-layer:write && npm run plugin-manifest:write
 Documentation
| Topic | Link |
|---|---|
| Installation guide | docs/integrations/installation-guide.md |
| Harness compatibility | docs/compatibility.md |
| Cross-harness skills | docs/cross-harness-skills.md |
| Marketplace model | docs/marketplace-model.md |
| Quality bar | docs/quality-bar.md |
| Taxonomy | docs/taxonomy.md |
| Lovable skill imports | docs/integrations/lovable-skills.md |
| External skill research | [docs/external-skill-research.md](https://g |