
Klustr
A native Kubernetes desktop client that installs nothing in your cluster.


macOS · brew tap sametkum/klustr && brew install klustr
Arch / CachyOS / Manjaro · paru -S klustr-bin
Debian / Ubuntu · sudo apt install ./klustr_*_amd64.deb (download first)
▶ Watch the full-quality video
What is Klustr?
Klustr is a cross-platform Kubernetes desktop client built with Wails (Go + native webview) and React. It uses your existing ~/.kube/config and speaks the standard Kubernetes API directly — nothing is deployed in the cluster. Drop the binary in, point at any context, and you're looking at a live view of everything you have permission to see — built-in resources, full RBAC with a subject → effective-permissions review, Custom Resources (CRDs), Helm releases, Argo CD Applications, Flux CD reconcilers, Tekton pipelines, Gateway API routes, cert-manager certificates, and Kyverno policy reports included. No extra logins, no argocd, flux, tkn or helm CLI required — only your kubeconfig.
Features
- 🔌 Pure client. No CRDs, no in-cluster components — works with whatever your kubeconfig already grants.
- 🔁 Live everywhere.
client-goinformers, never polled. - 🌐 Multi-context aggregation. View 2+ clusters in one table, per-context status pings with latency in the status bar.
- 👥 Context groups & tags. Named multi-context groups; color tags on the top bar so you always know which environment you're touching.
- 📋 Every built-in resource. Workloads, networking, storage, config, admission, autoscaling, and the full RBAC set under a dedicated Access Control sidebar group.
- 🔎 Access Review. Subject → effective-permissions GVR × verb matrix with the binding → role chain behind every ✓, wildcards and
cluster-adminflagged. Live, no--asimpersonation, no extra API traffic. - 🧩 Custom Resources (CRDs). Auto-discovered on connect, grouped by API group, watch-backed.
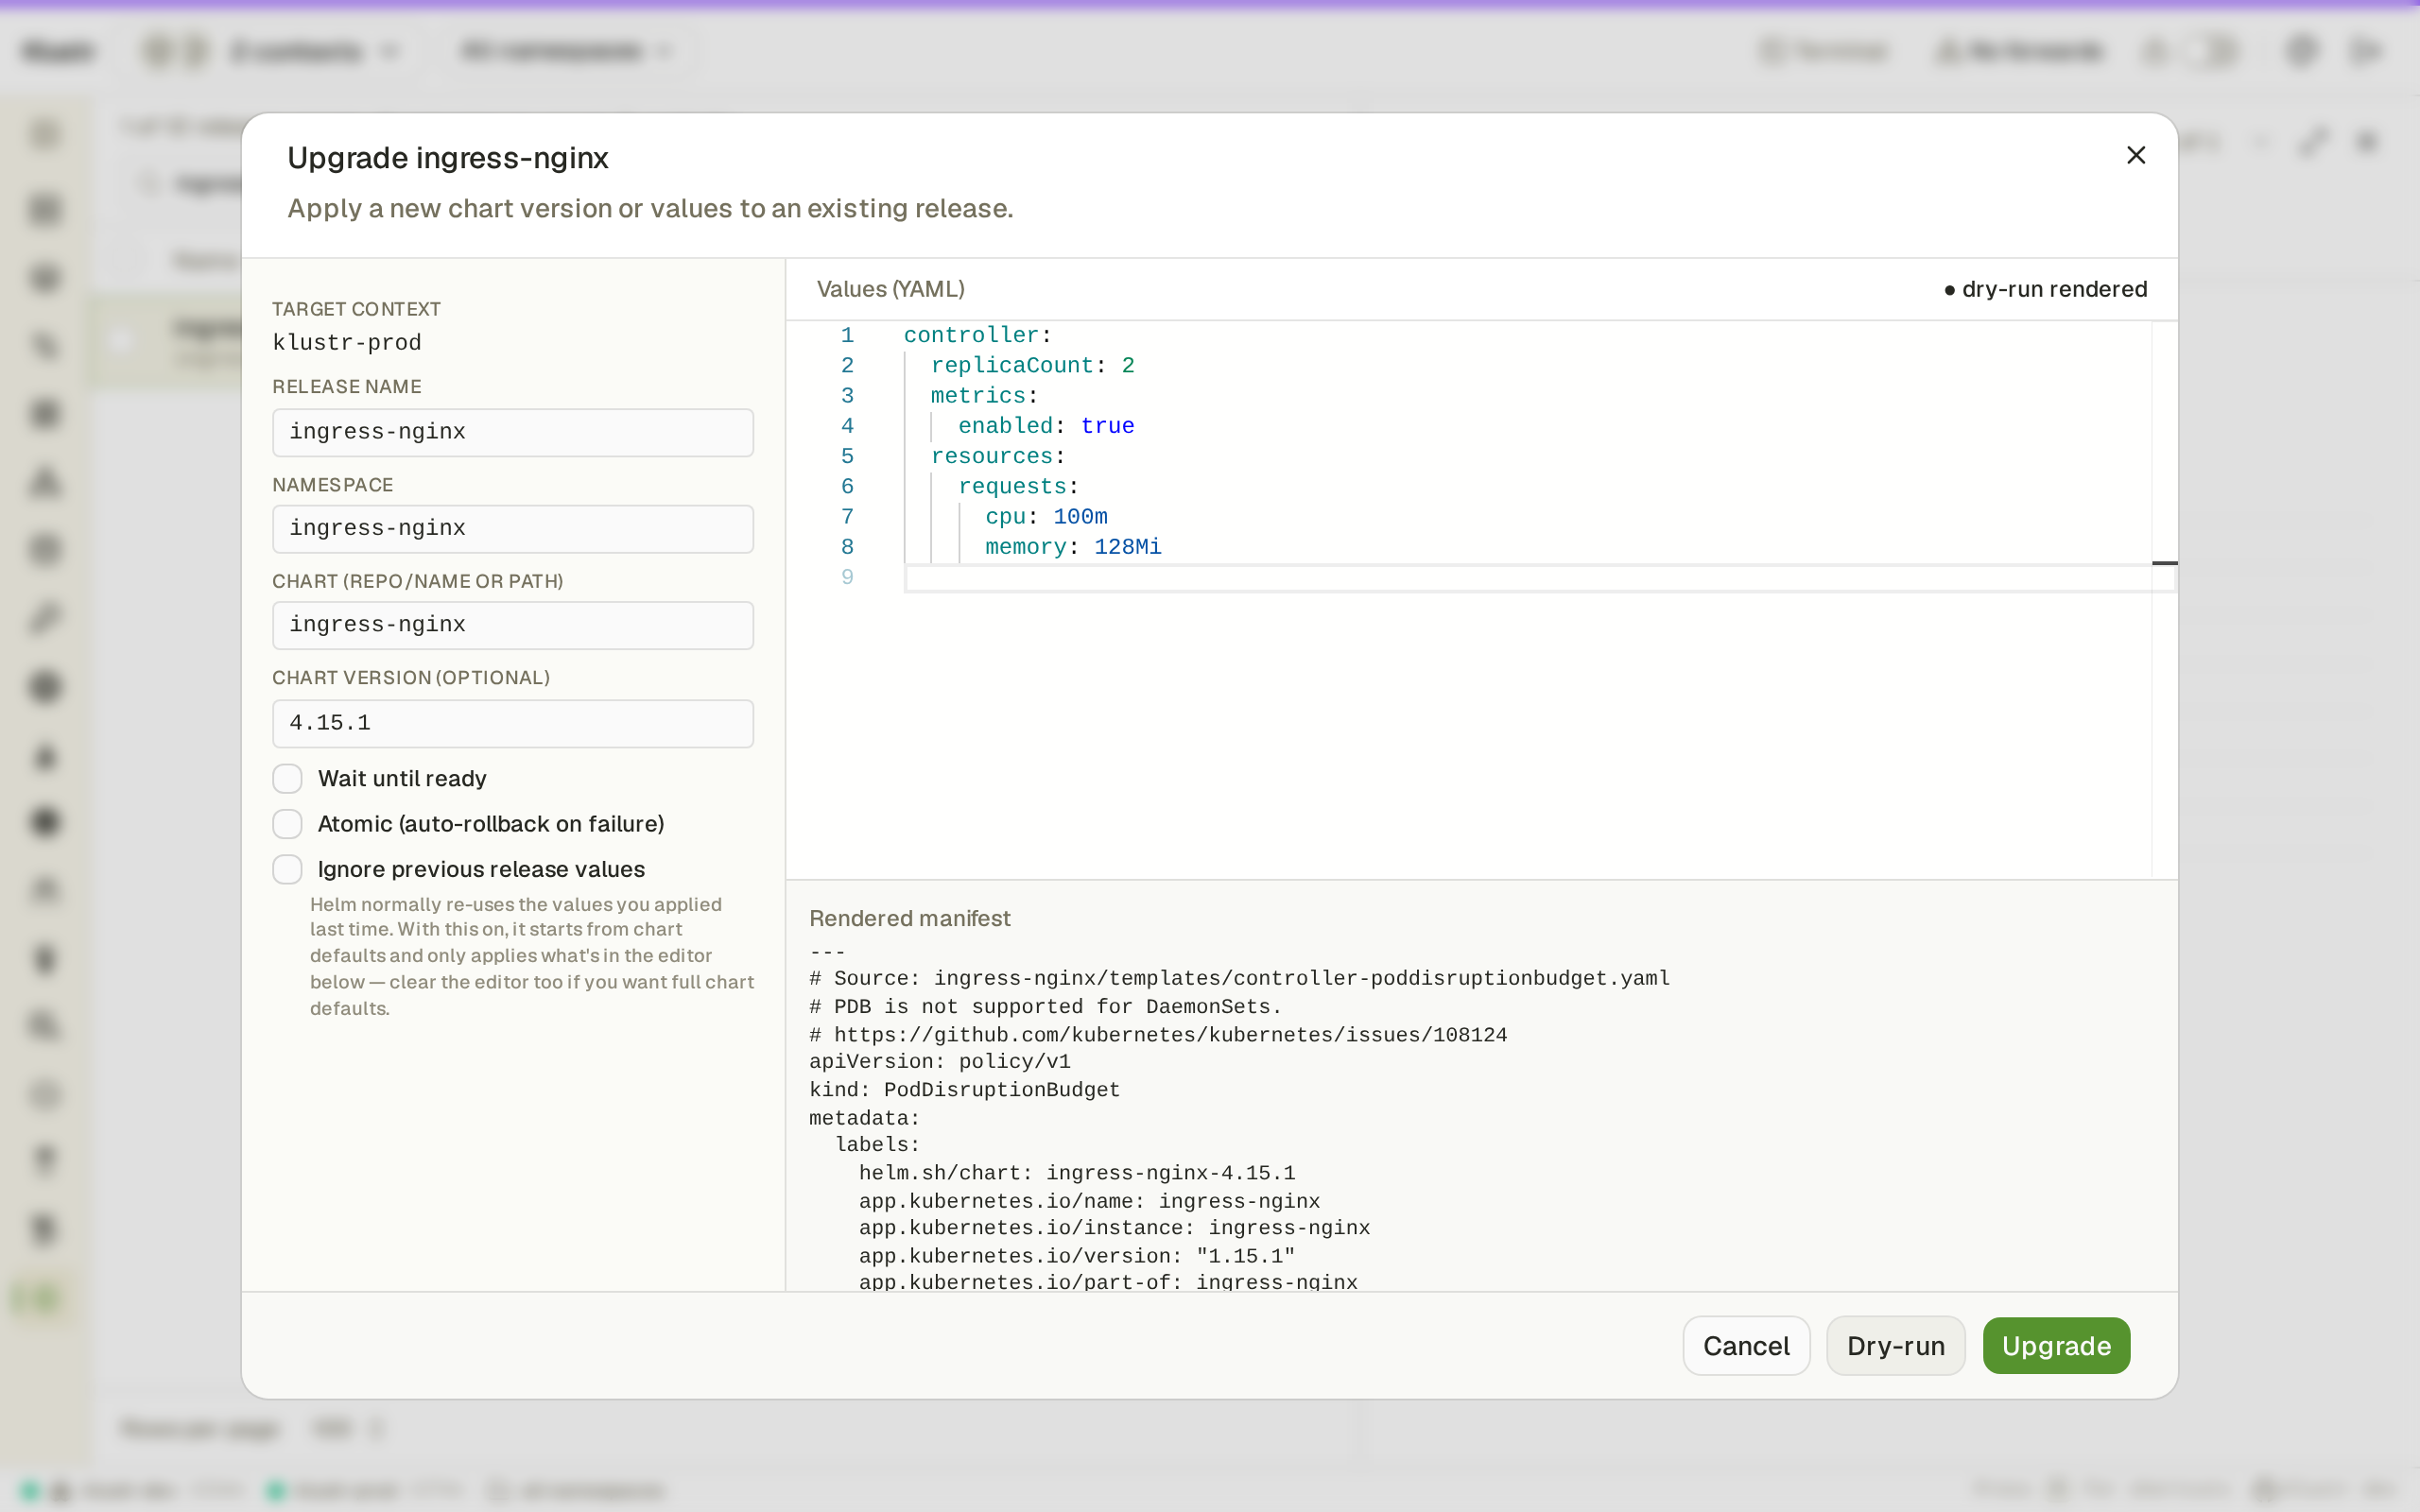
- ⎈ Helm. First-class Helm v3: install / upgrade / rollback / uninstall with a dry-run preview before any change, plus repo management and chart search.
- 🚢 Argo CD. Sync, Refresh, Rollback and cascade-aware Delete through the Kubernetes API — no
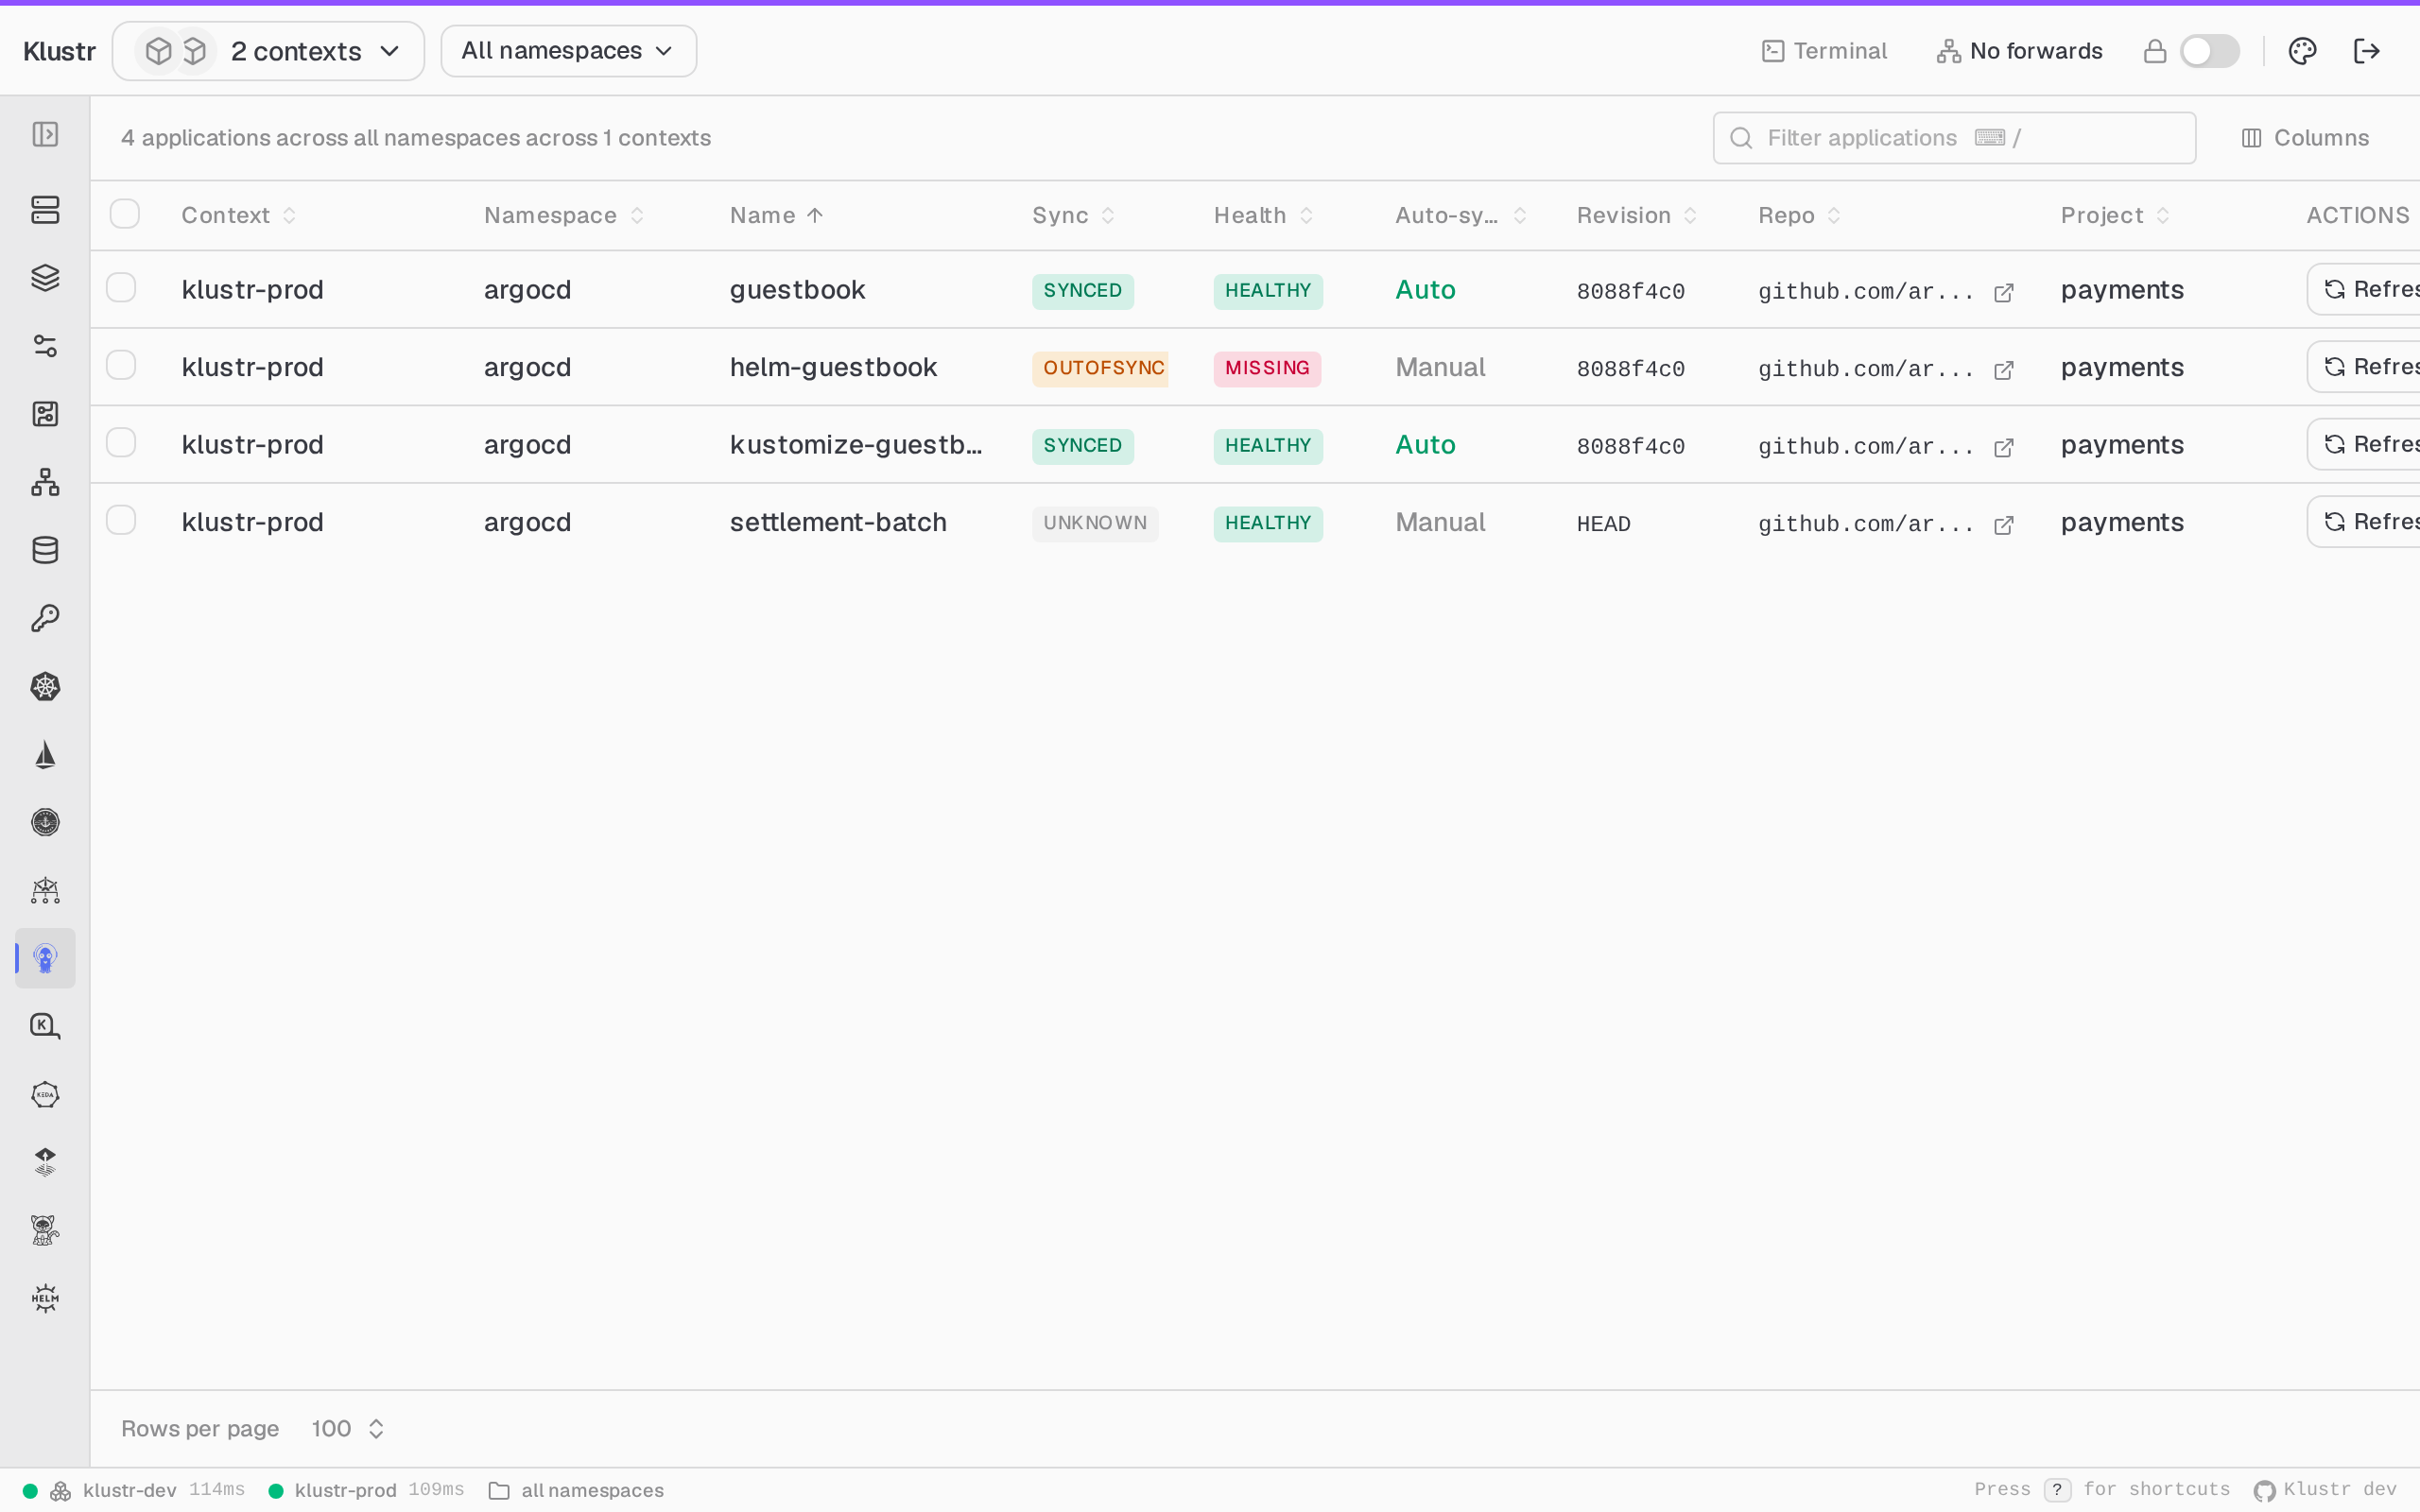
argocd-server, noargocdCLI, no Argo login. - 🚀 Flux CD. Kustomization · HelmRelease · GitRepository · HelmRepository · OCIRepository · Bucket · Provider · Alert · Receiver, plus ImageRepository, ImagePolicy and ImageUpdateAutomation. Inspect scanned tags, selected images and digests, and automation Git commits; follow repository references across namespaces. Reconcile and Suspend/Resume actions are available where the resource API supports them, with no
fluxCLI required. - 🏗️ Tekton. PipelineRuns, TaskRuns, Pipelines and Tasks. A PipelineRun's task table joins the resolved pipeline with its TaskRuns and skipped tasks; TaskRun step logs open on the running or failed step; Cancel and Rerun without
tkn. - 🌉 Gateway API. Typed informers; listener table, per-rule match → backend → weight matrix and
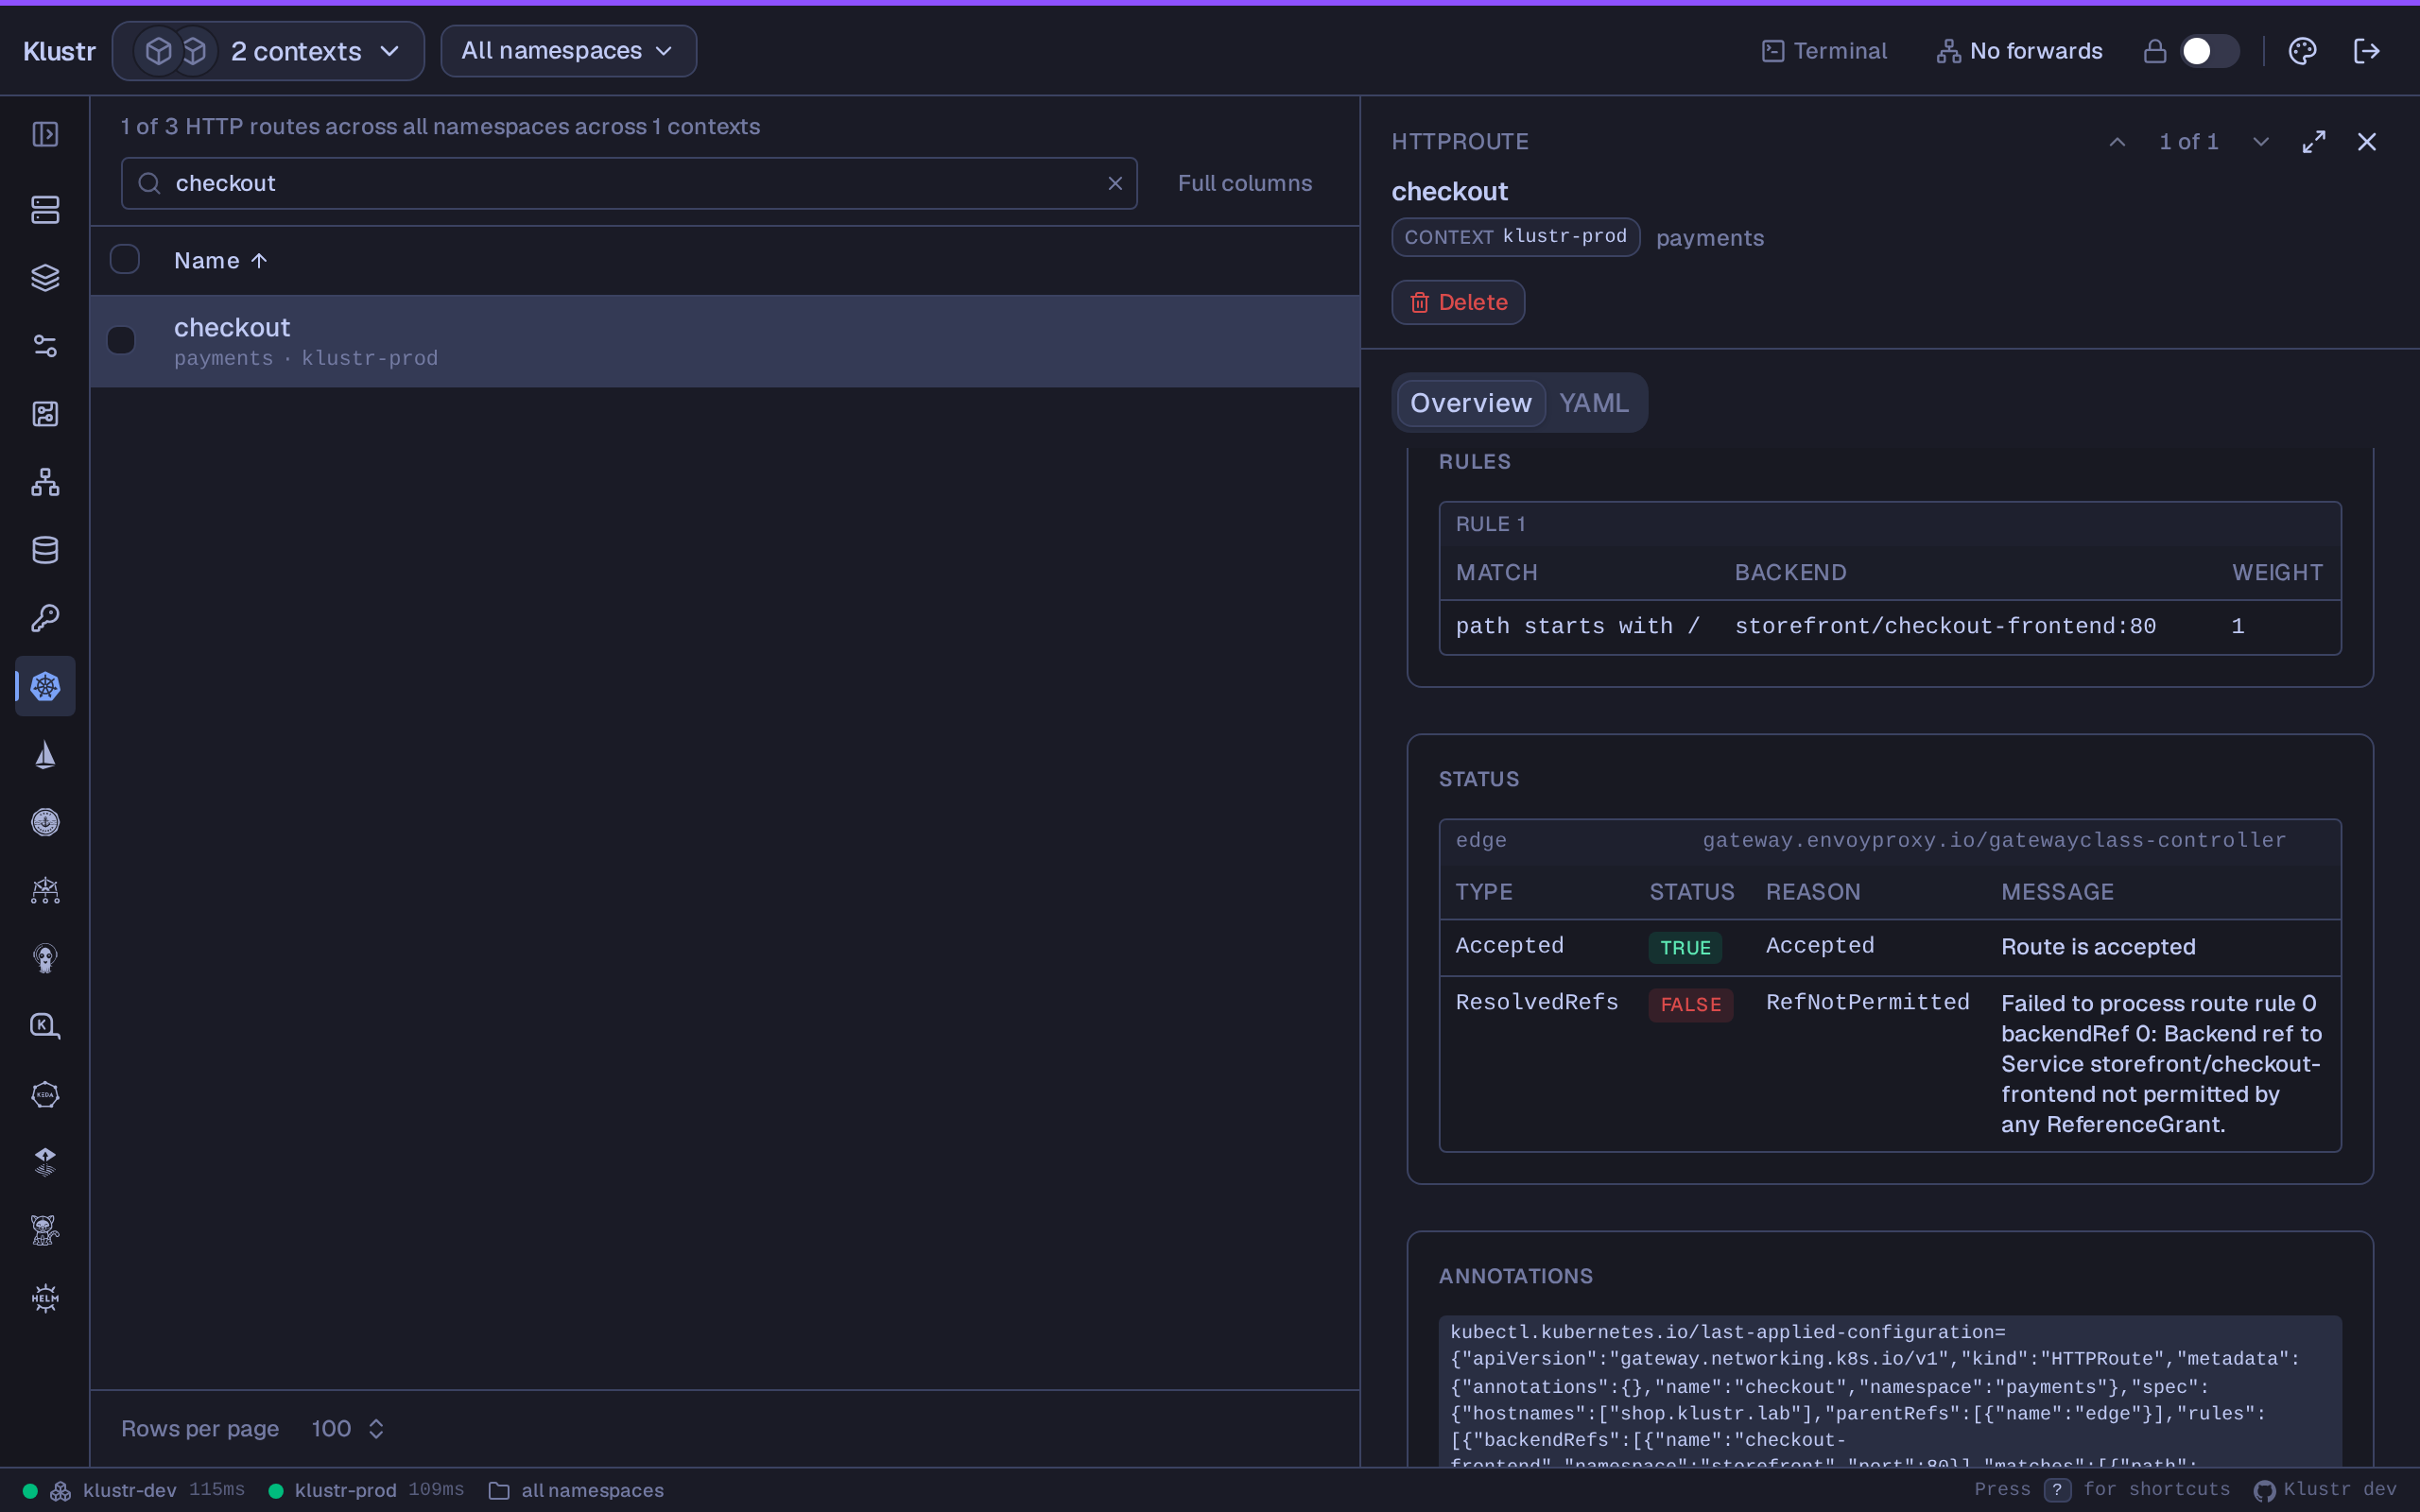
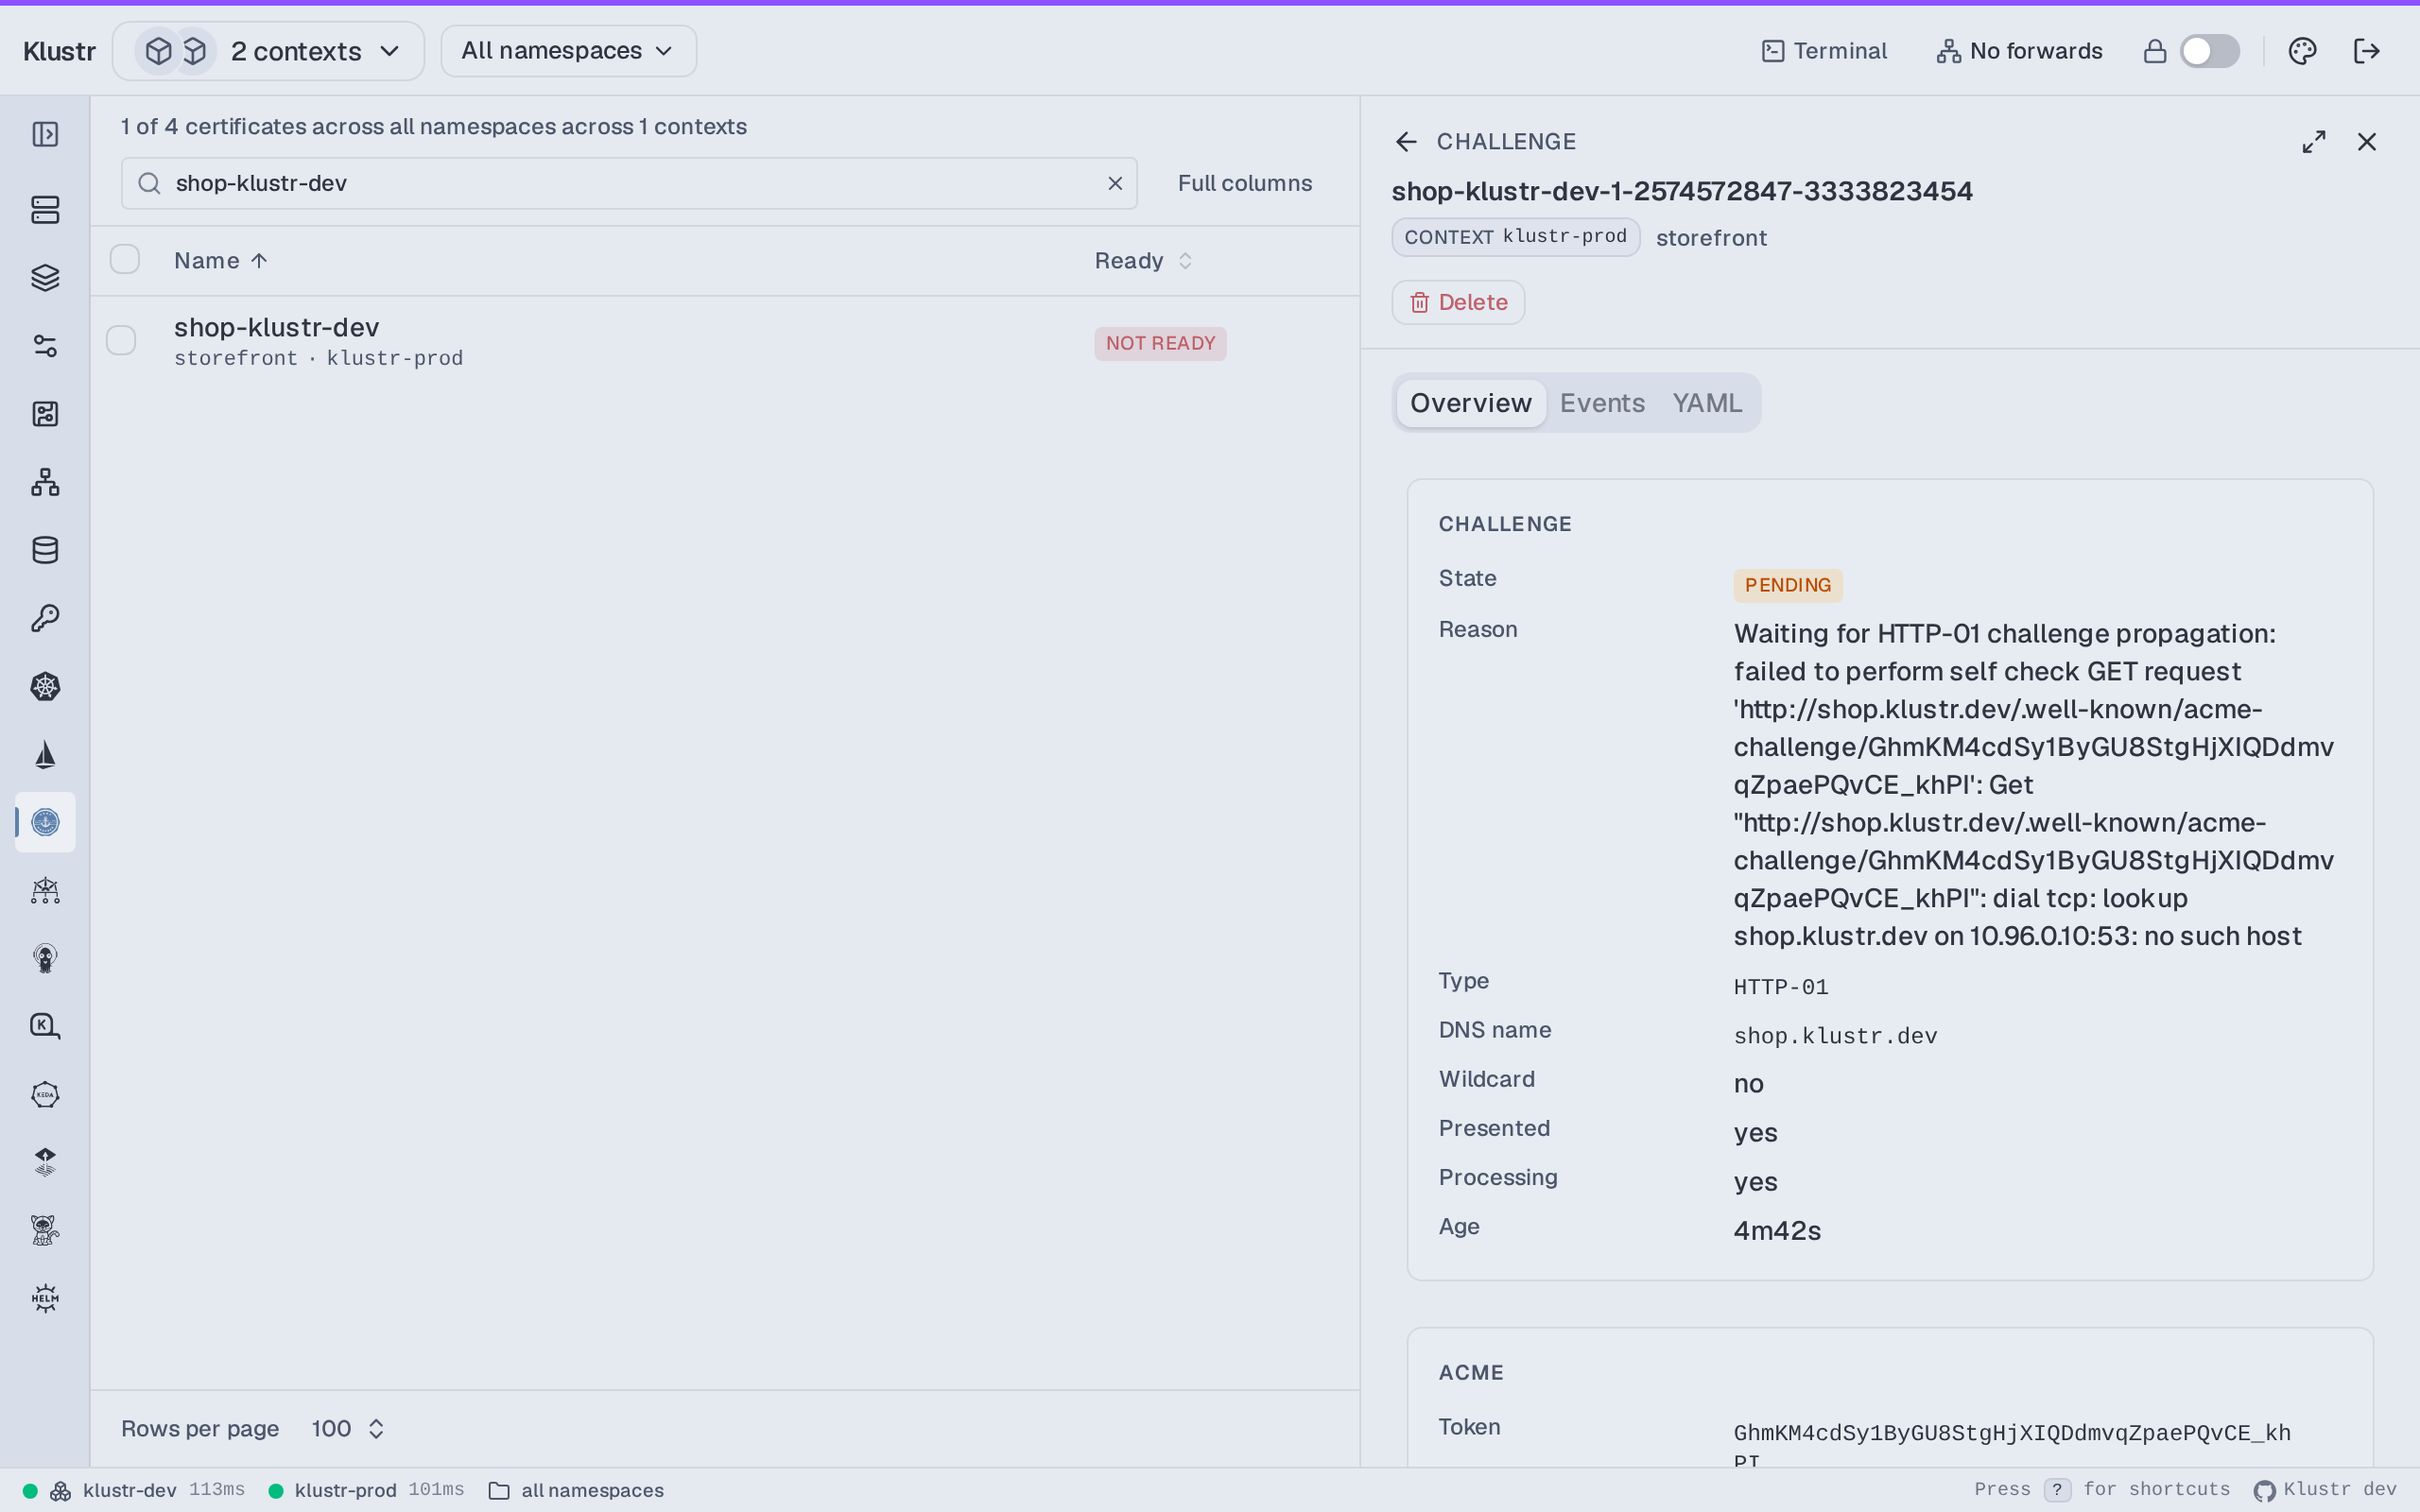
RouteParentStatusso a misrouted parent orRefNotPermittedbackend is one click away. Vendor-neutral. - 🔐 cert-manager. Certificates, Issuers / ClusterIssuers, and the full issuance chain — CertificateRequest → Order → Challenge — with ready/expiry status and a drill-down across the chain. One-click Renew, no
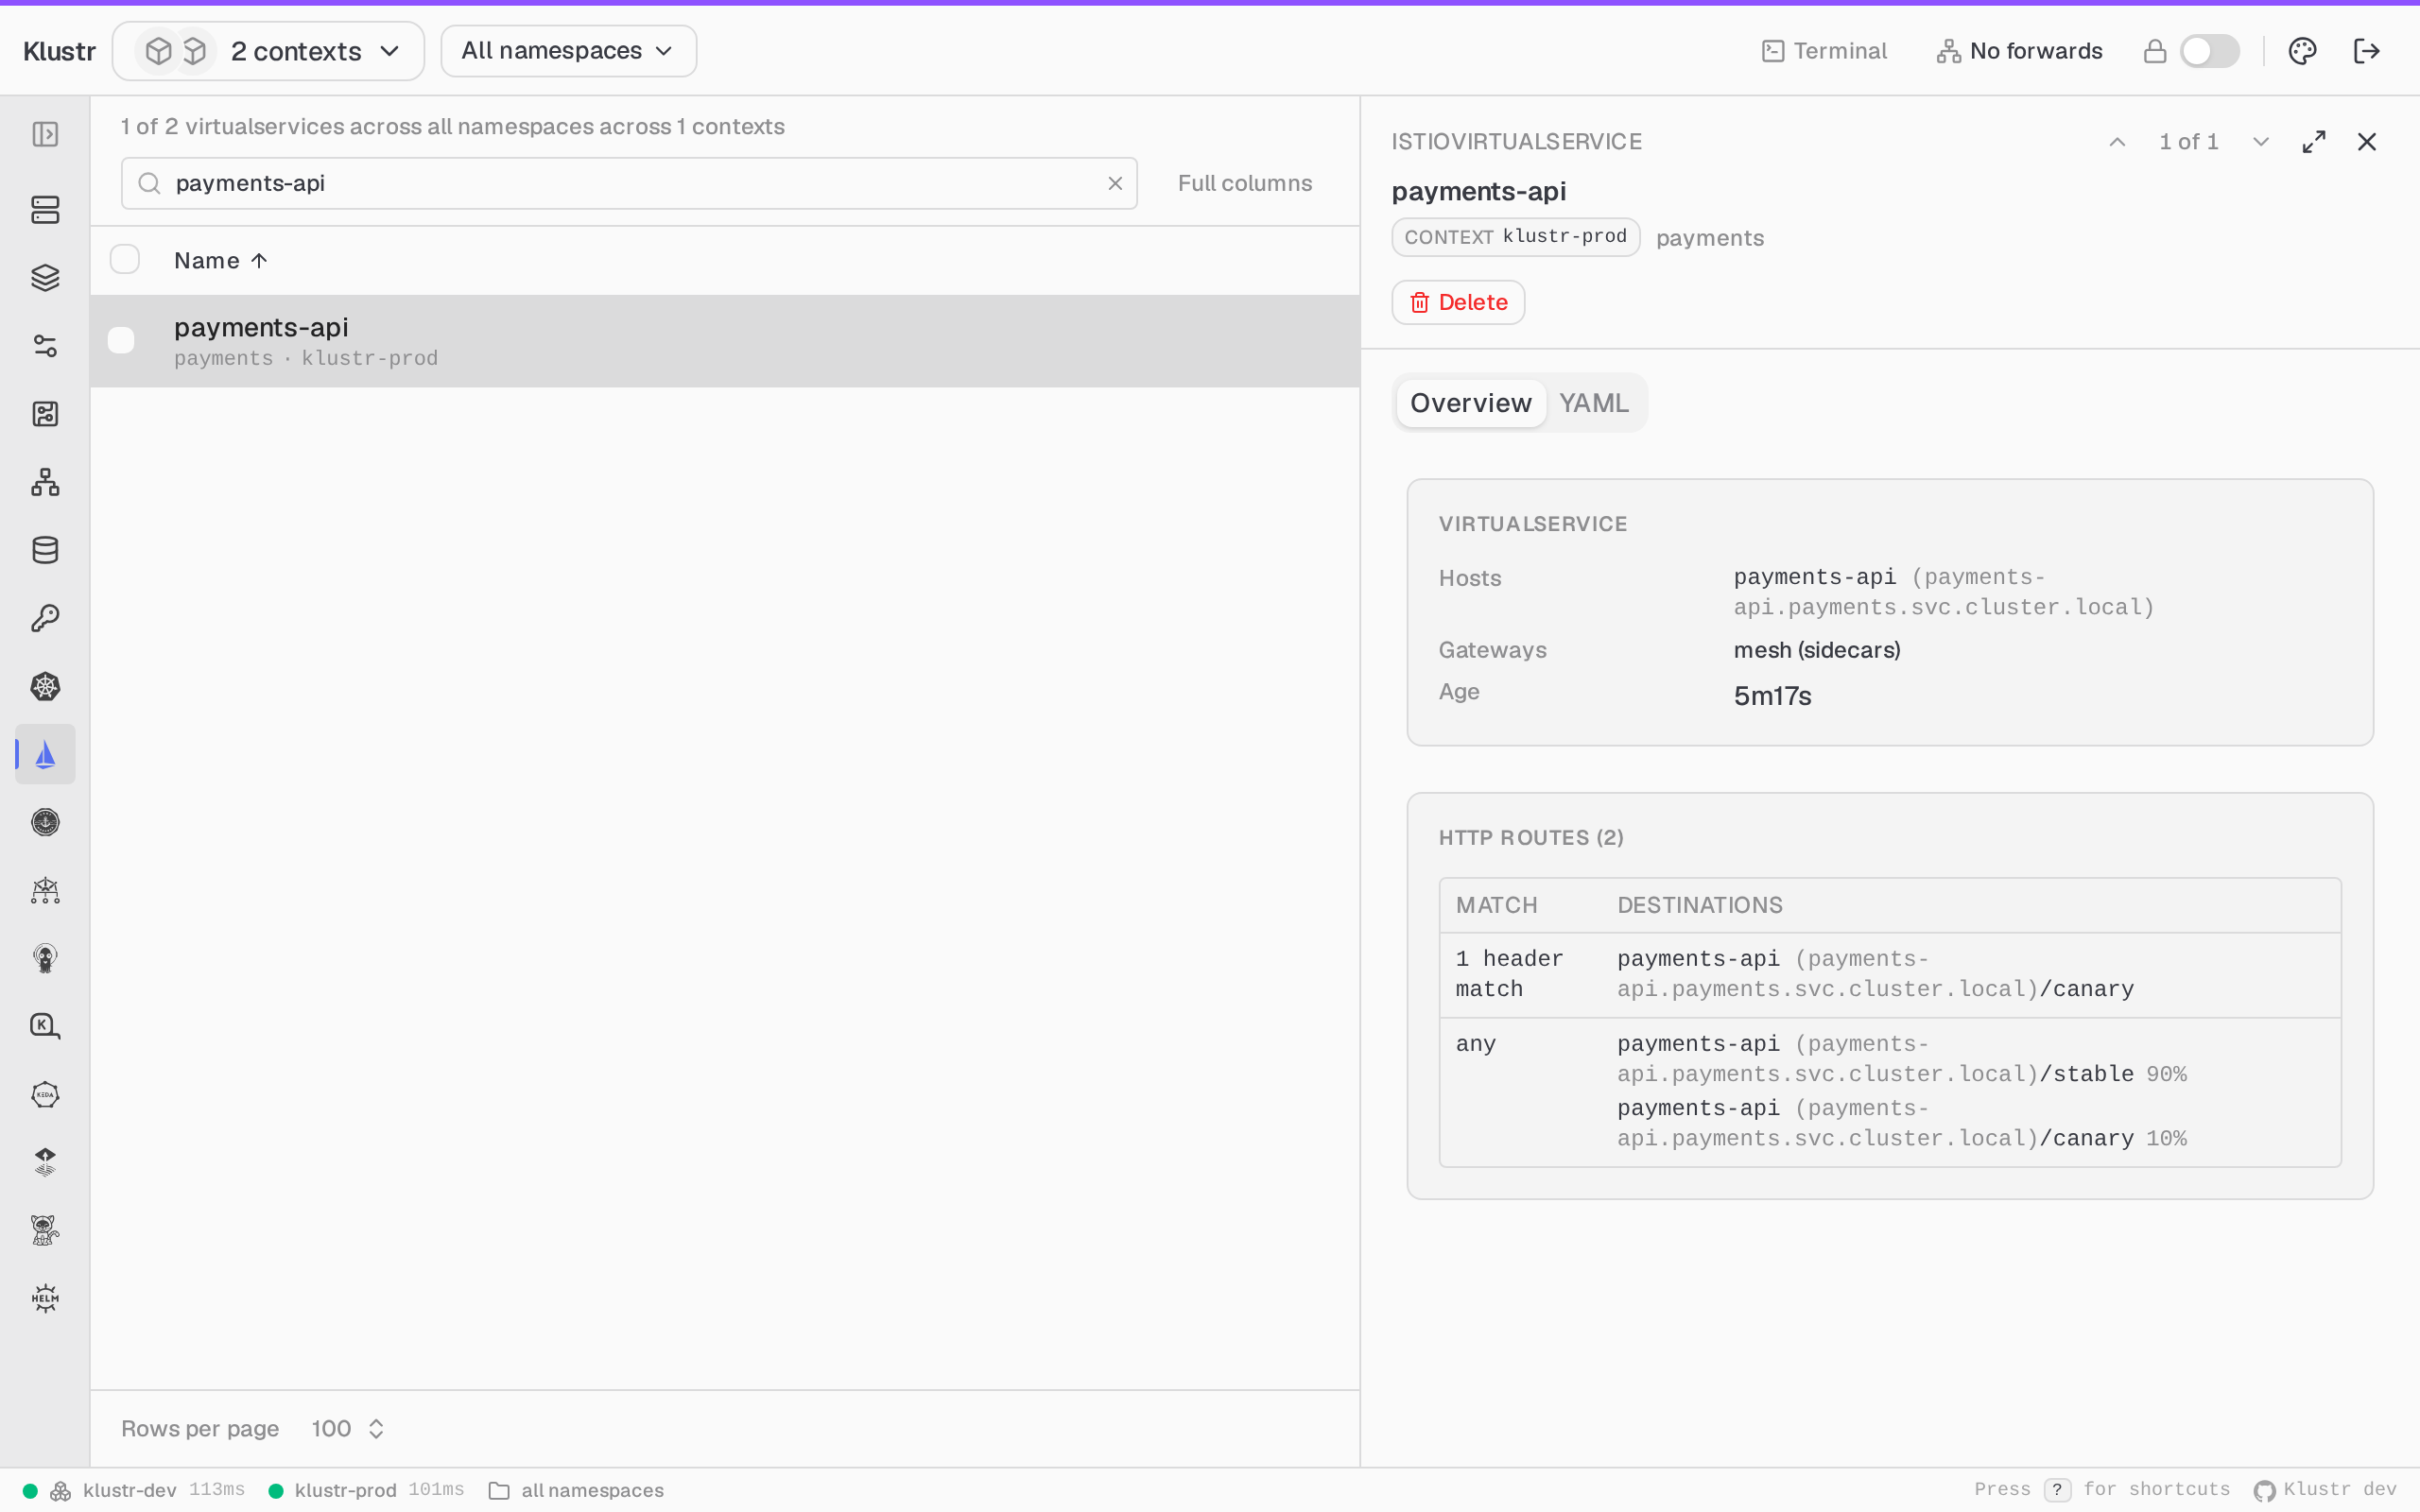
cmctlCLI. - 🕸️ Istio. VirtualServices, DestinationRules and PeerAuthentications, watch-backed; the served API version is read from the discovered CRD rather than hardcoded.
- Cilium. Dedicated views for network policies, endpoints, nodes, identities, CIDR groups, LoadBalancer IP pools, L2 announcement and egress gateway policies, and BGP configuration. Read policy rules, IP allocation and reported BGP peer status directly from CRDs, with links to referenced resources.
- 🌳 Karpenter. NodePools, NodeClaims and AWS EC2NodeClasses, surfaced automatically when their CRDs are present. Follow a pool or claim to its node class and inspect resolved subnets, security groups, AMIs and their requirements, IAM configuration and readiness conditions.
- 🛡️ Kyverno. ClusterPolicies, Policies, CEL ValidatingPolicies, PolicyExceptions and
wgpolicyk8s.iopolicy reports. Each policy lists the resources it fails, and a resource's detail shows its own report. - 📜 Logs. Stern-style multi-pod streaming with per-pod ANSI colors, follow, save and regex.
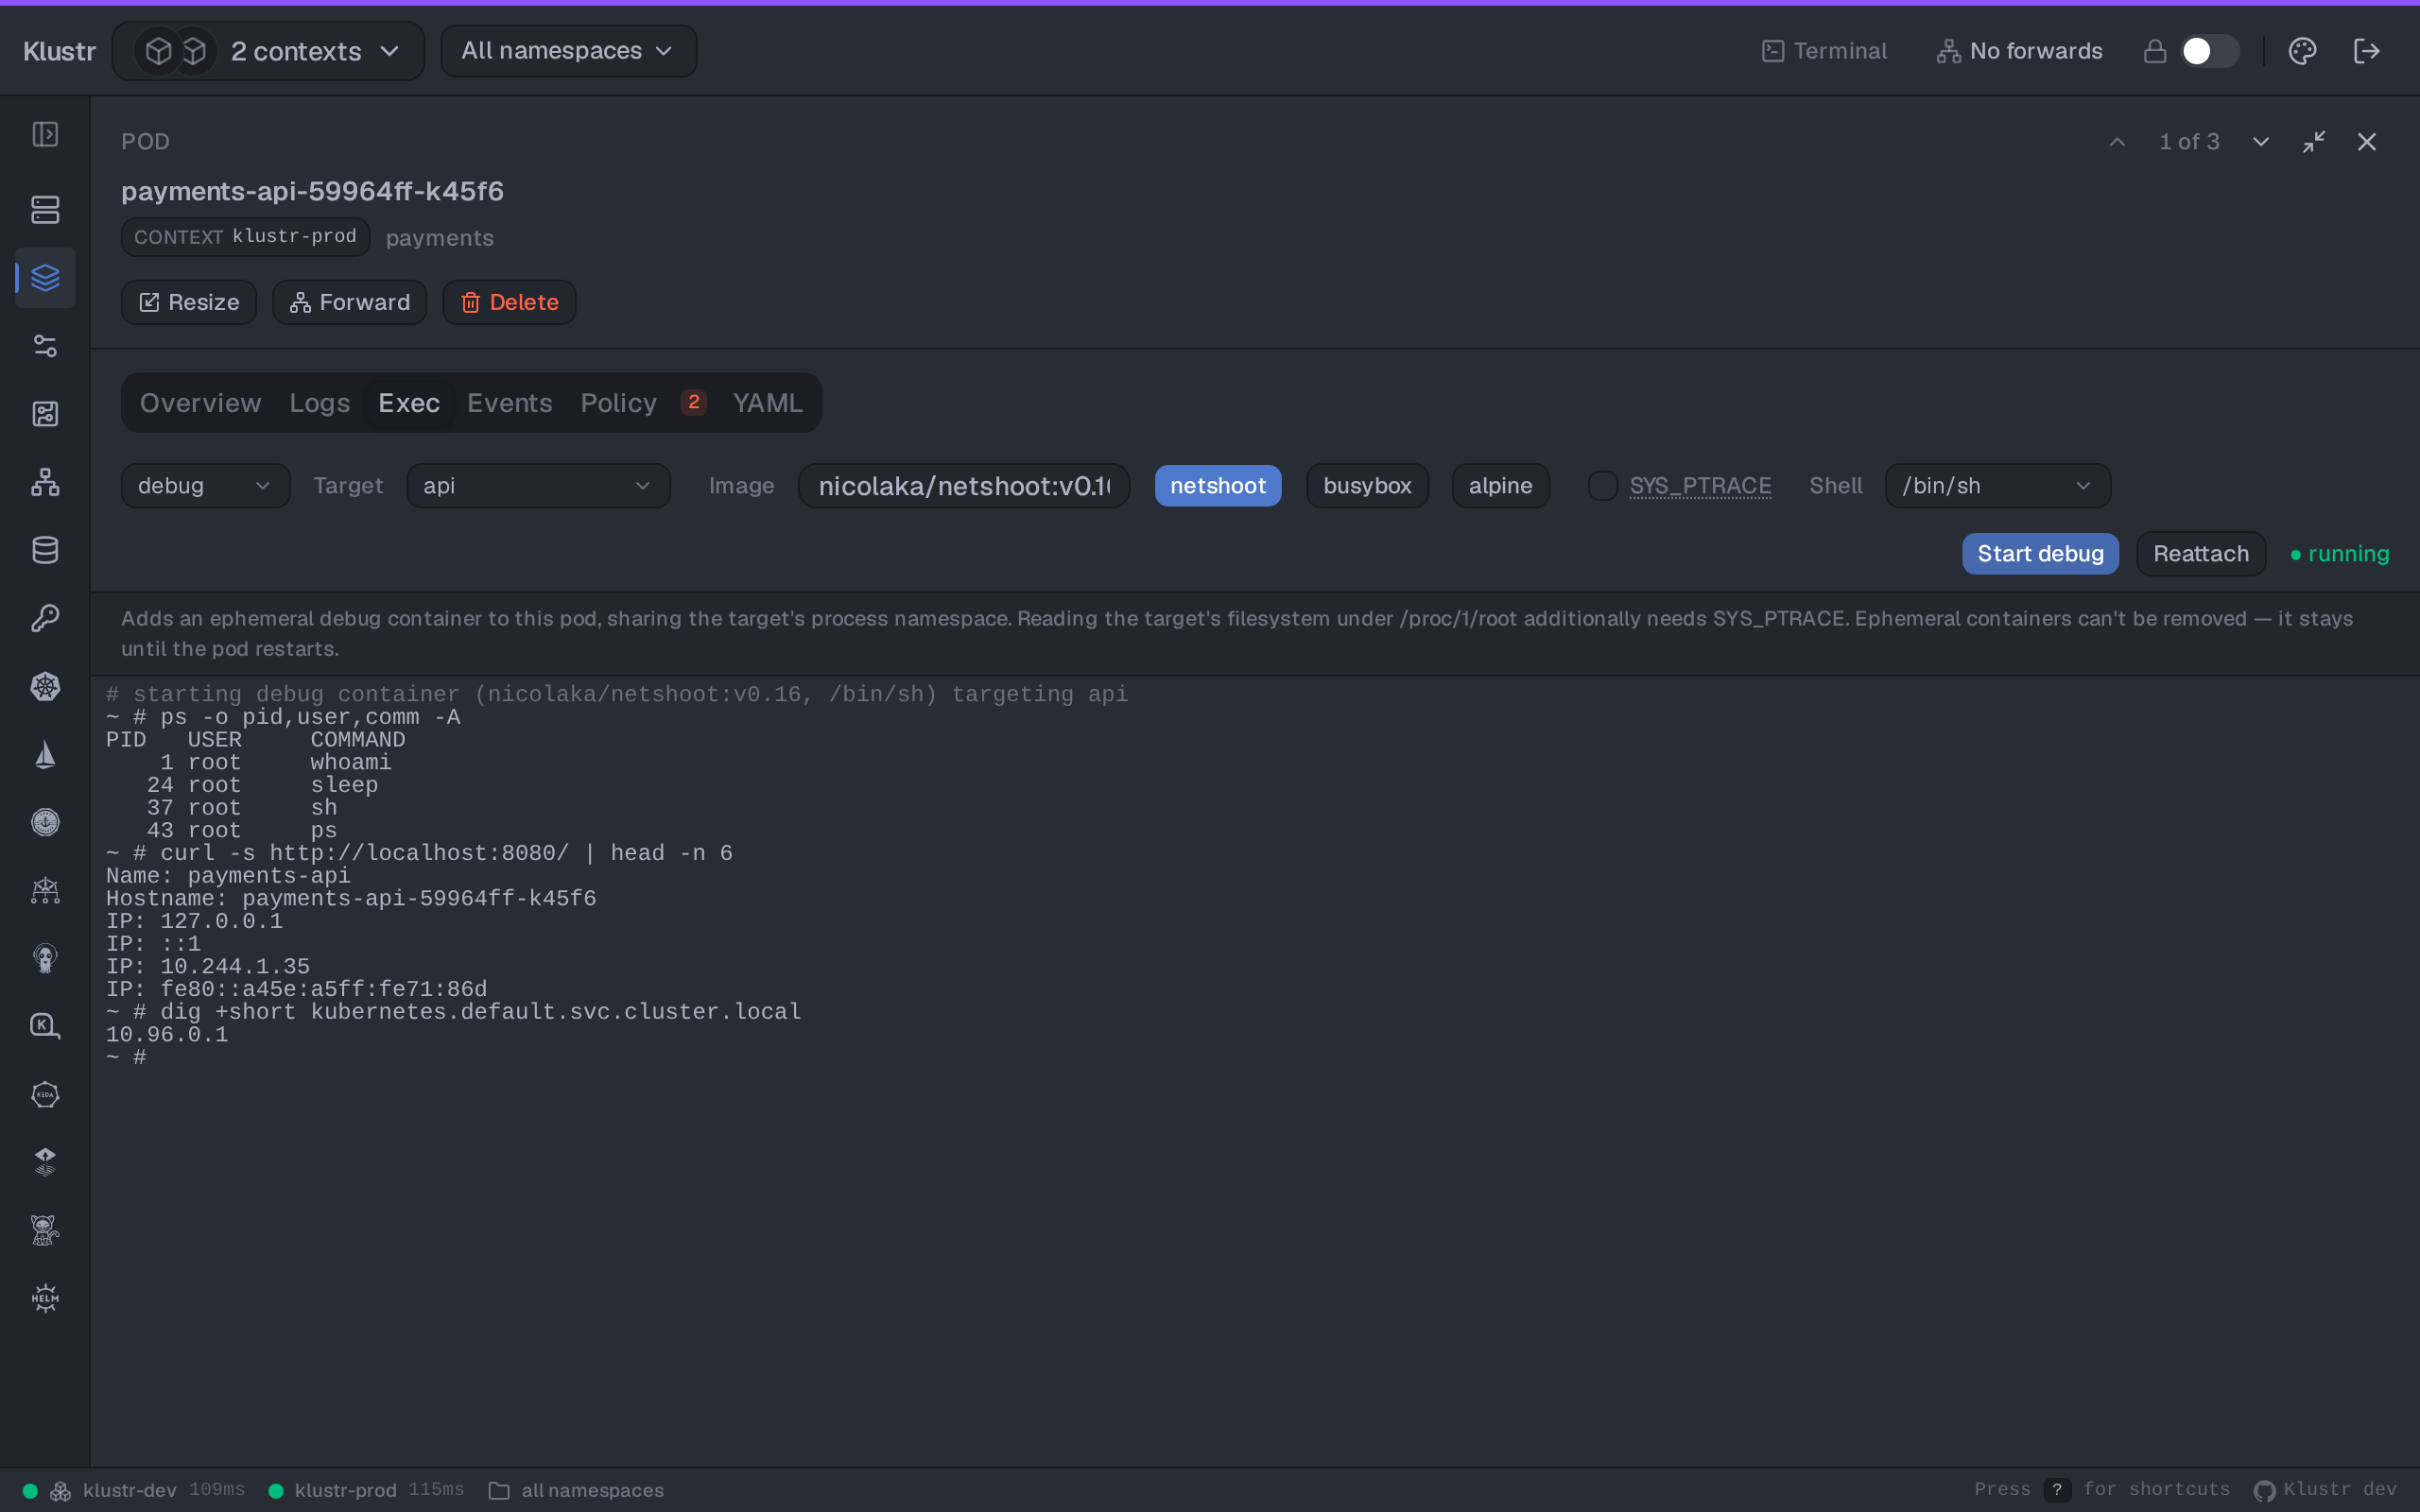
- 🖥️ In-app exec. SPDY shell into any container.
- 🐚 Node shell. Root shell on any node via a temporary privileged
nsenterpod that's removed when the session ends — no SSH, nothing pre-installed. - 🚧 Cordon & drain. One-click cordon/uncordon and a live-progress drain that evicts through the Eviction API (PDB-aware, skips DaemonSet & mirror pods).
- 🔧 YAML edit. Monaco editor with a server-side dry-run diff before apply.
- 🚀 Scale, restart, pause/resume. Replica controls, one-click rolling restart, inline pause/resume, HPA min/max editable inline.
- 📐 In-place pod resize. Change a running container's CPU / memory requests and limits via the
pods/resizesubresource — no pod recreation; shows the live resize status (Deferred / Infeasible). - ⏪ Rollout history & rollback. Side-by-side template diff and one-click revert on Deployments / StatefulSets / DaemonSets.
- 🔄 Port-forwarding. Suggested local ports, persistent header indicator, click-to-open in browser.
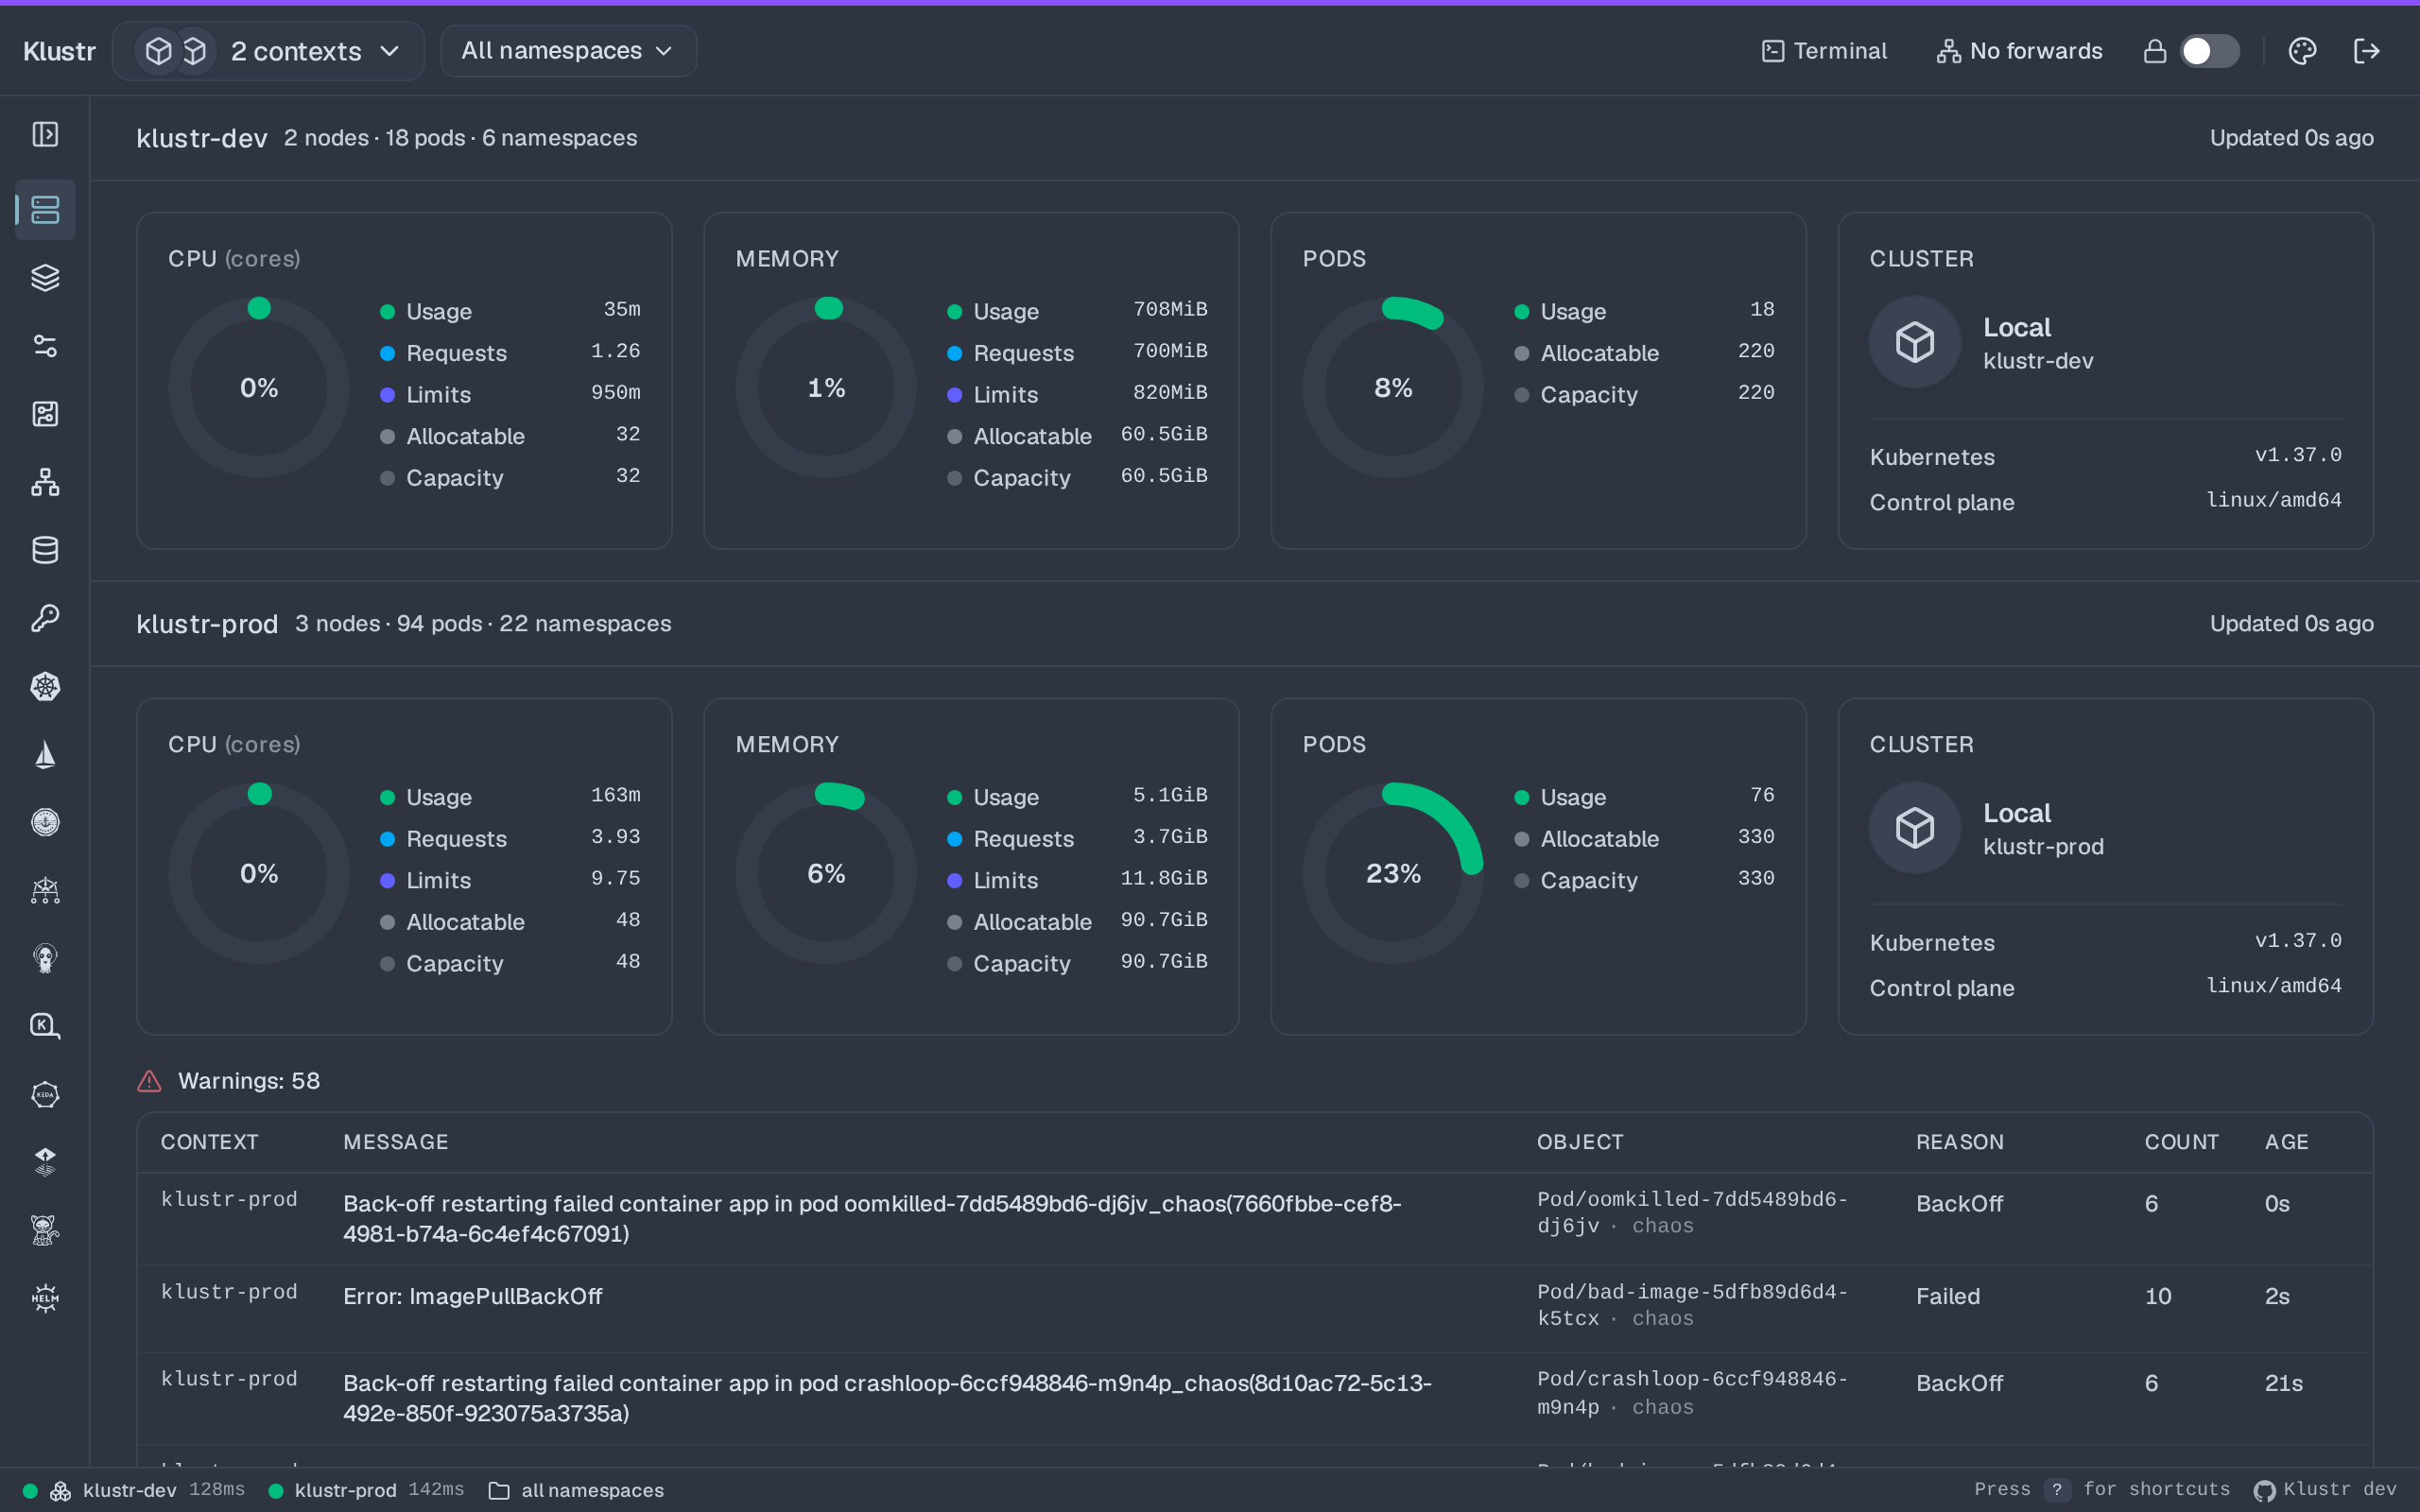
- 🗺️ Cluster overviews. CPU / memory / pod donuts, workloads health, recent warnings — single-cluster or aggregated.
- 🧭 Cross-resource navigation. Drill from workload to pod to node and back.
- 🎨 Themes & shortcuts. Command palette (
⌘K), pod search (⌘P), namespace search (⌘N), keyboard cheatsheet (?).
Screenshots
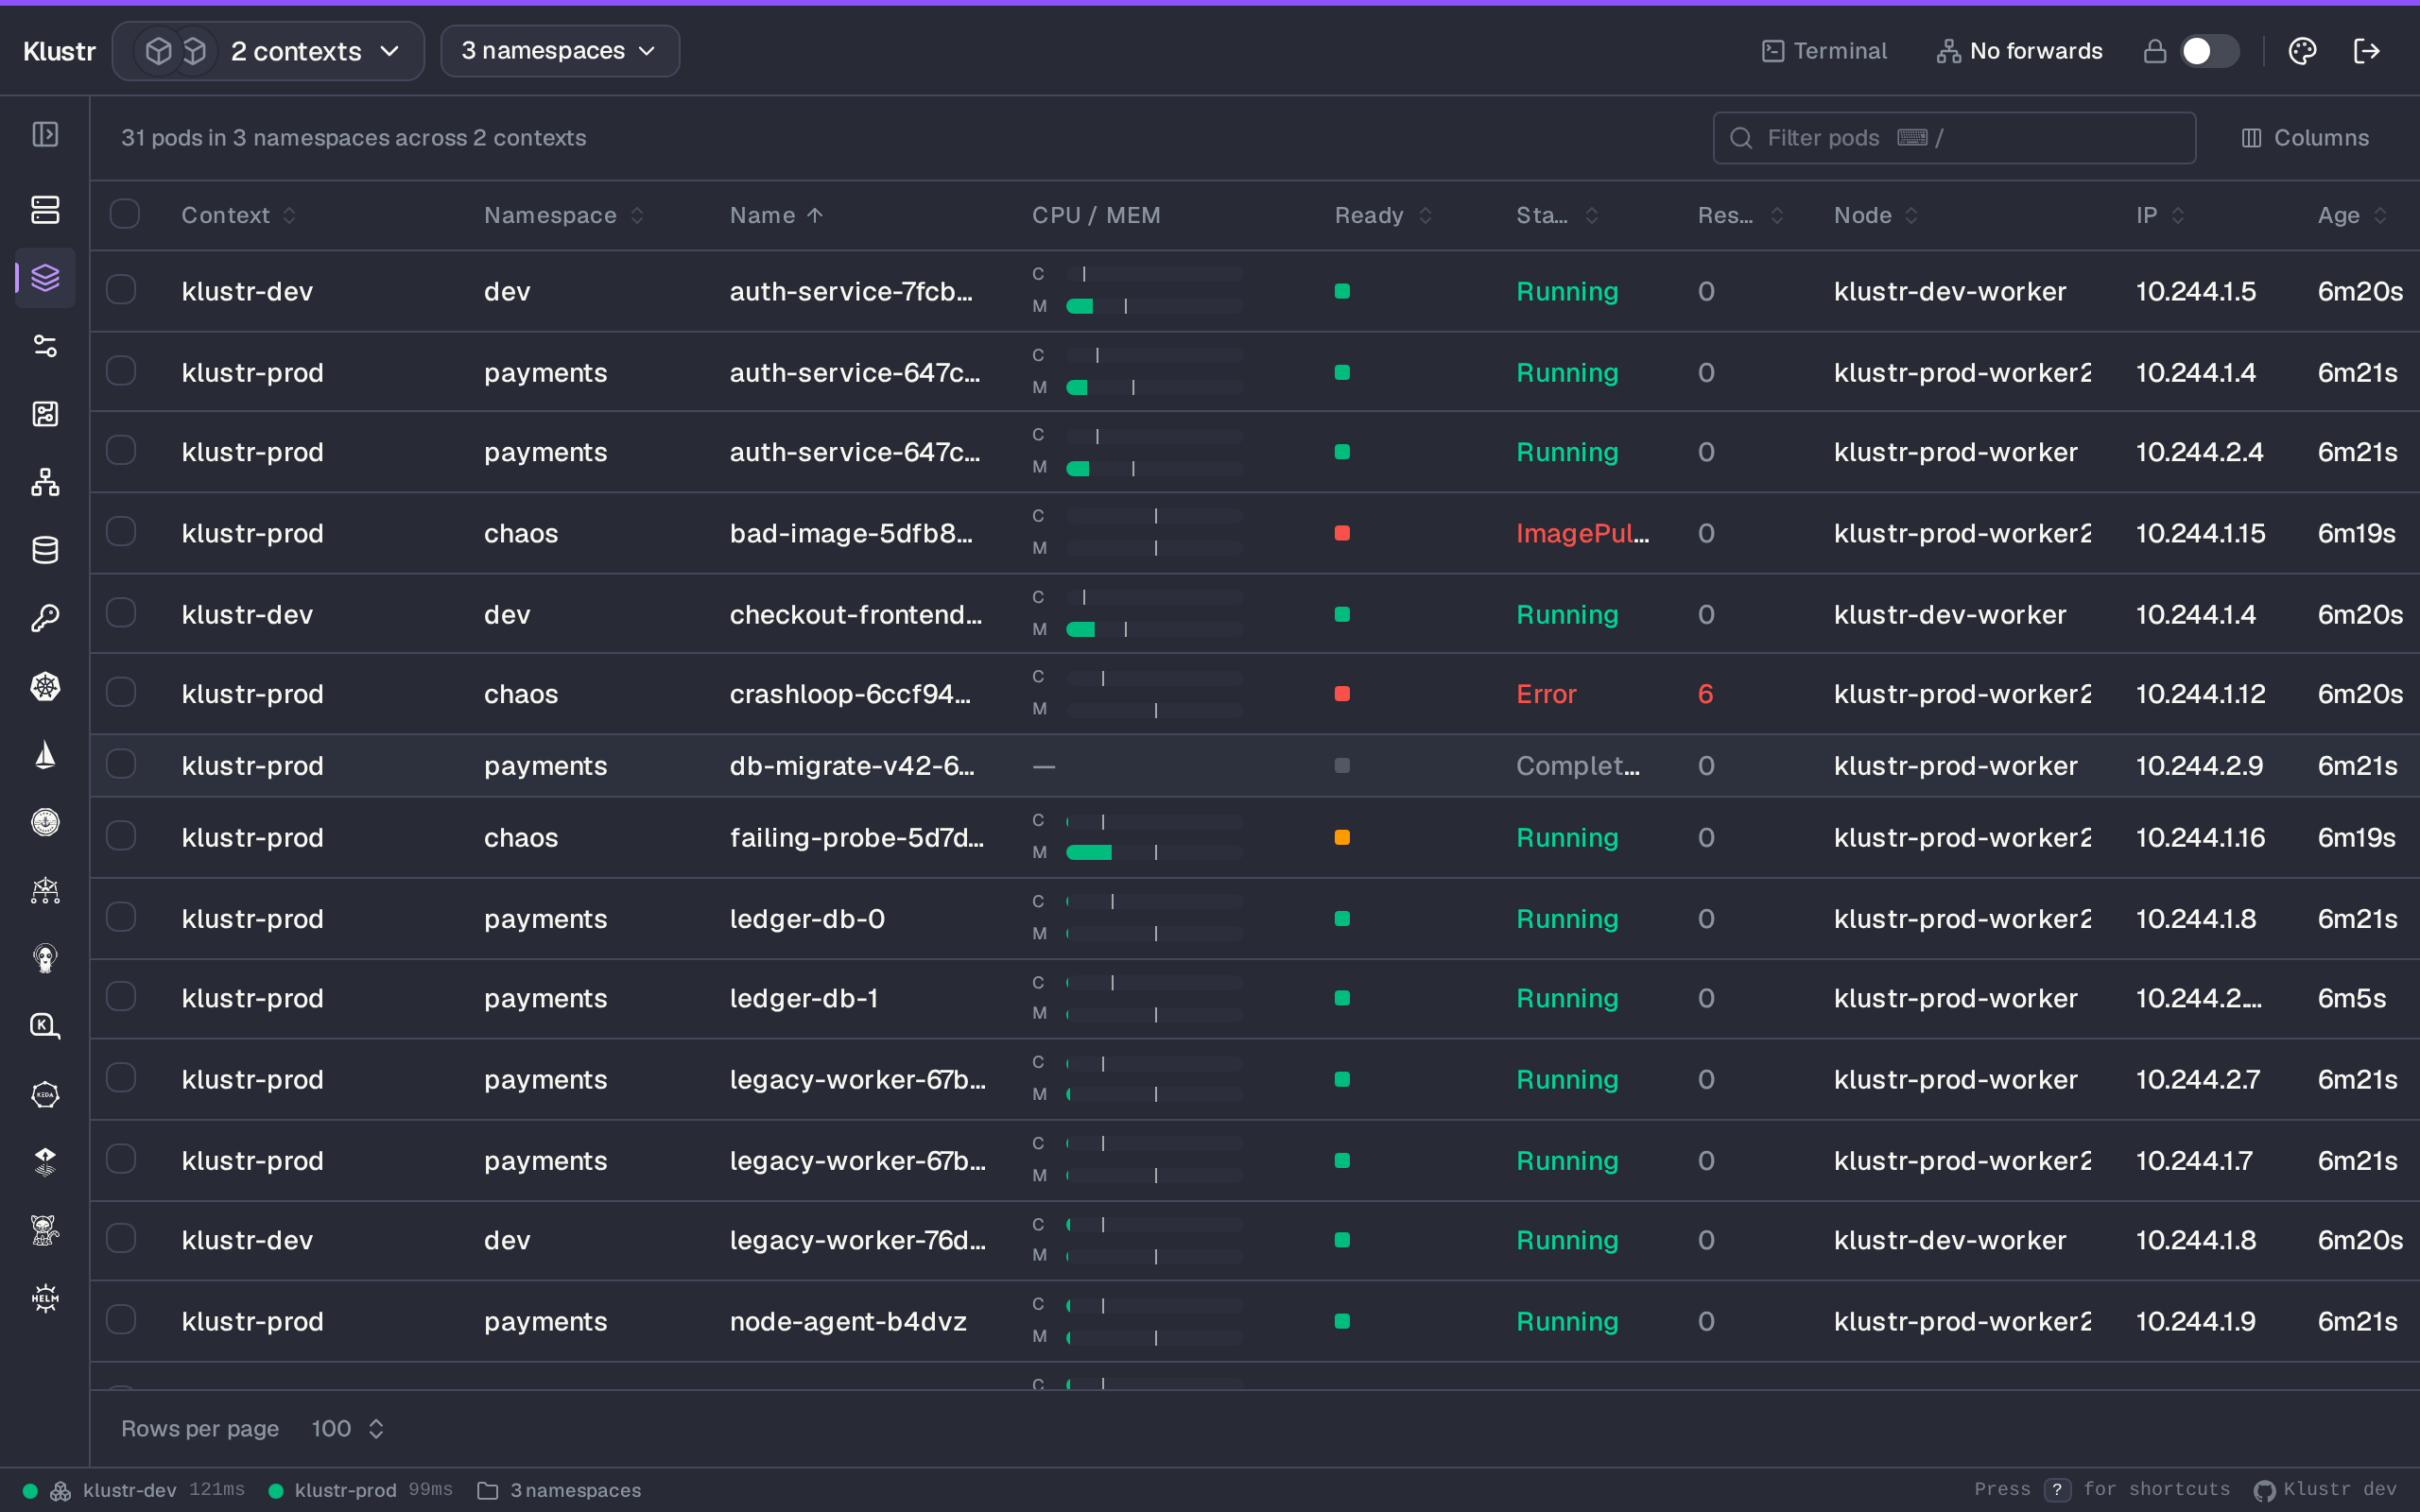
Every shot is captured from two kind clusters seeded with realistic workloads and deliberate failures. The shots cycle through Klustr's themes, so the pack doubles as a tour of them — see docs/screenshots/ for the full set.
 |
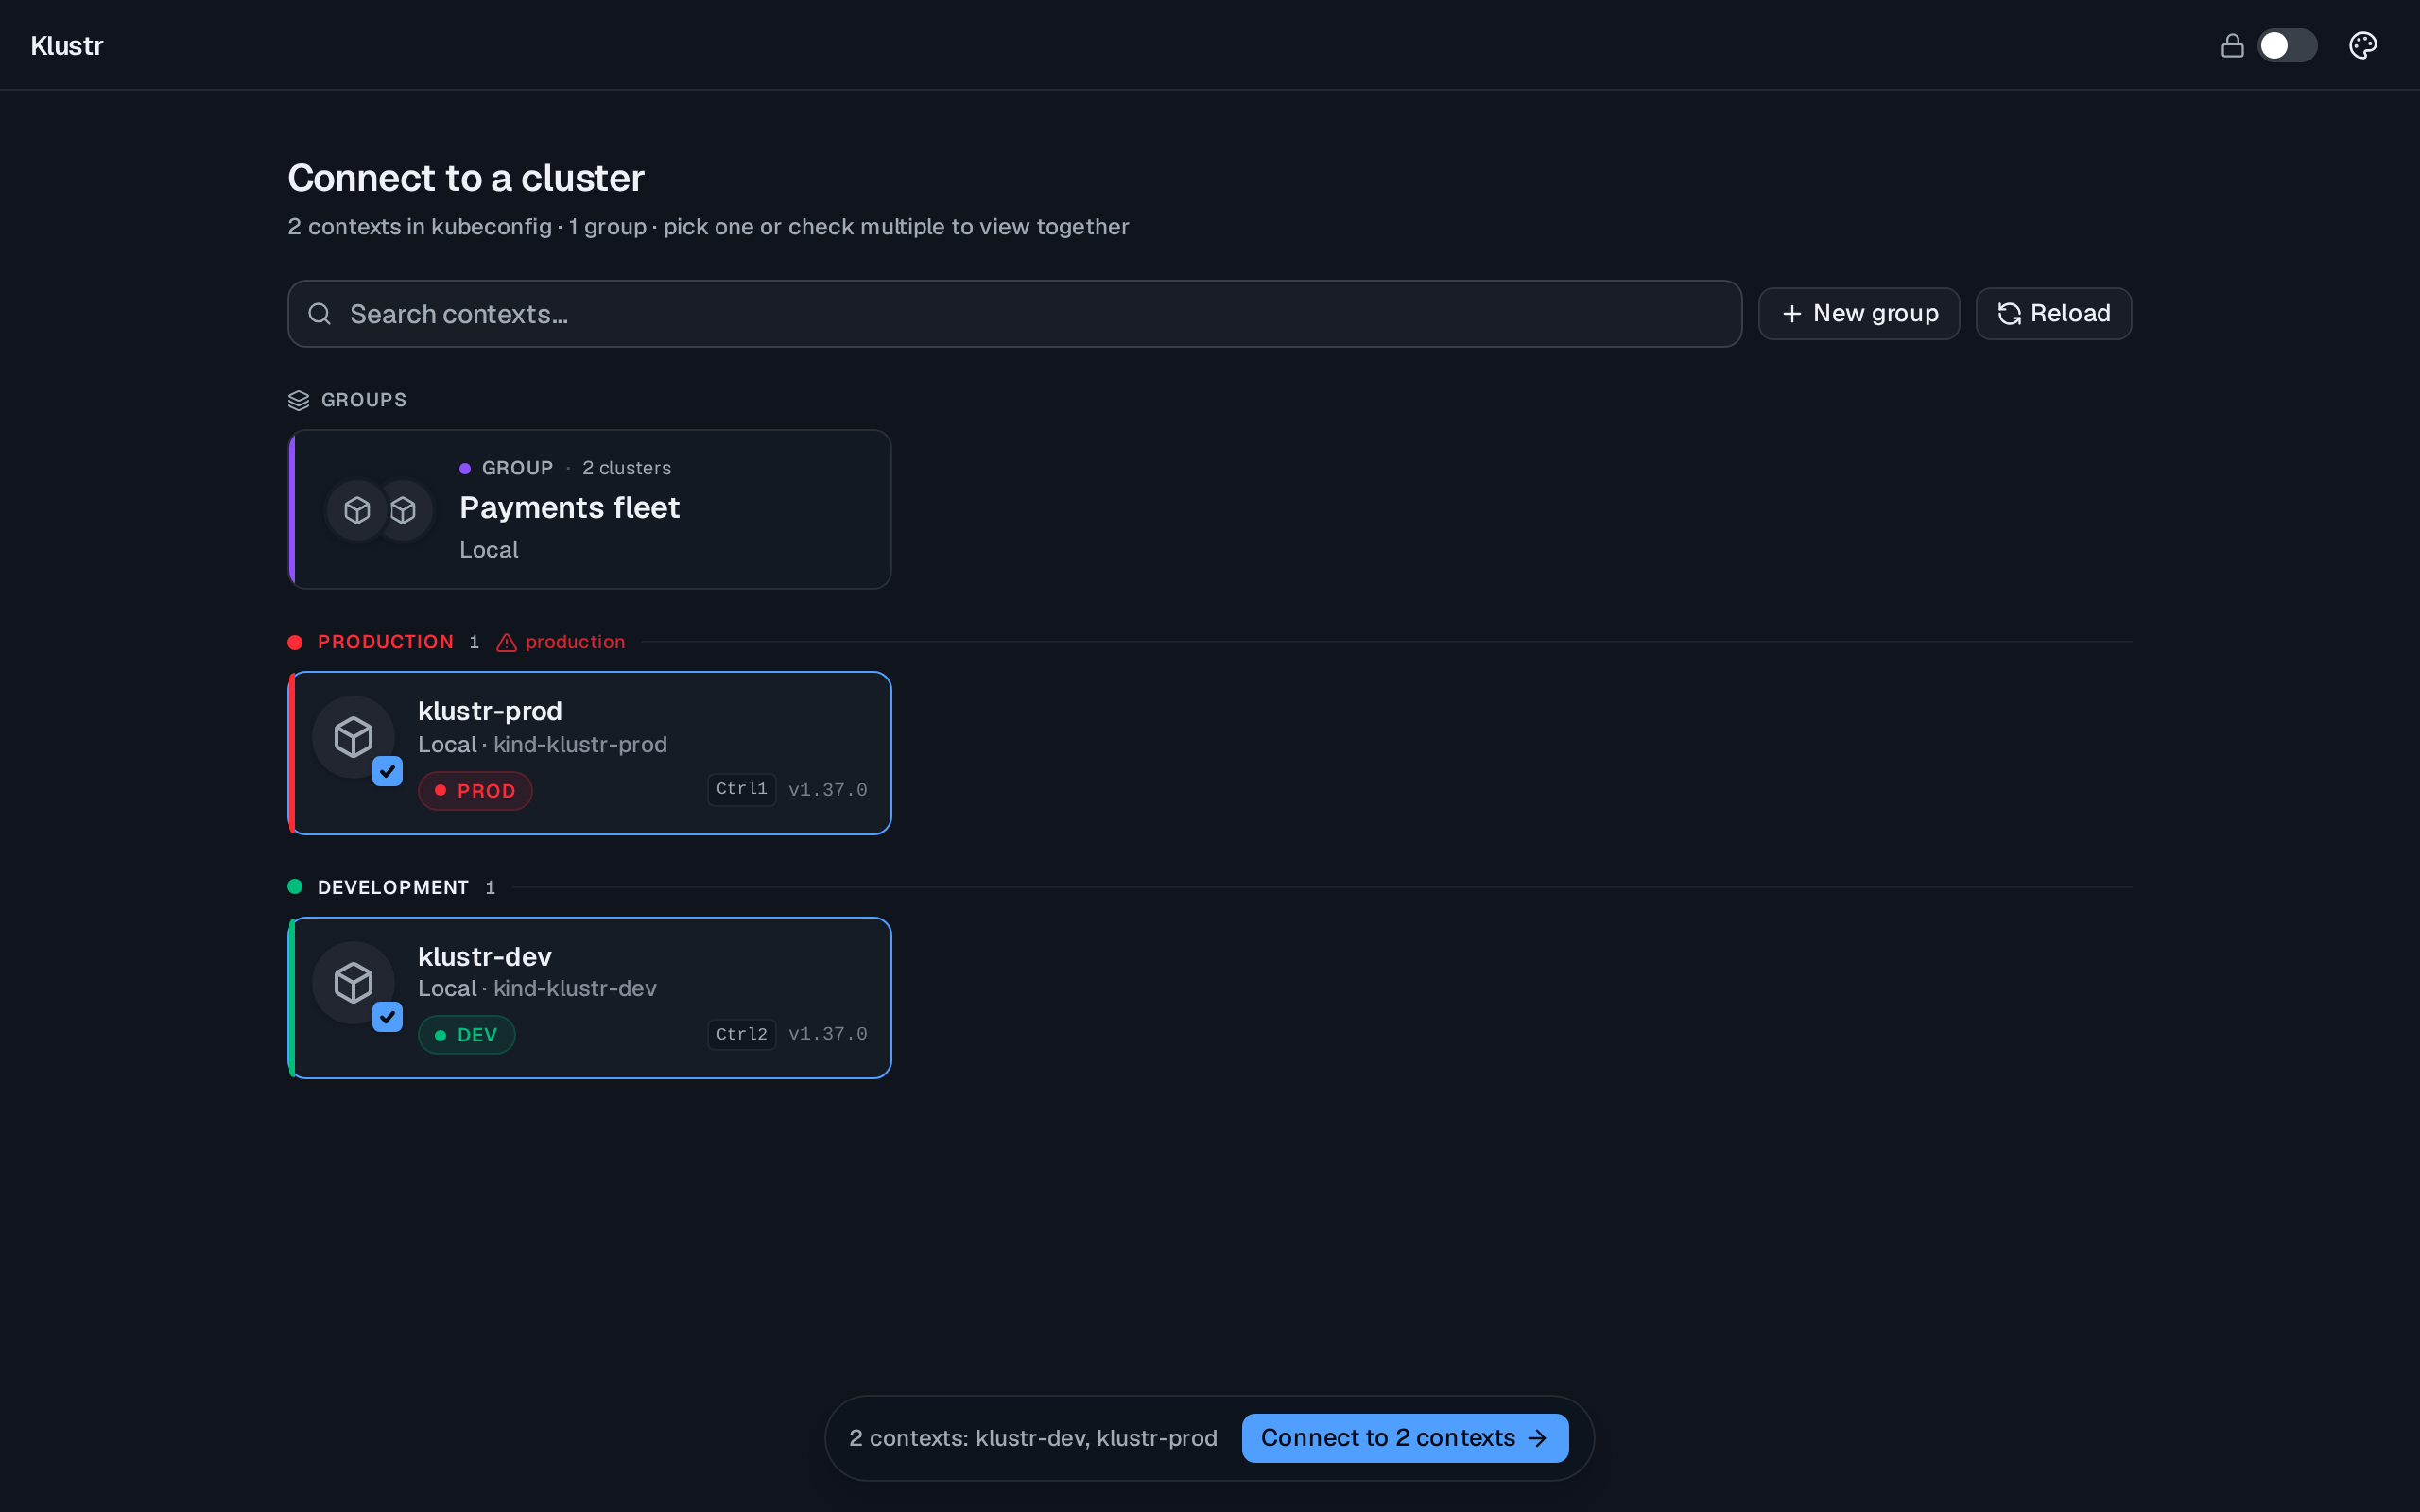 |
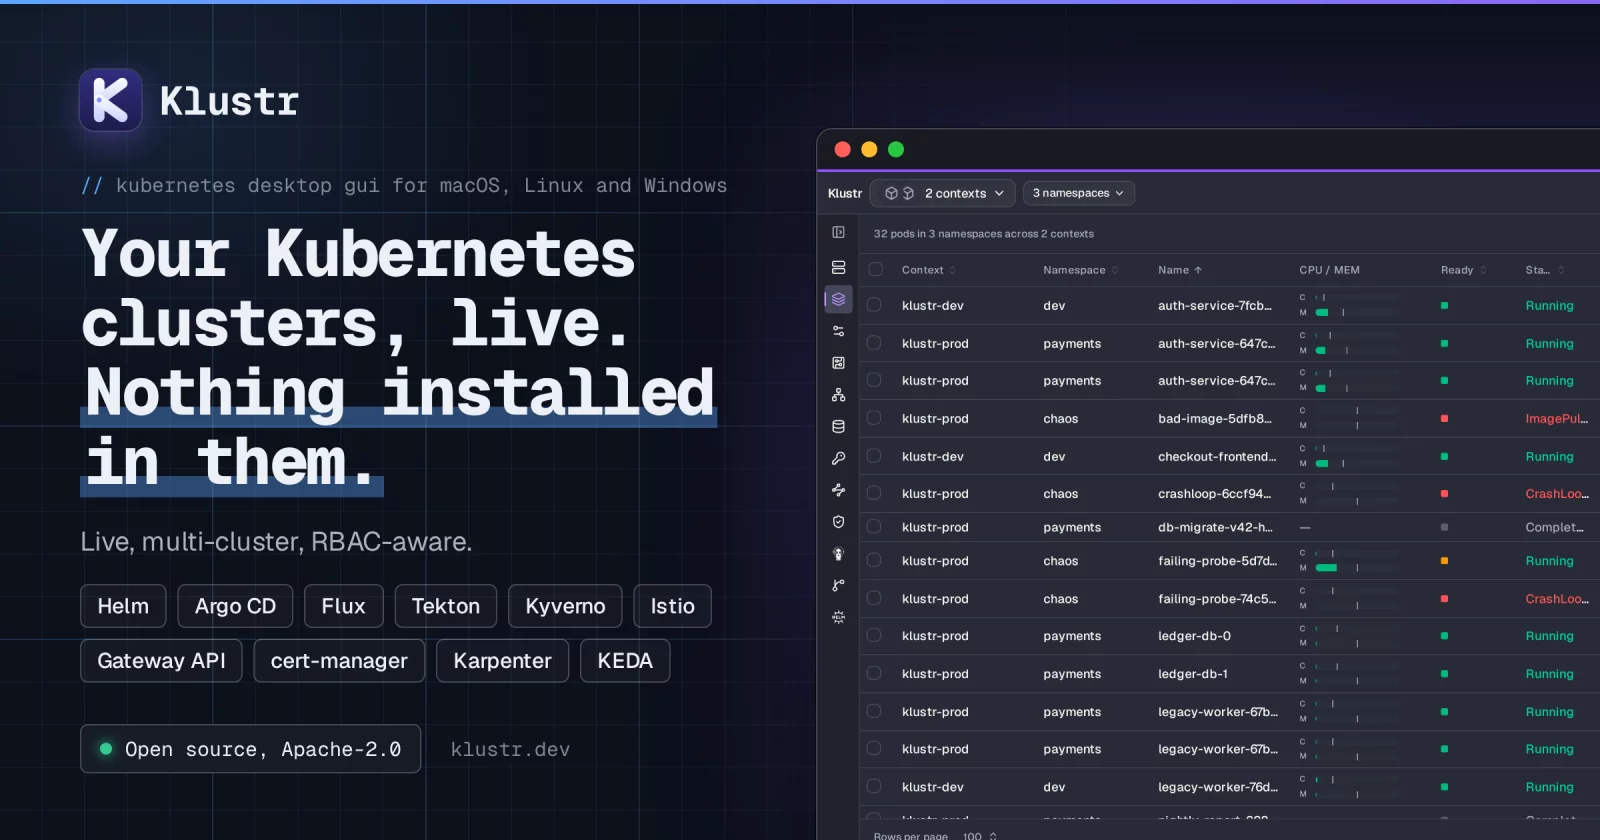
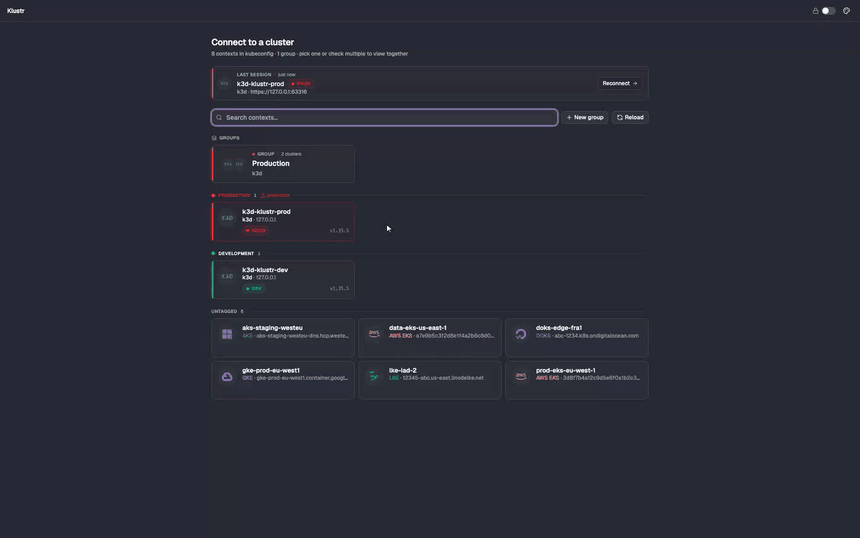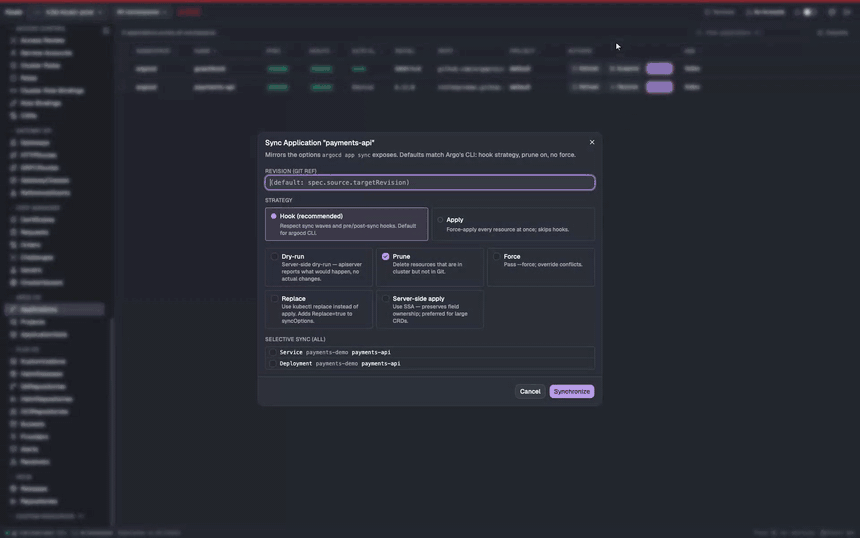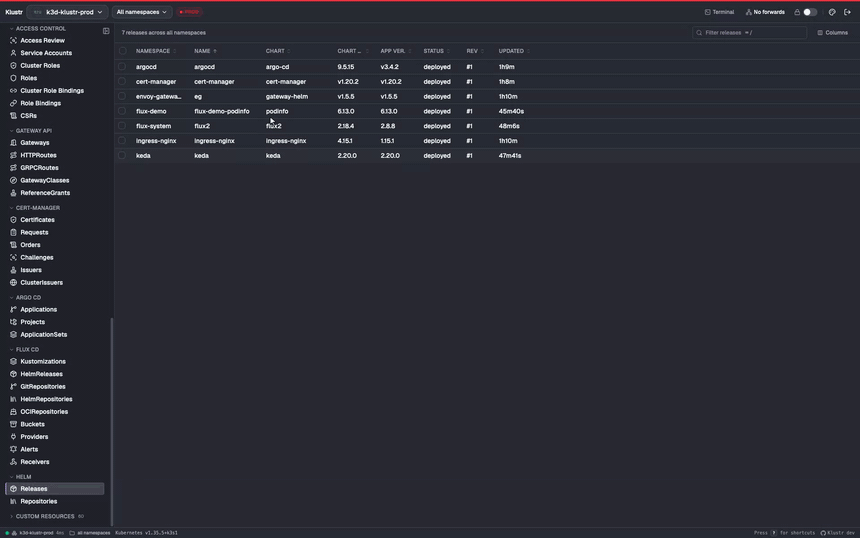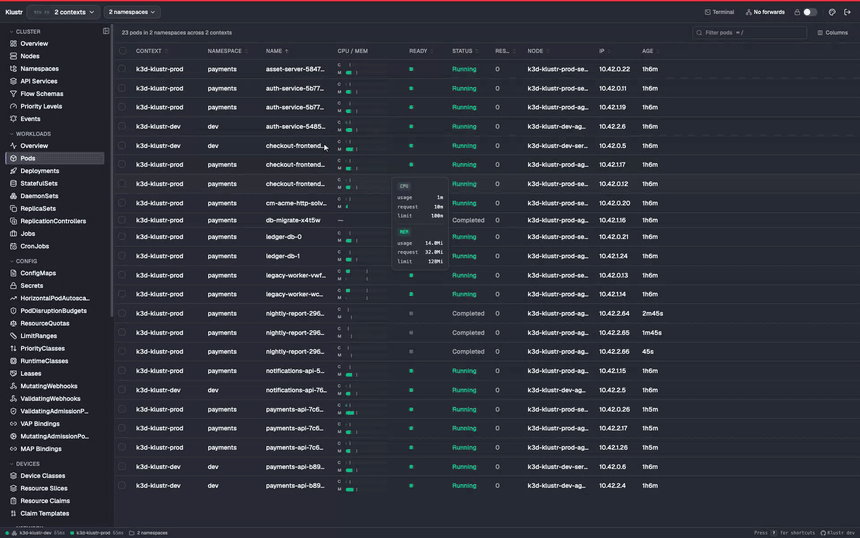
| Aggregated pods — two clusters and three namespaces in one table; failing pods sit next to the healthy rows | Connections — contexts grouped by tag, two checked for an aggregated session, a saved group for one-click reconnect |
 |
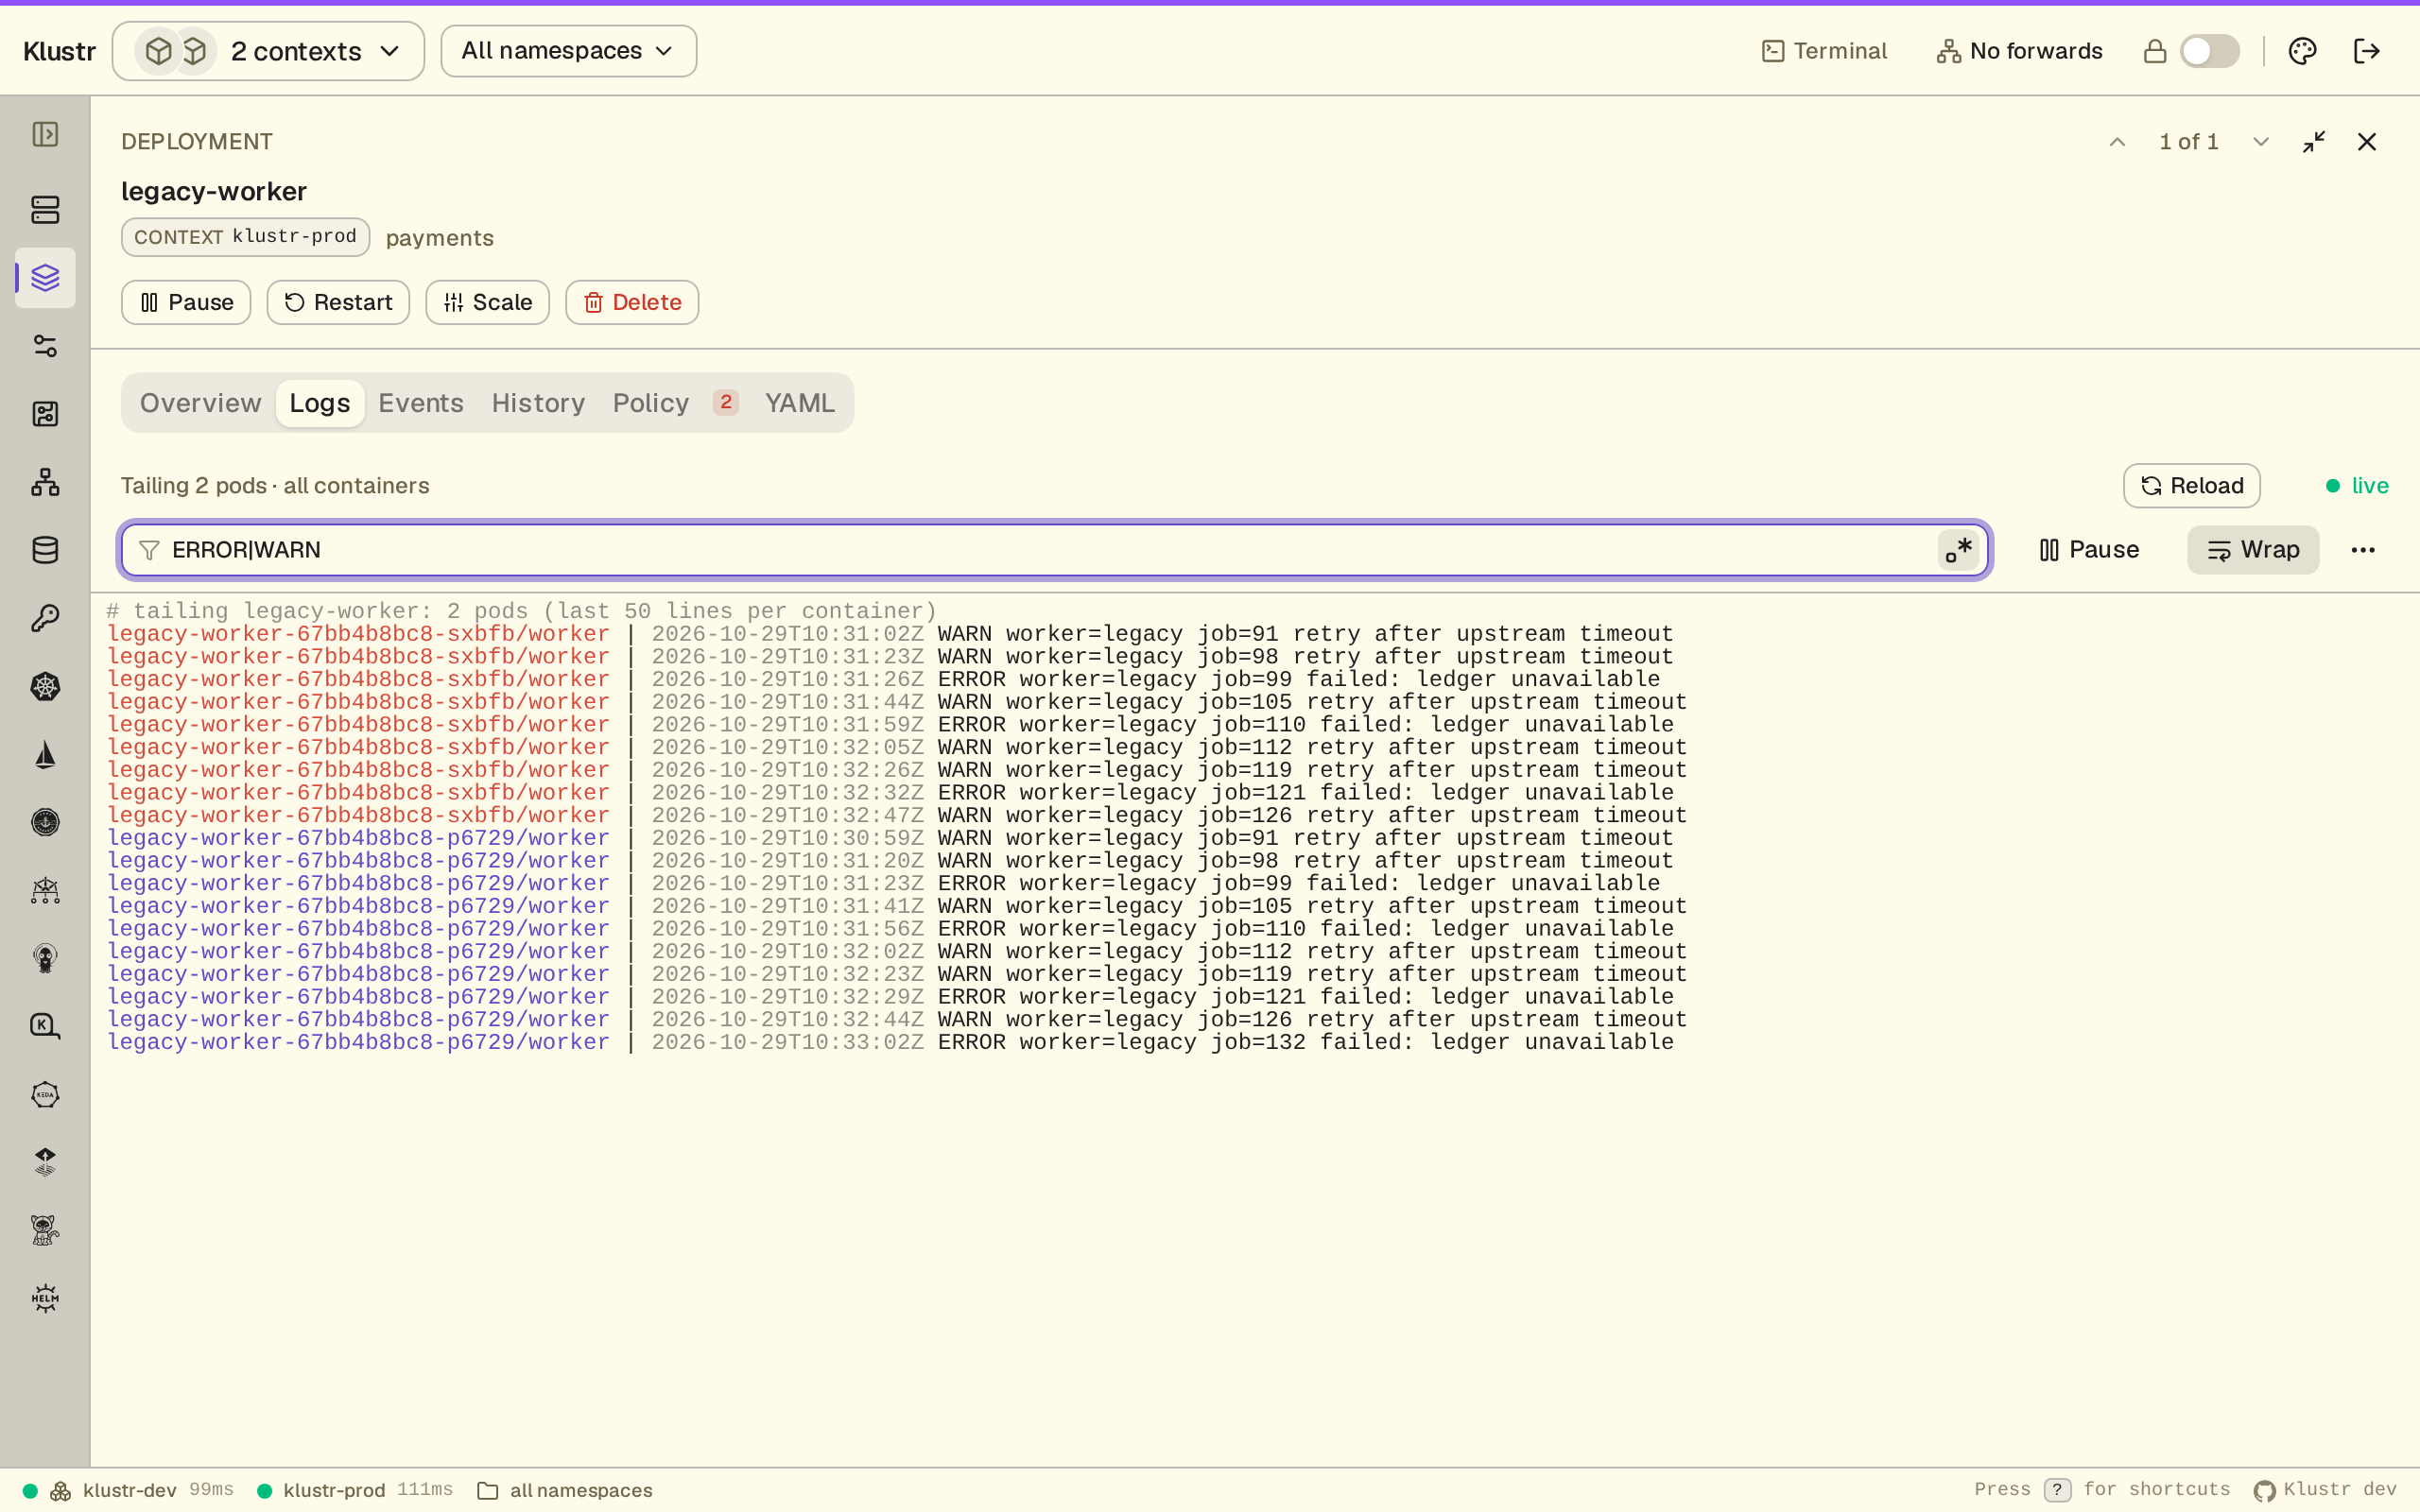 |
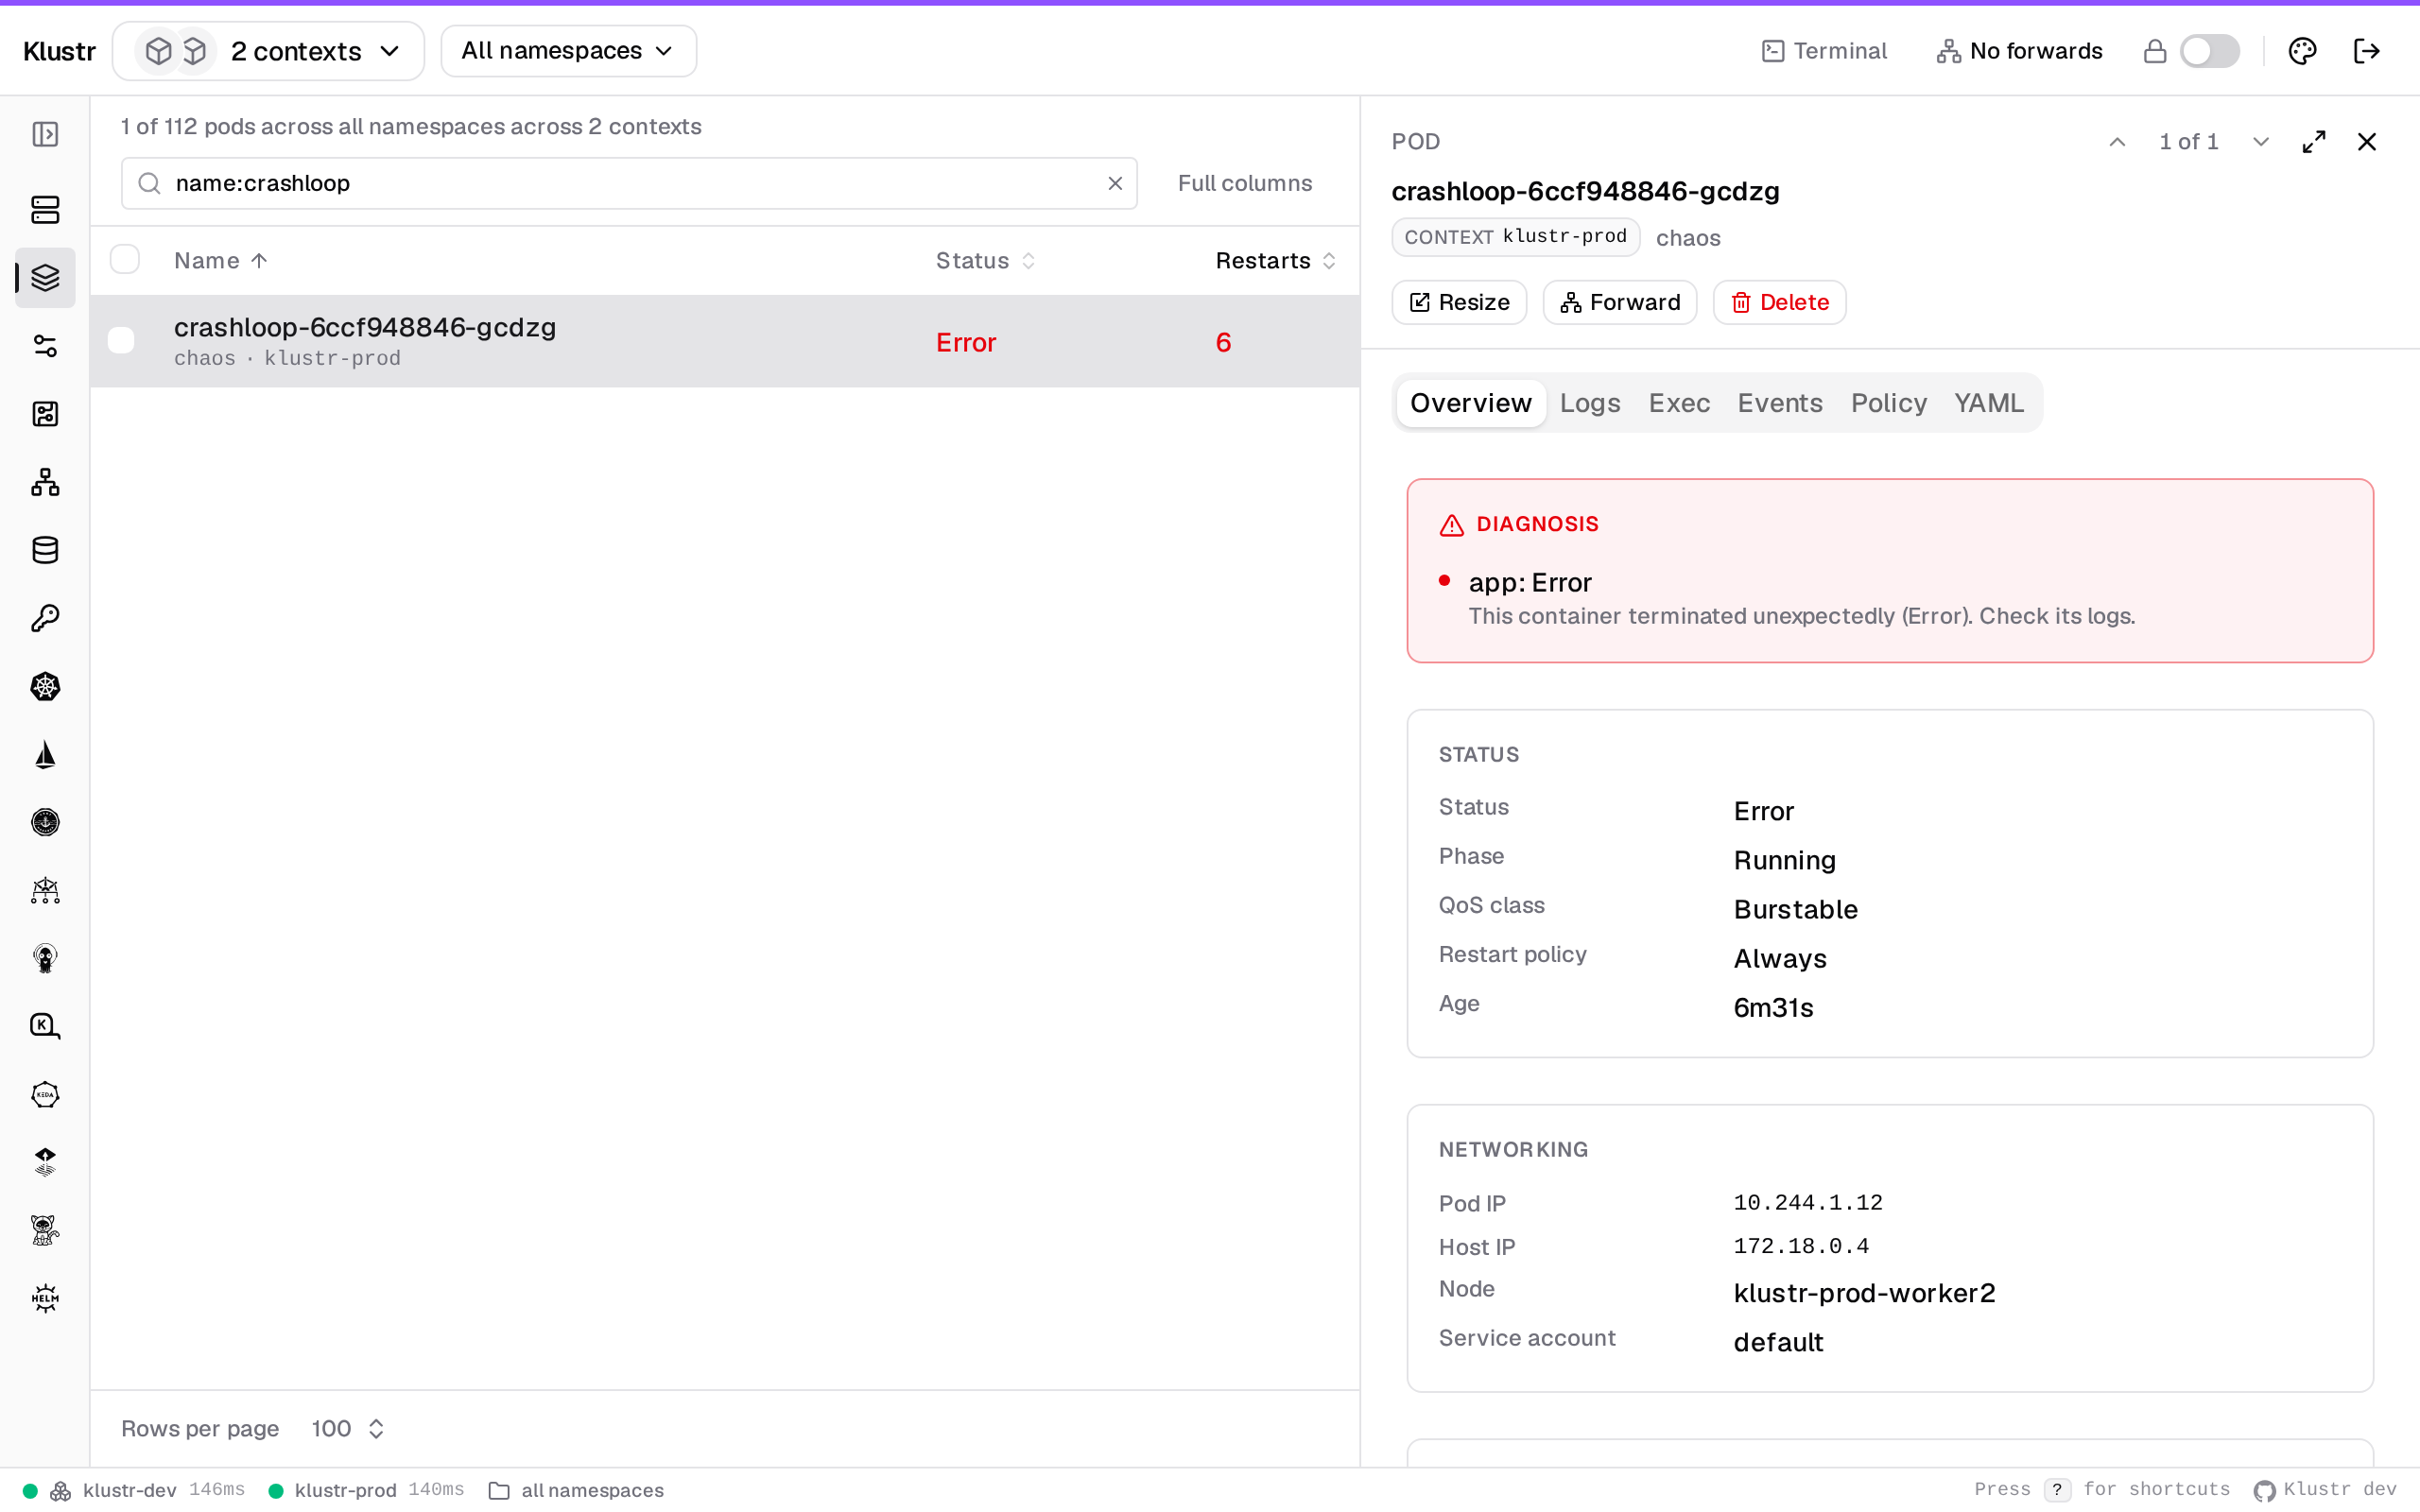
| Pod diagnosis — a card that says why the pod is unhealthy and what to check next | Multi-pod logs — one stream across a Deployment, a color per pod, live regex filter |
 |
 |
Debug container — netshoot injected into a shell-less pod, ps / curl / dig against the target |
Helm upgrade — values on the left, the dry-run rendered manifest on the right, apply only after reading it |
 |
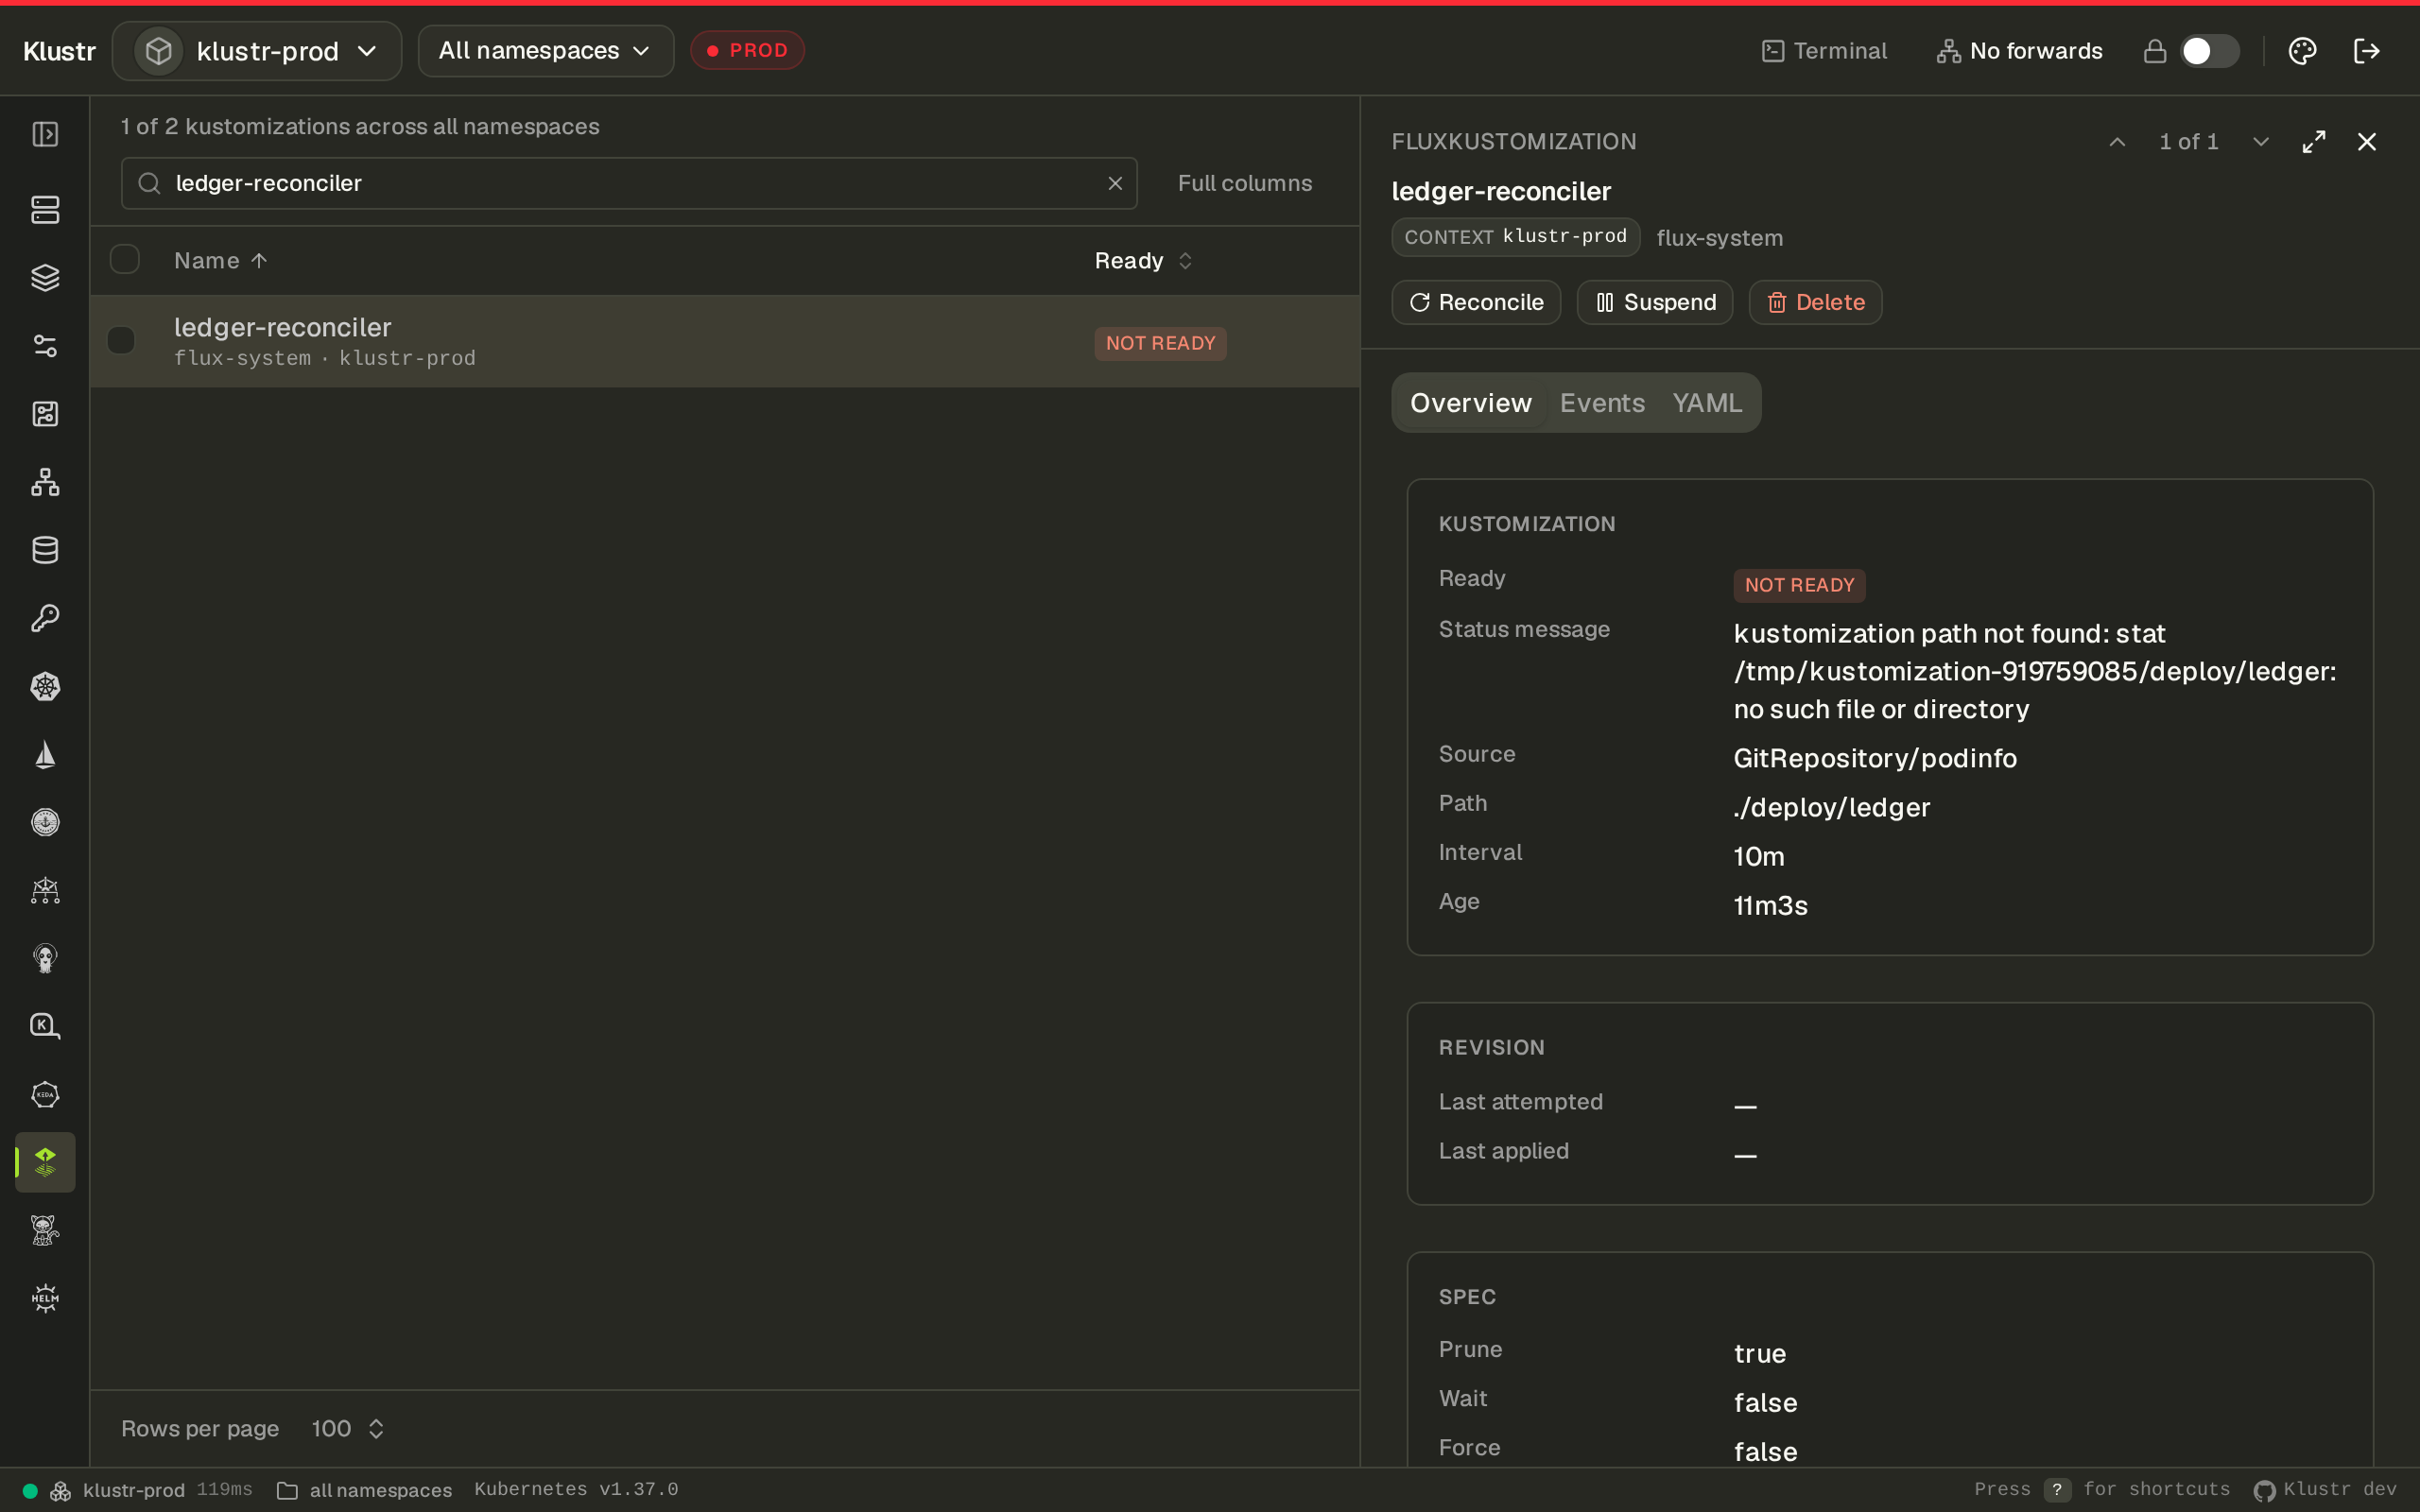 |
| Argo CD — Sync / Health pills, per-row Refresh, Suspend and Sync through the Kubernetes API | Flux CD — a failed Kustomization with its status message, source and path readable without YAML |
 |
 |
Gateway API — rule matrix plus RouteParentStatus: Accepted, but ResolvedRefs=False with RefNotPermitted |
cert-manager — Certificate → CertificateRequest → Order → Challenge, with the ACME self-check error |
 |
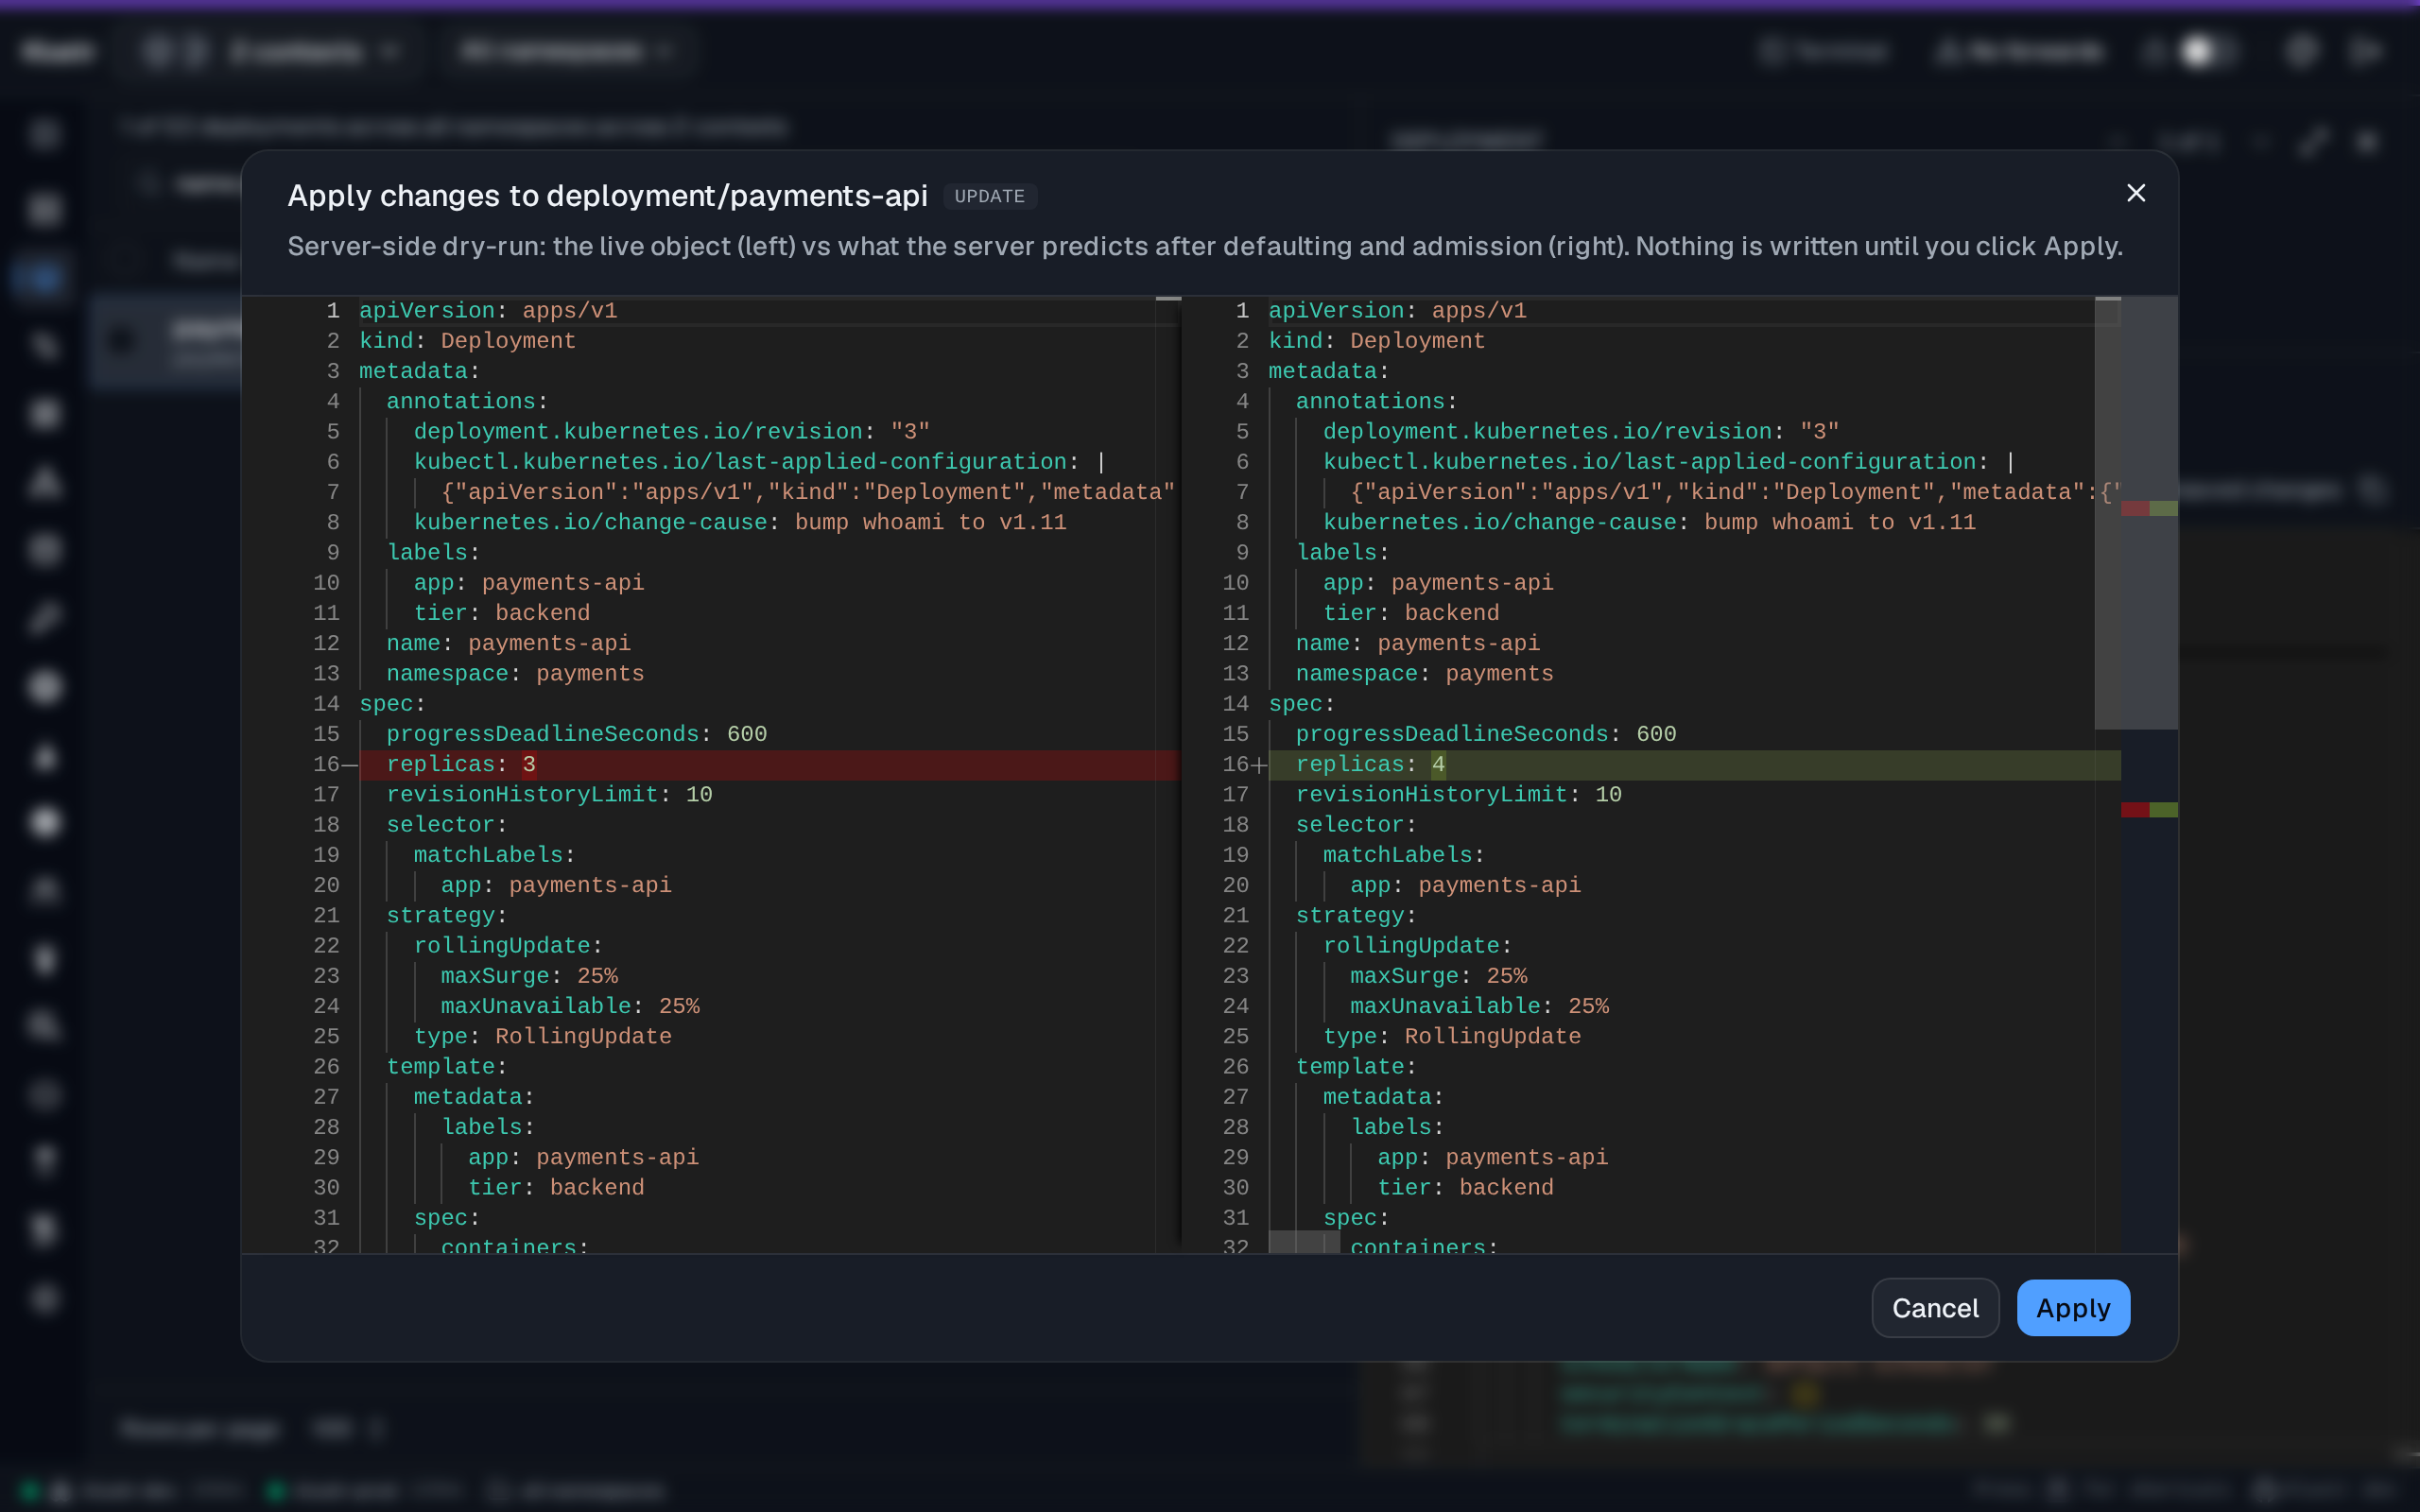 |
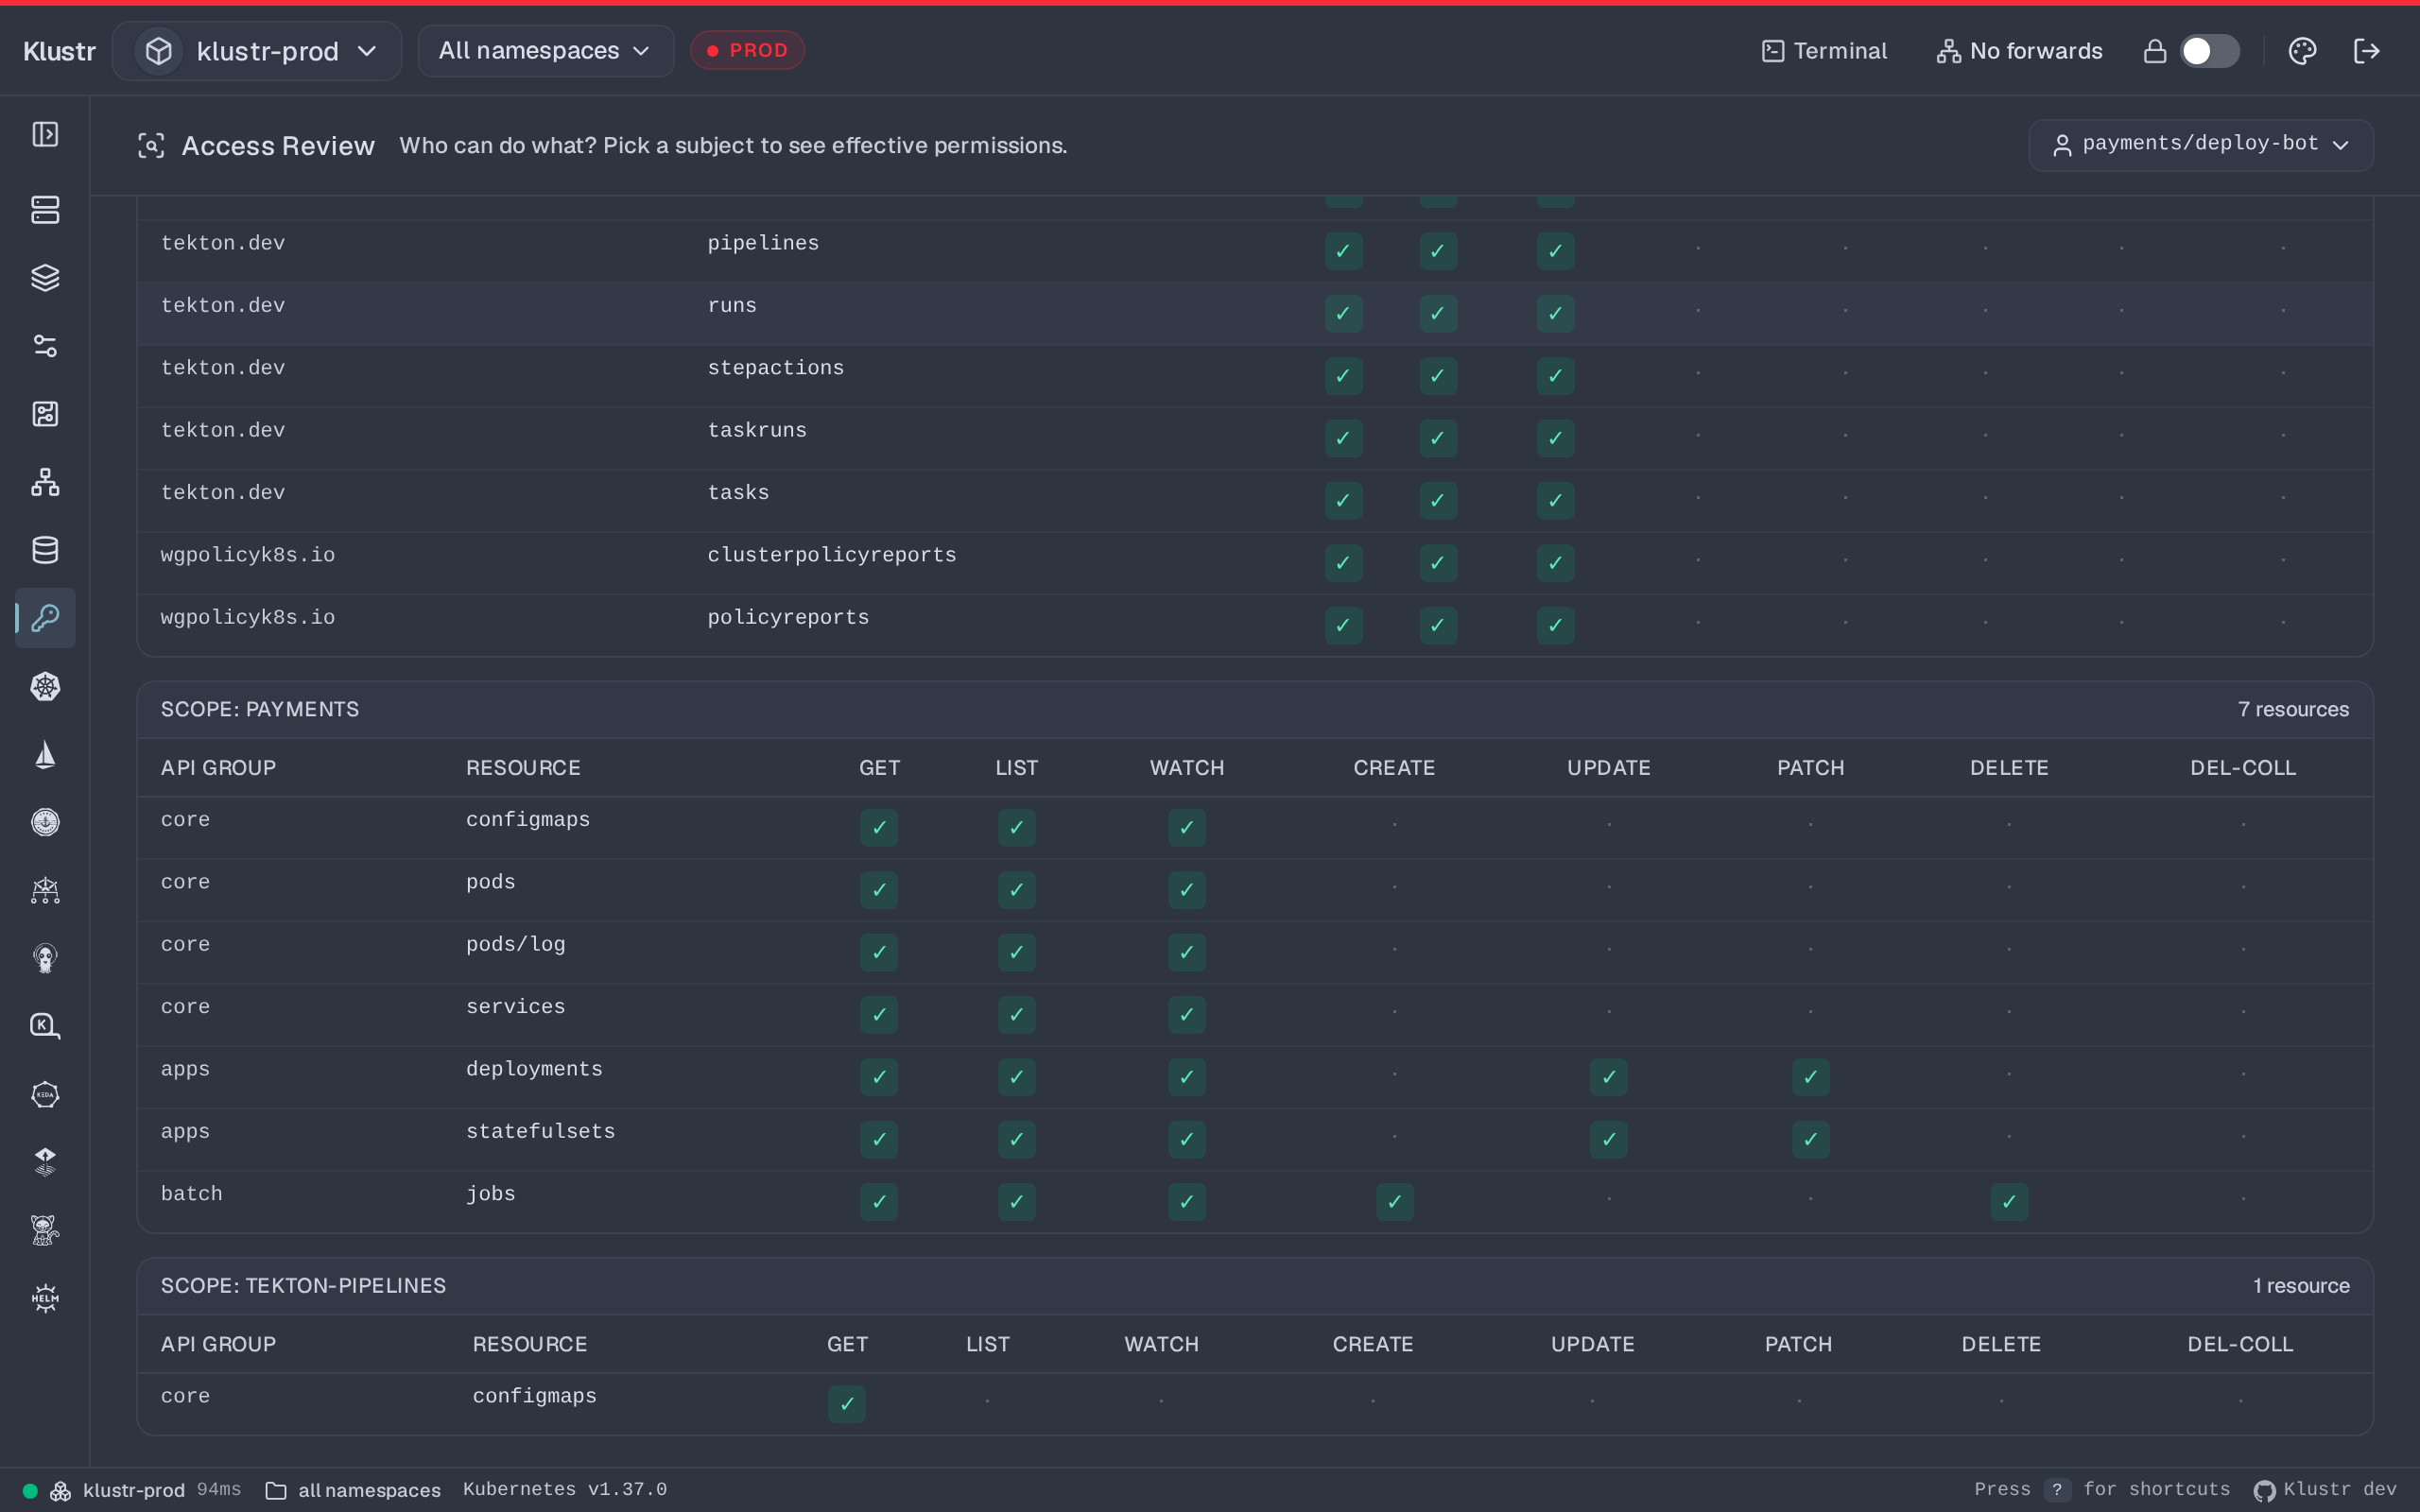
| Access Review — a ServiceAccount's effective permissions as a resource × verb matrix per scope, wildcard rules flagged | YAML edit — Monaco editor with the server-side dry-run diff before apply |
 |
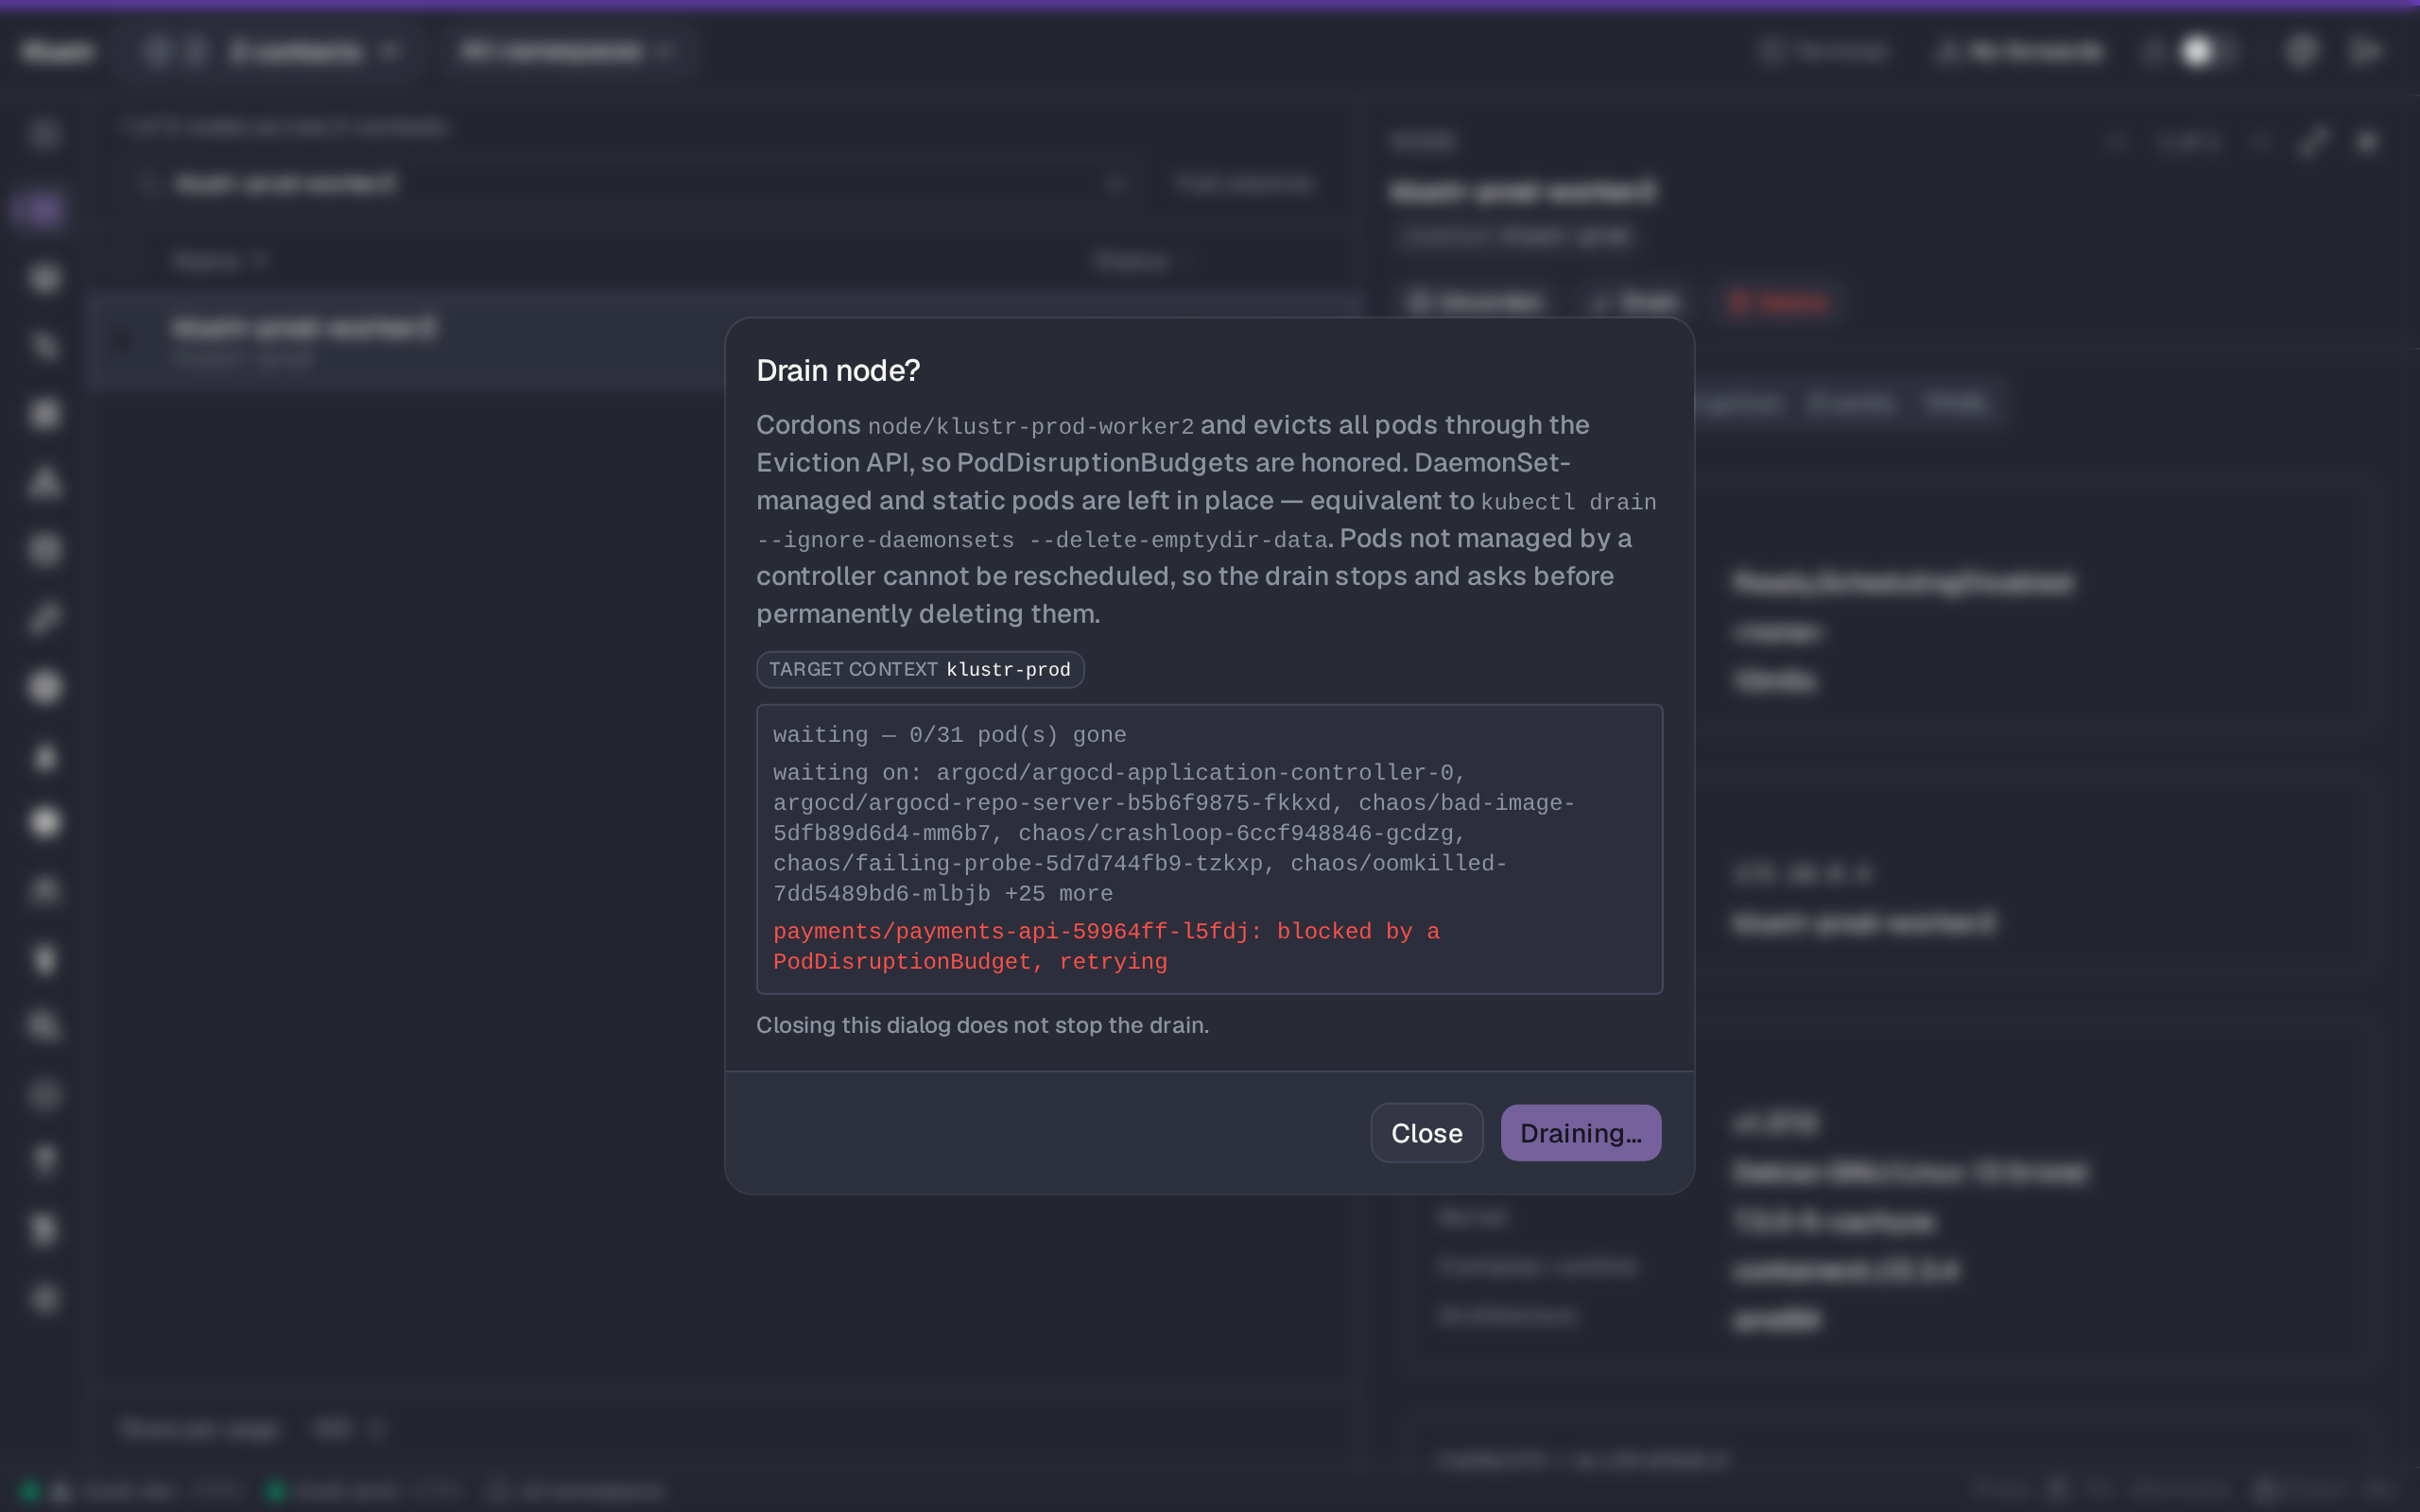 |
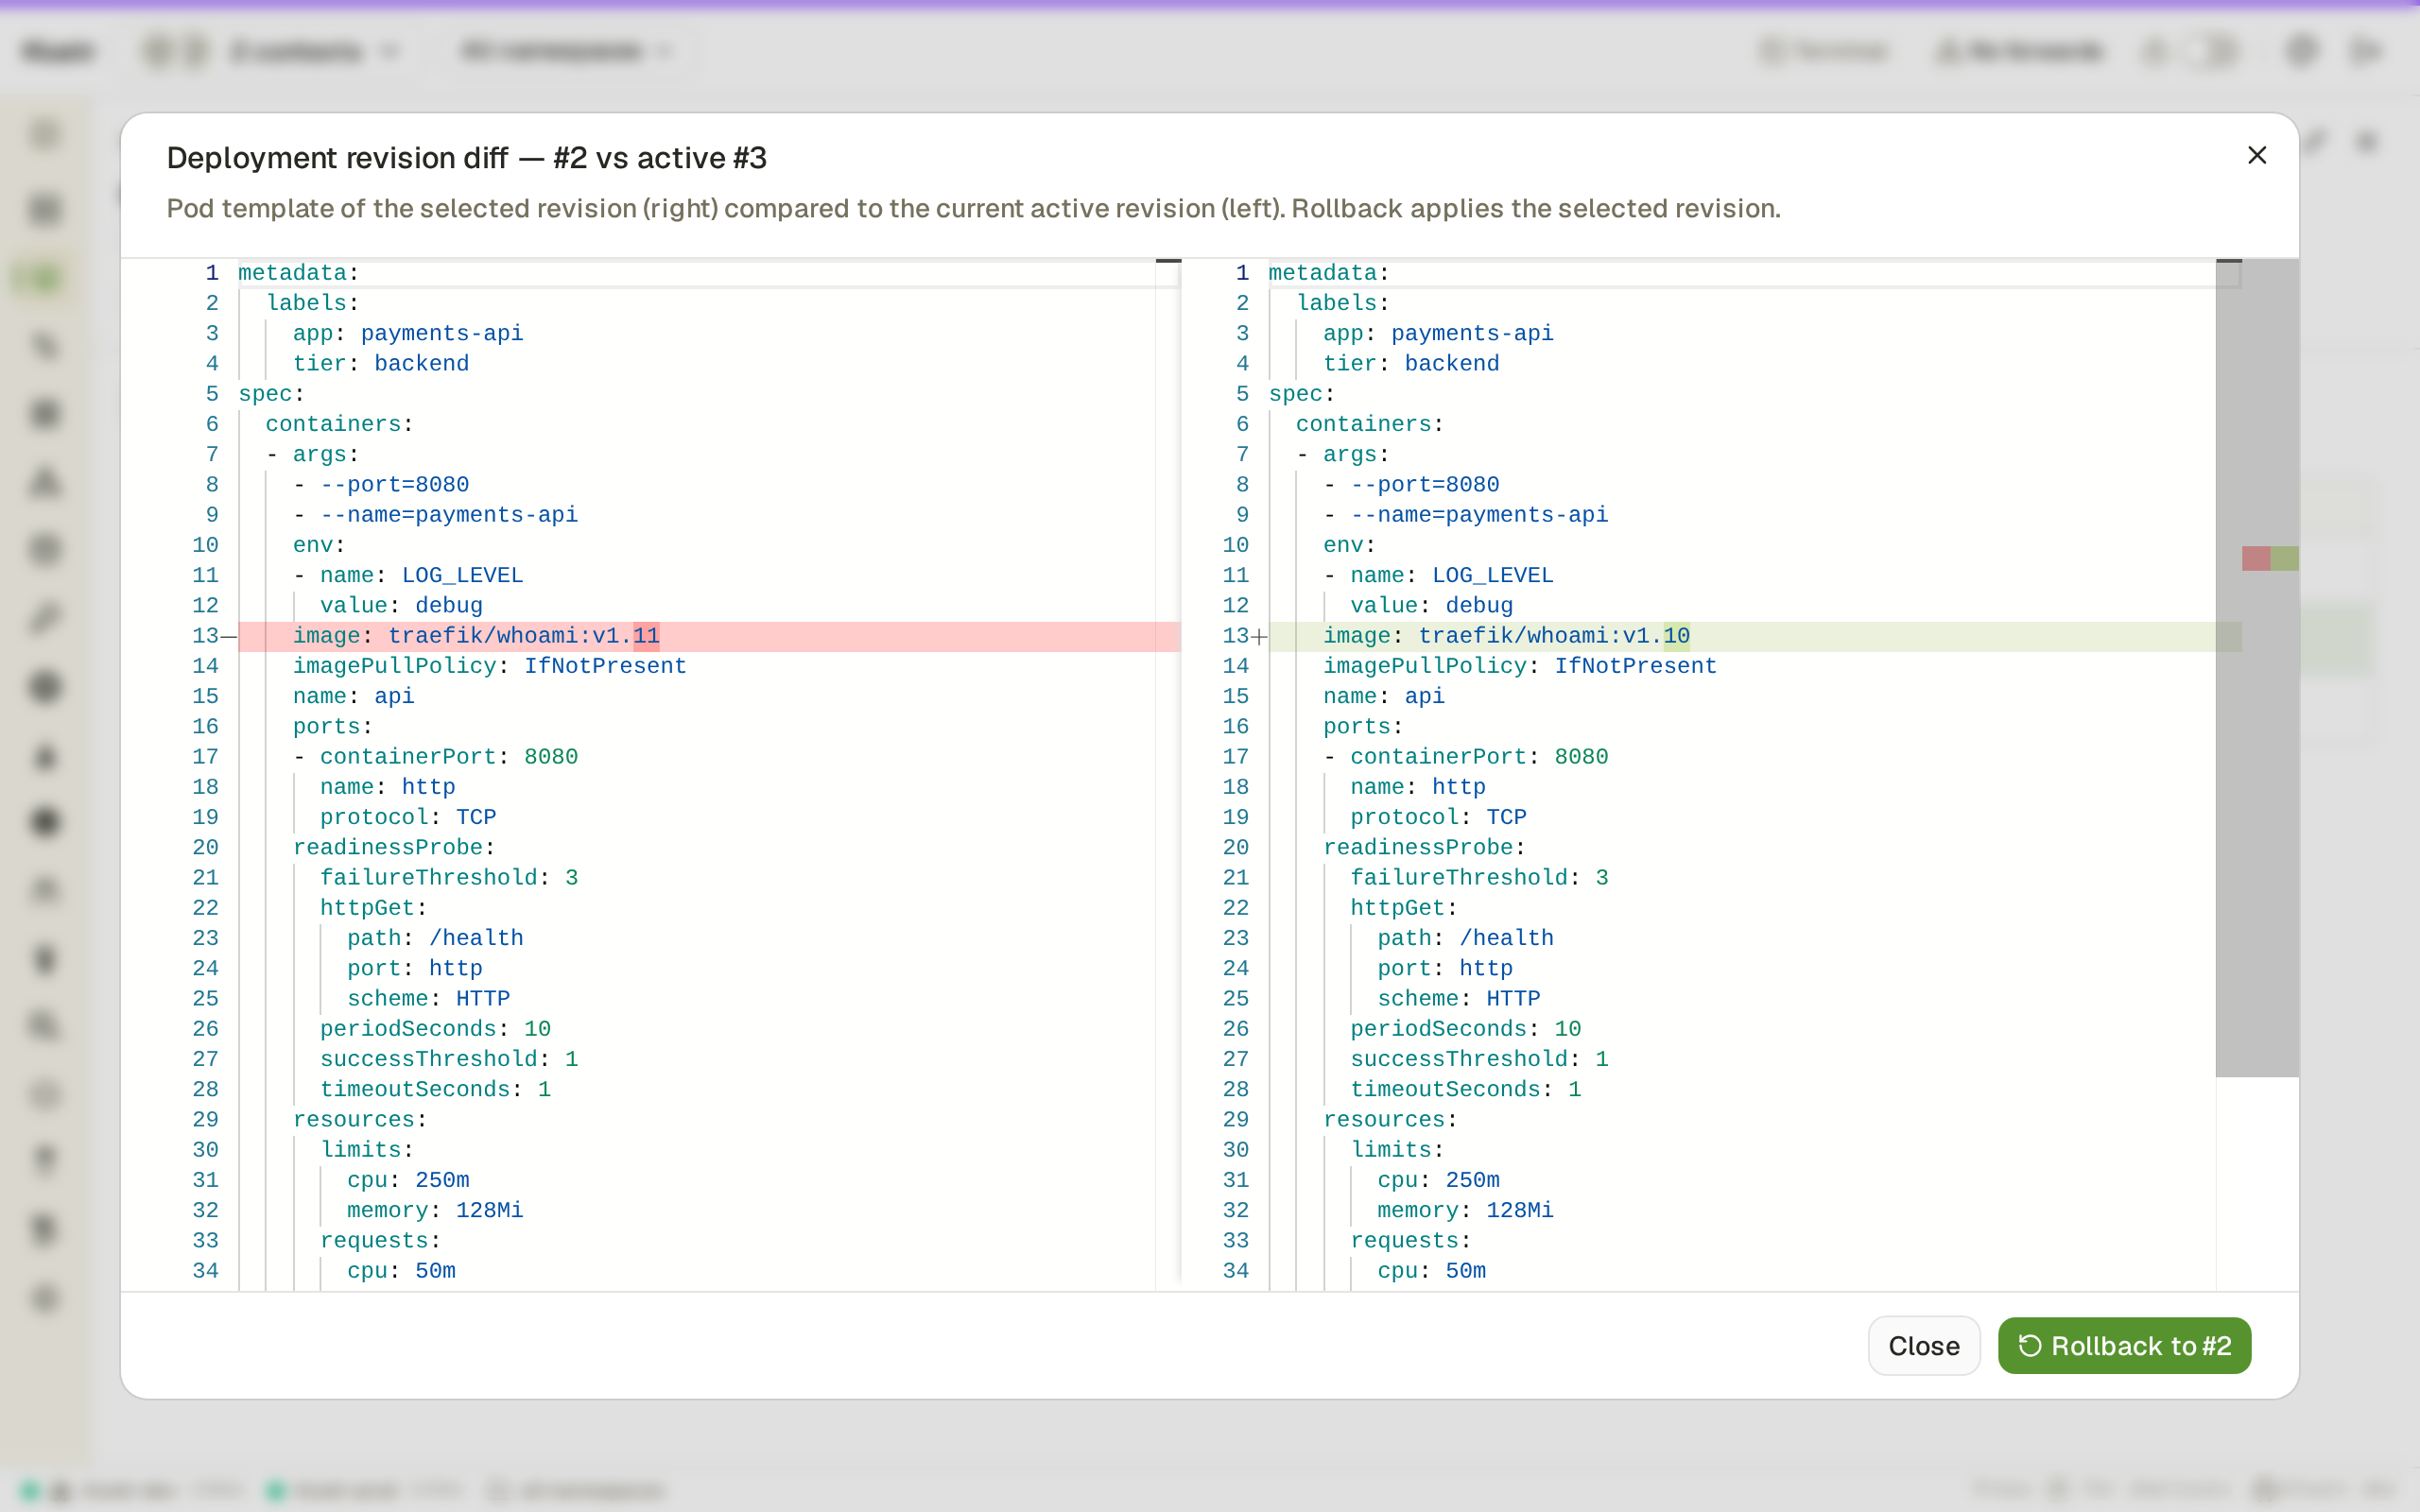
| Rollout history — revision diff with change causes and one-click rollback | Node drain — Eviction API progress, the PDB-blocked pod called out and retried |
 |
 |
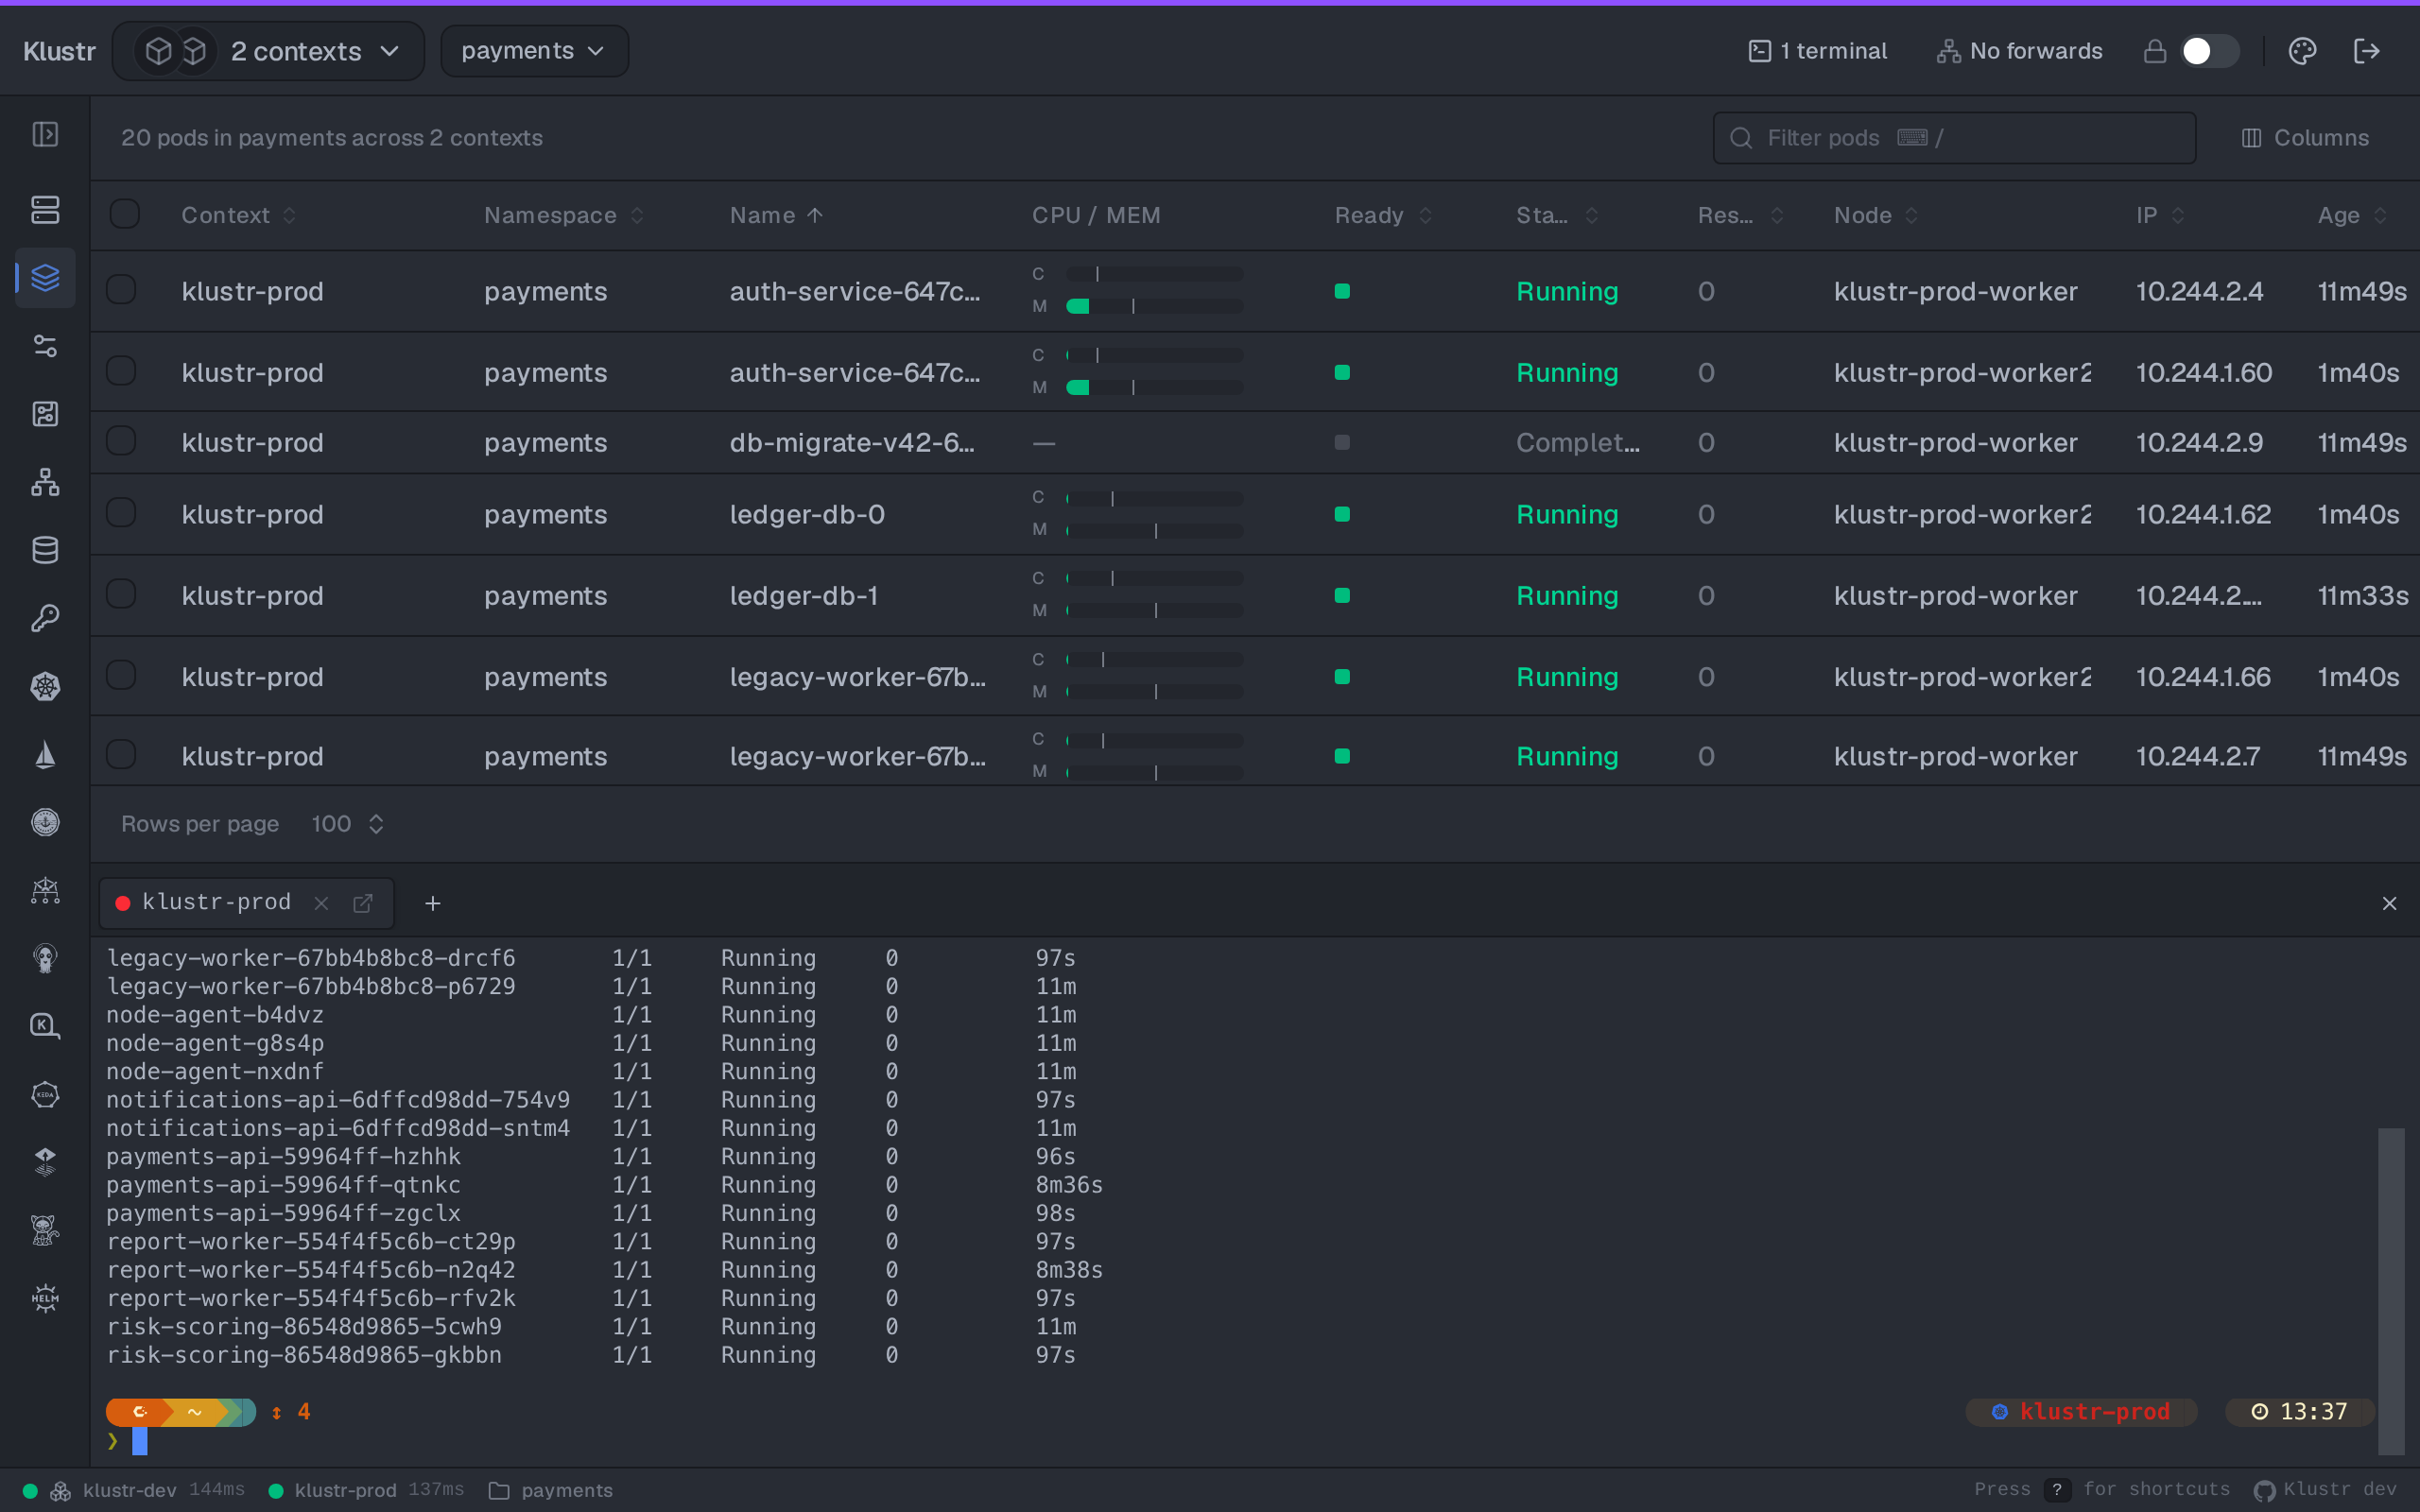
Terminal — a local shell pinned to a context under the table, KUBECONFIG already set |
Cluster overview — CPU / memory / pod capacity per cluster and a live warnings feed |
 |
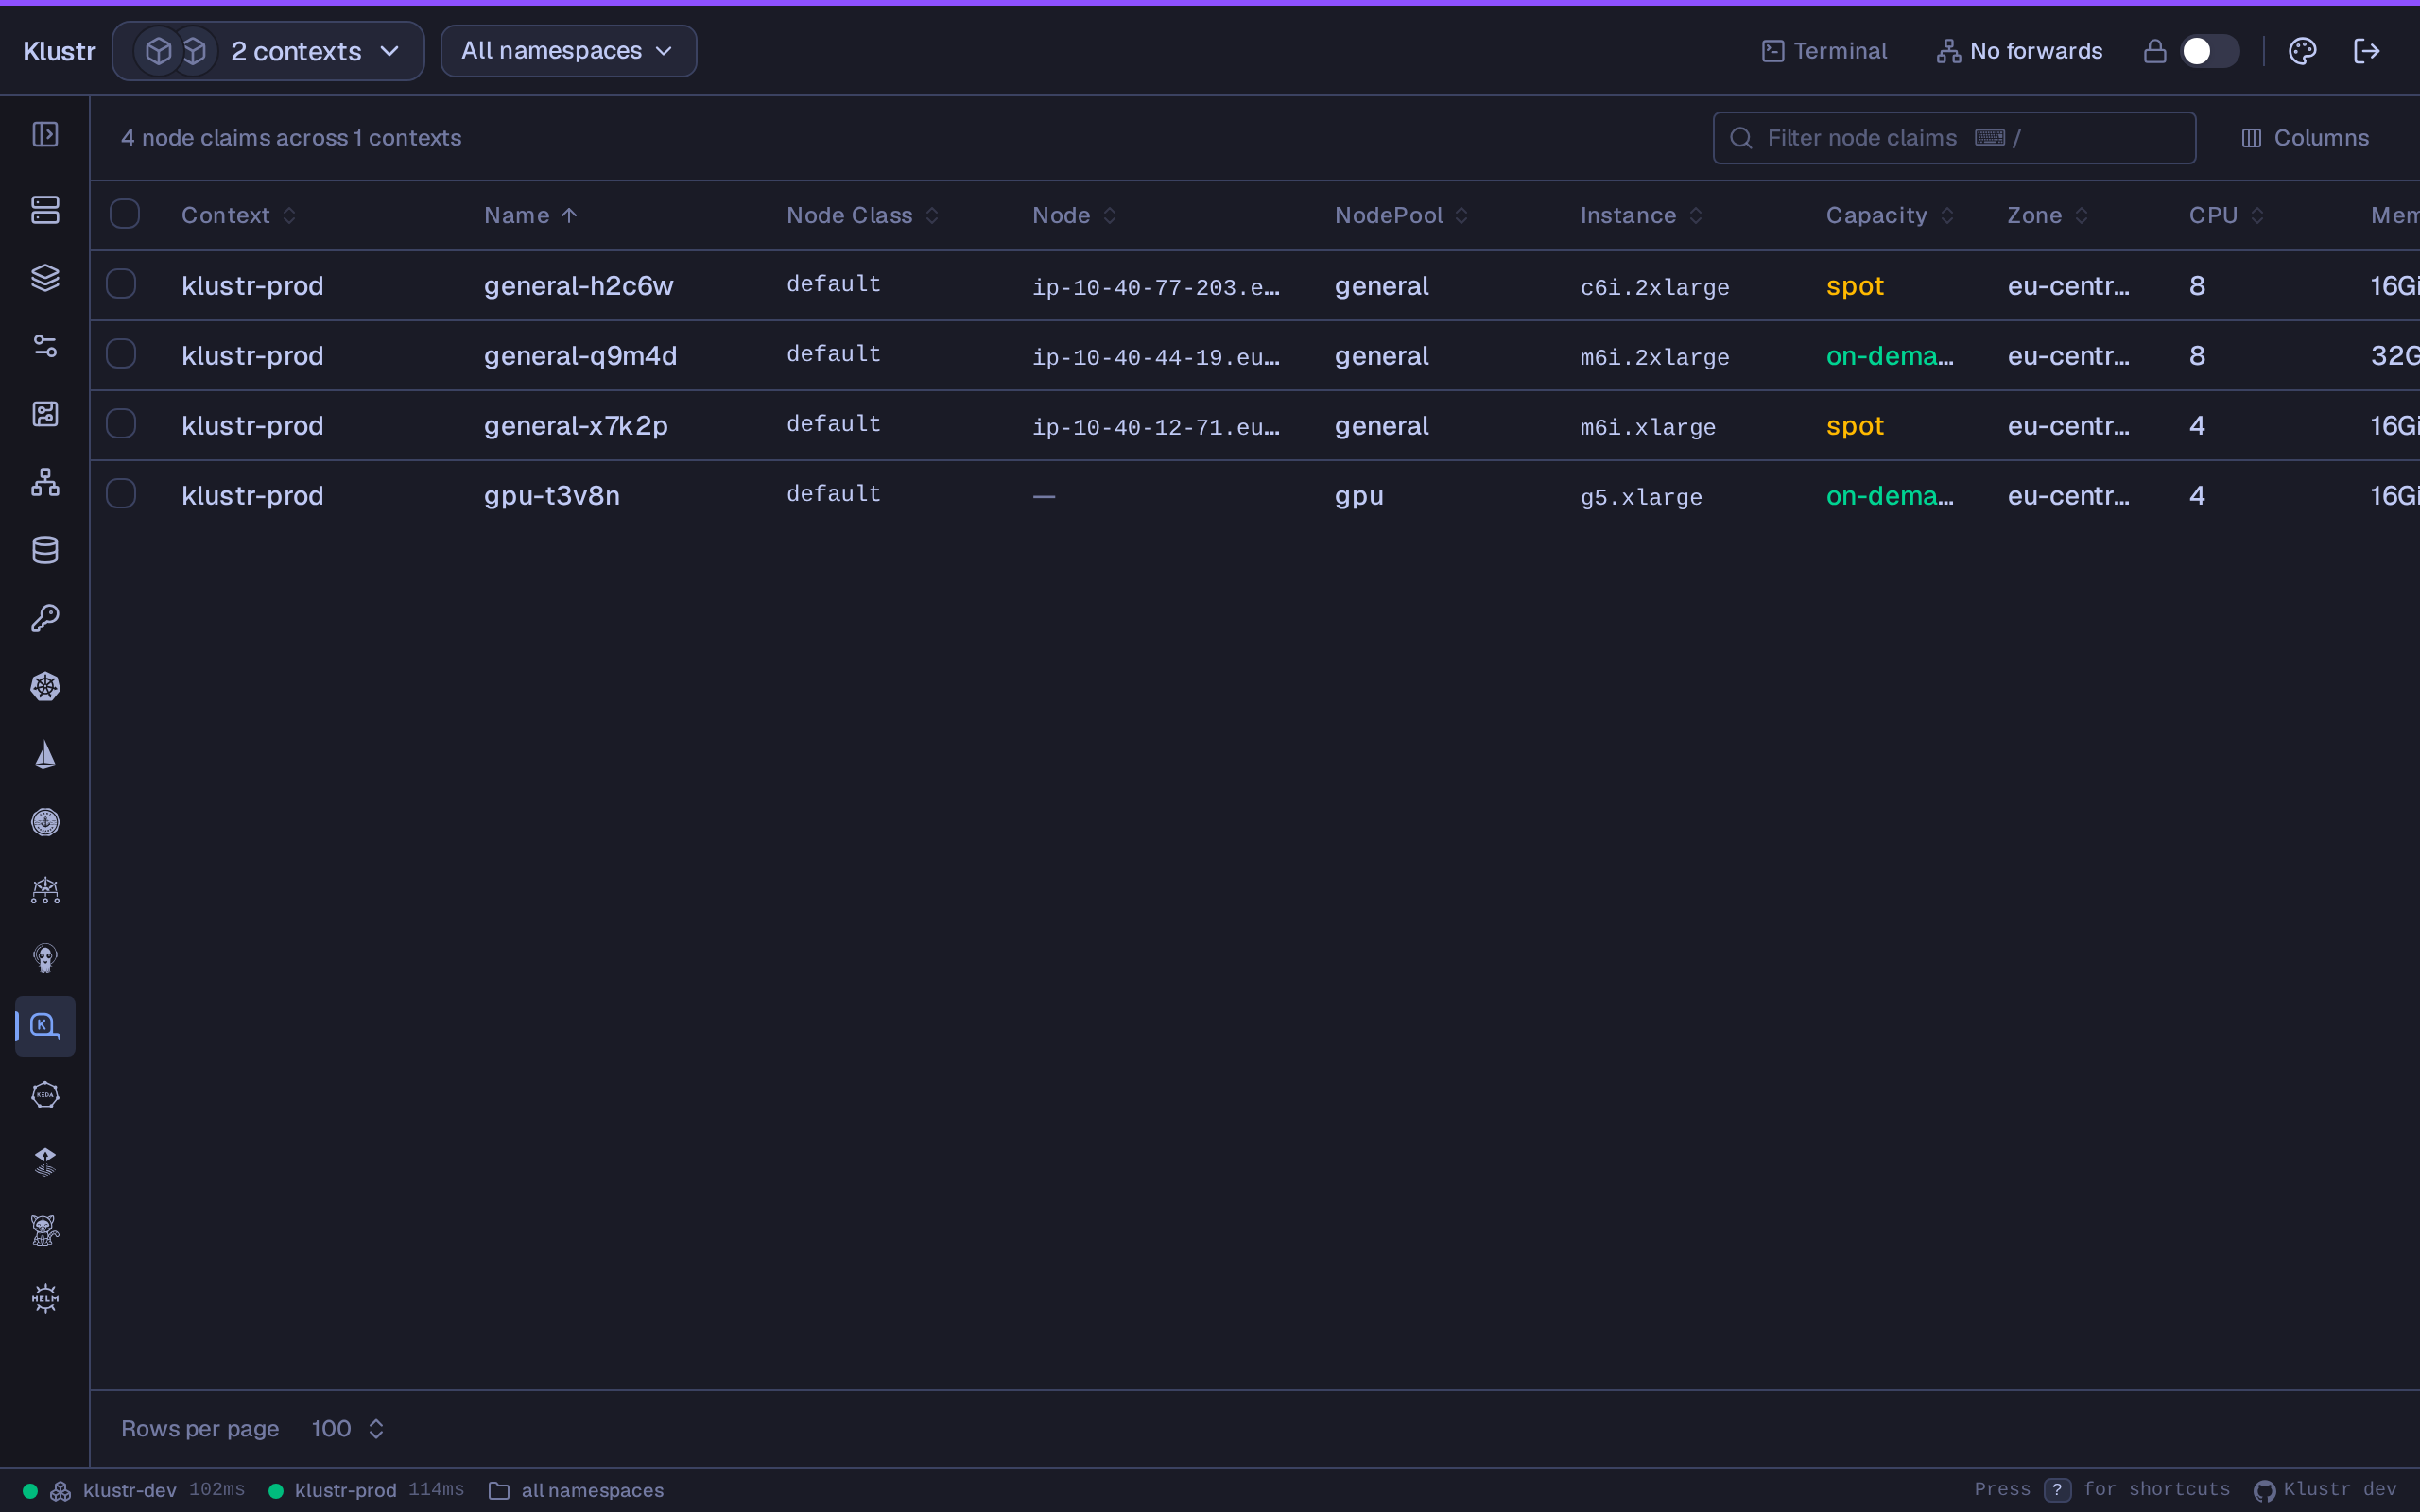 |
| Istio — a VirtualService's weighted canary and header match as a rule table | Karpenter — NodeClaims with node, pool, instance, zone and the Launched / Registered / Initialized steps |
 |
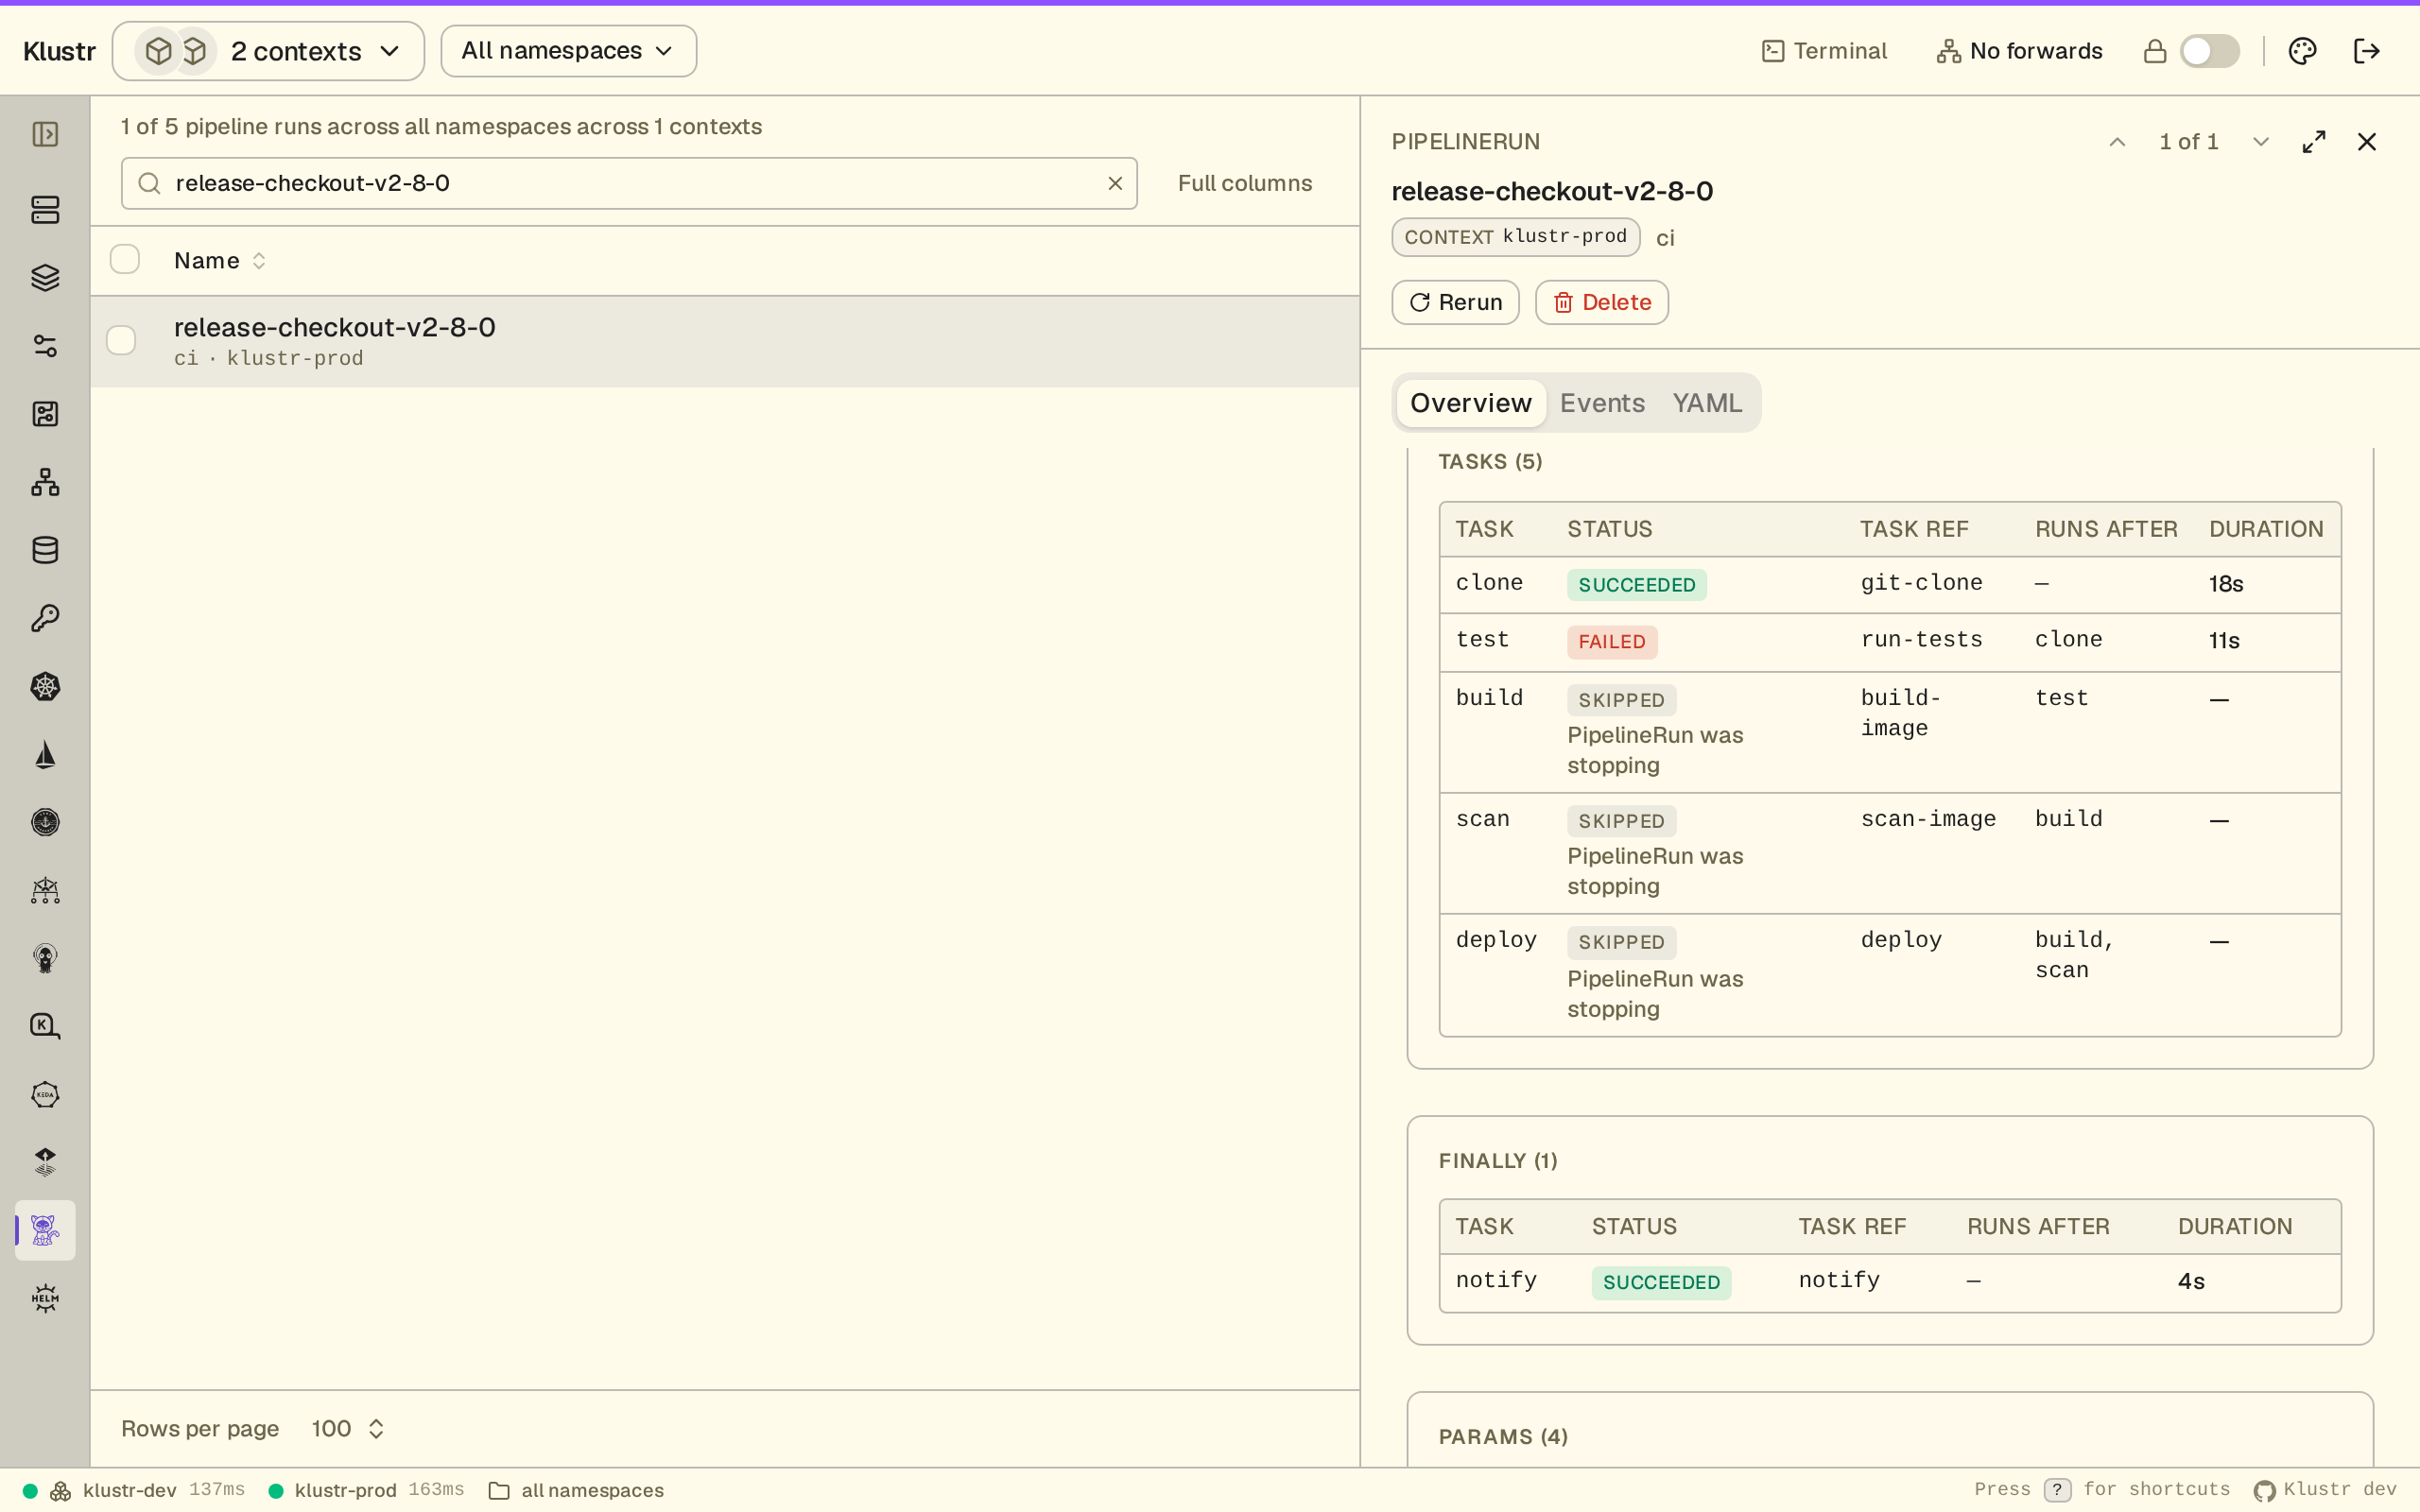 |
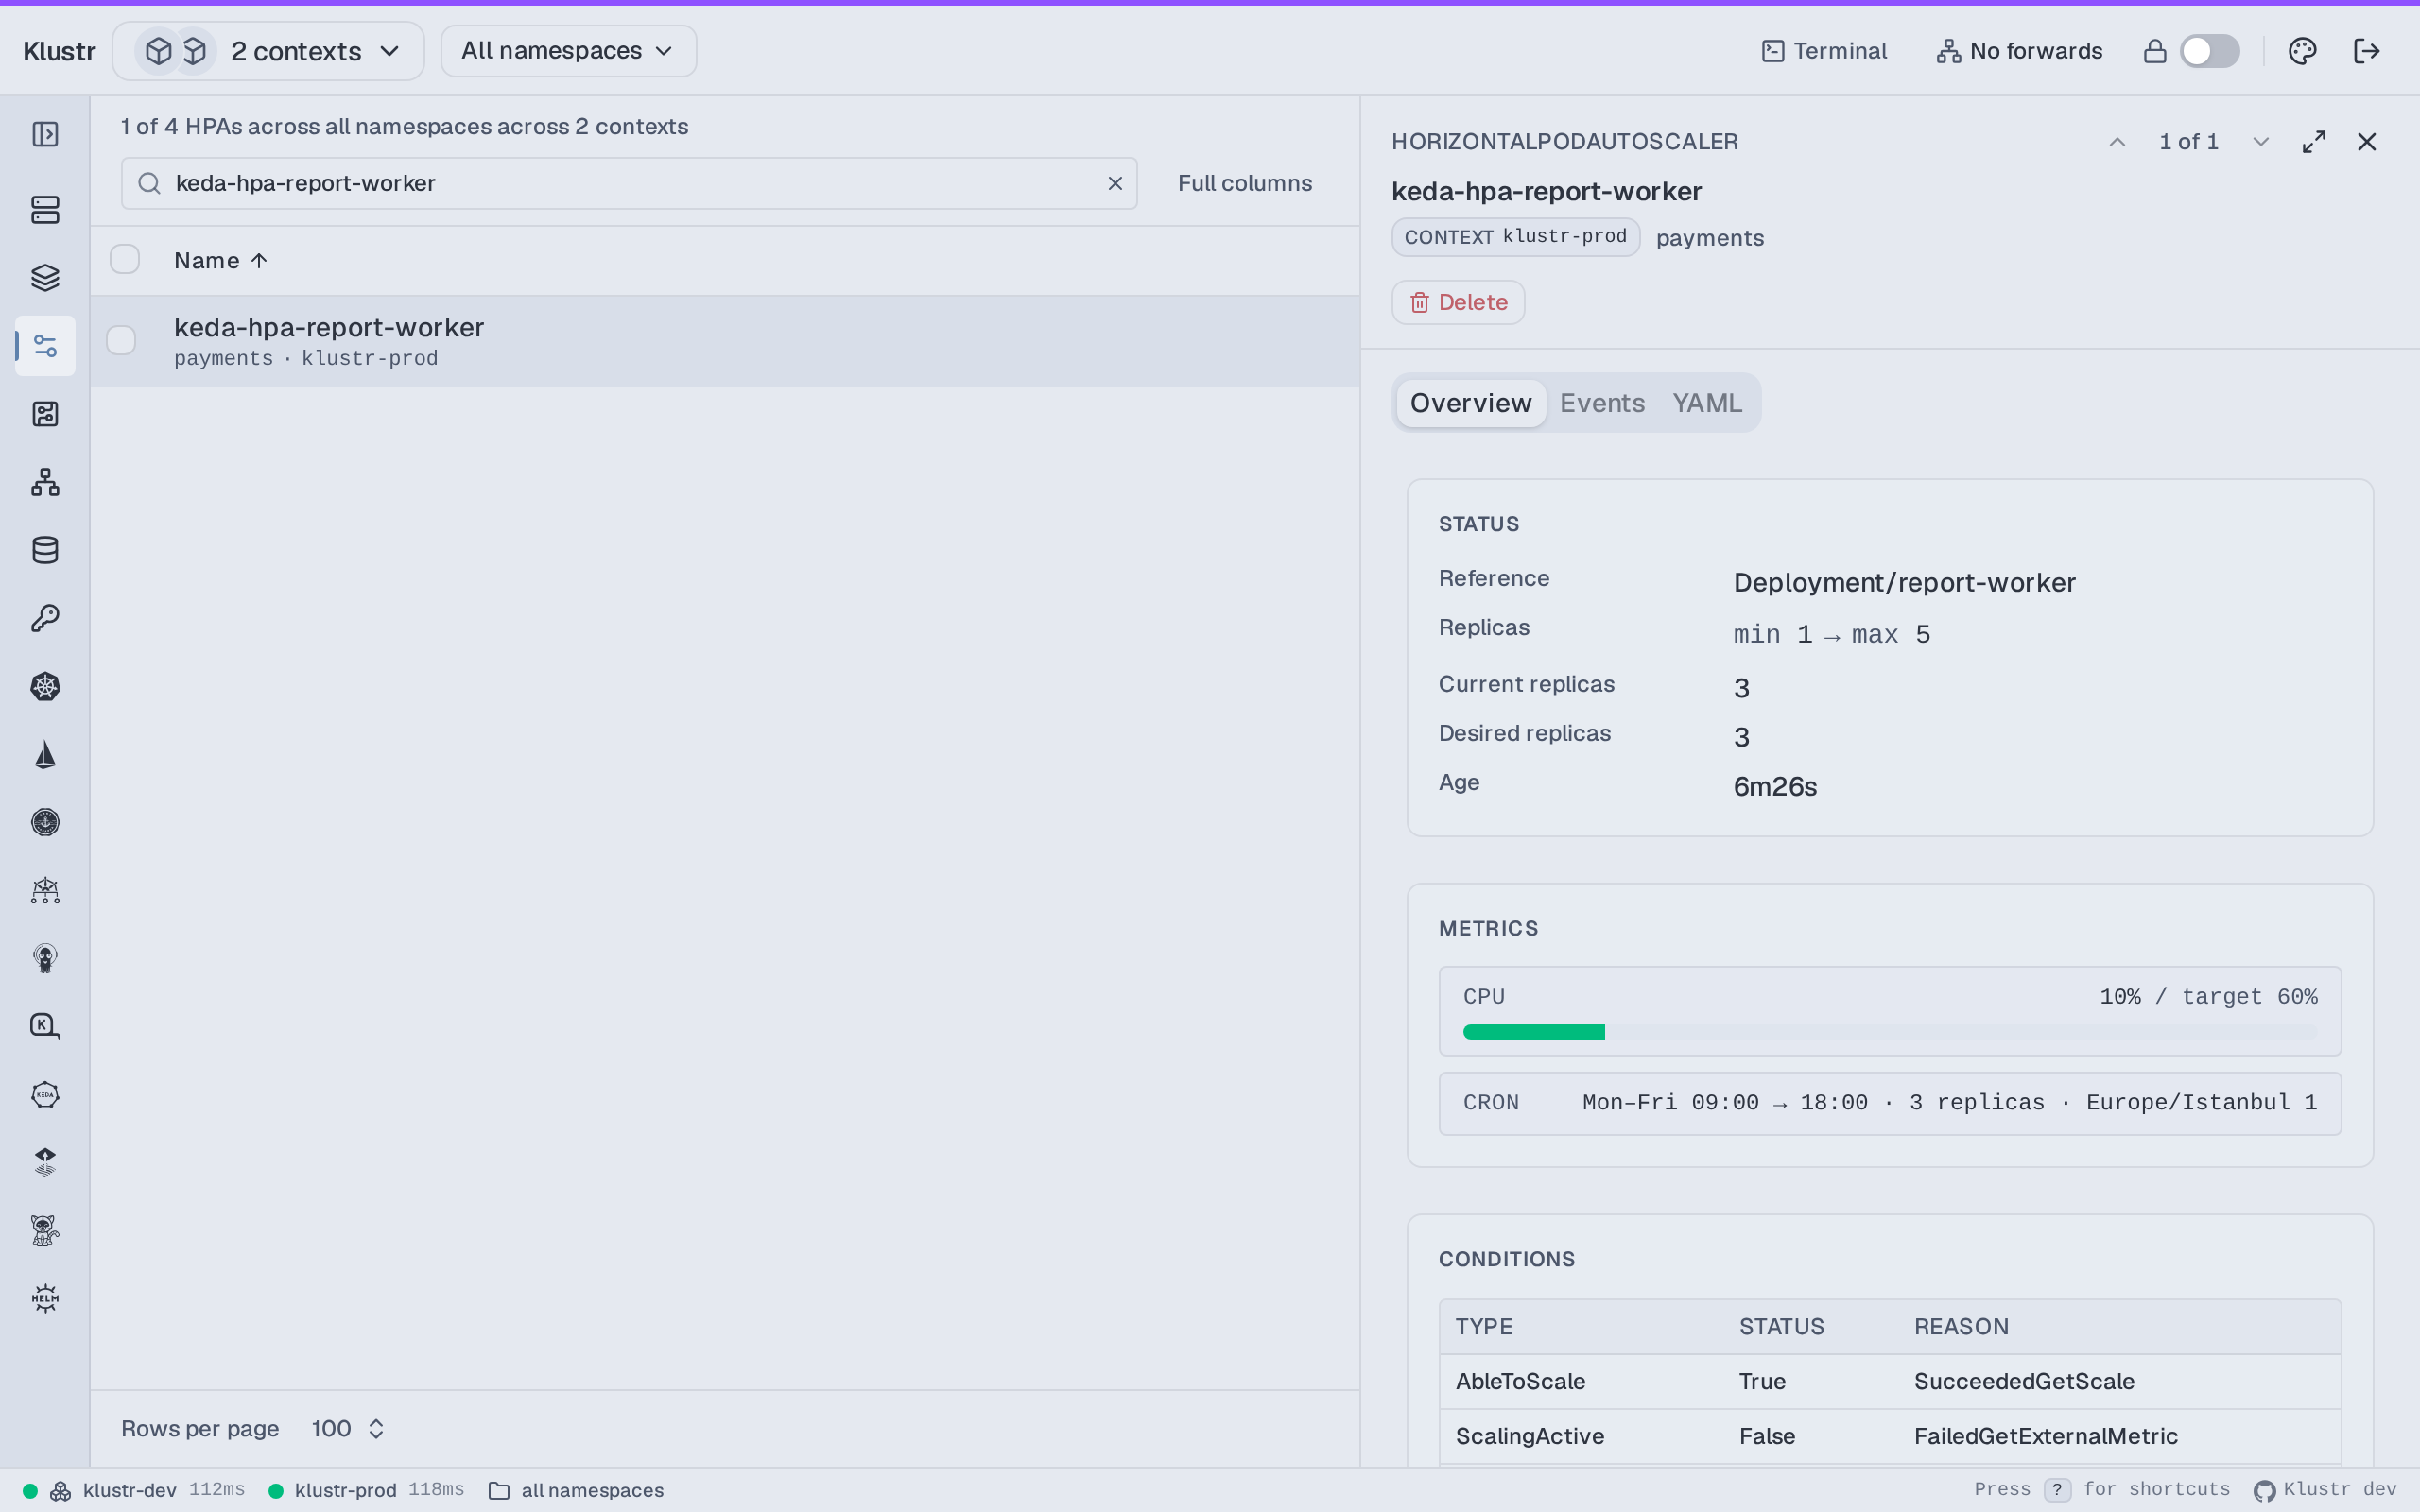
| KEDA — a KEDA-managed HPA with its external metrics mapped back to the cron and CPU triggers | Tekton — a failed PipelineRun's task table: the failing test, the tasks it skipped, and the finally task that still ran |
 |
|
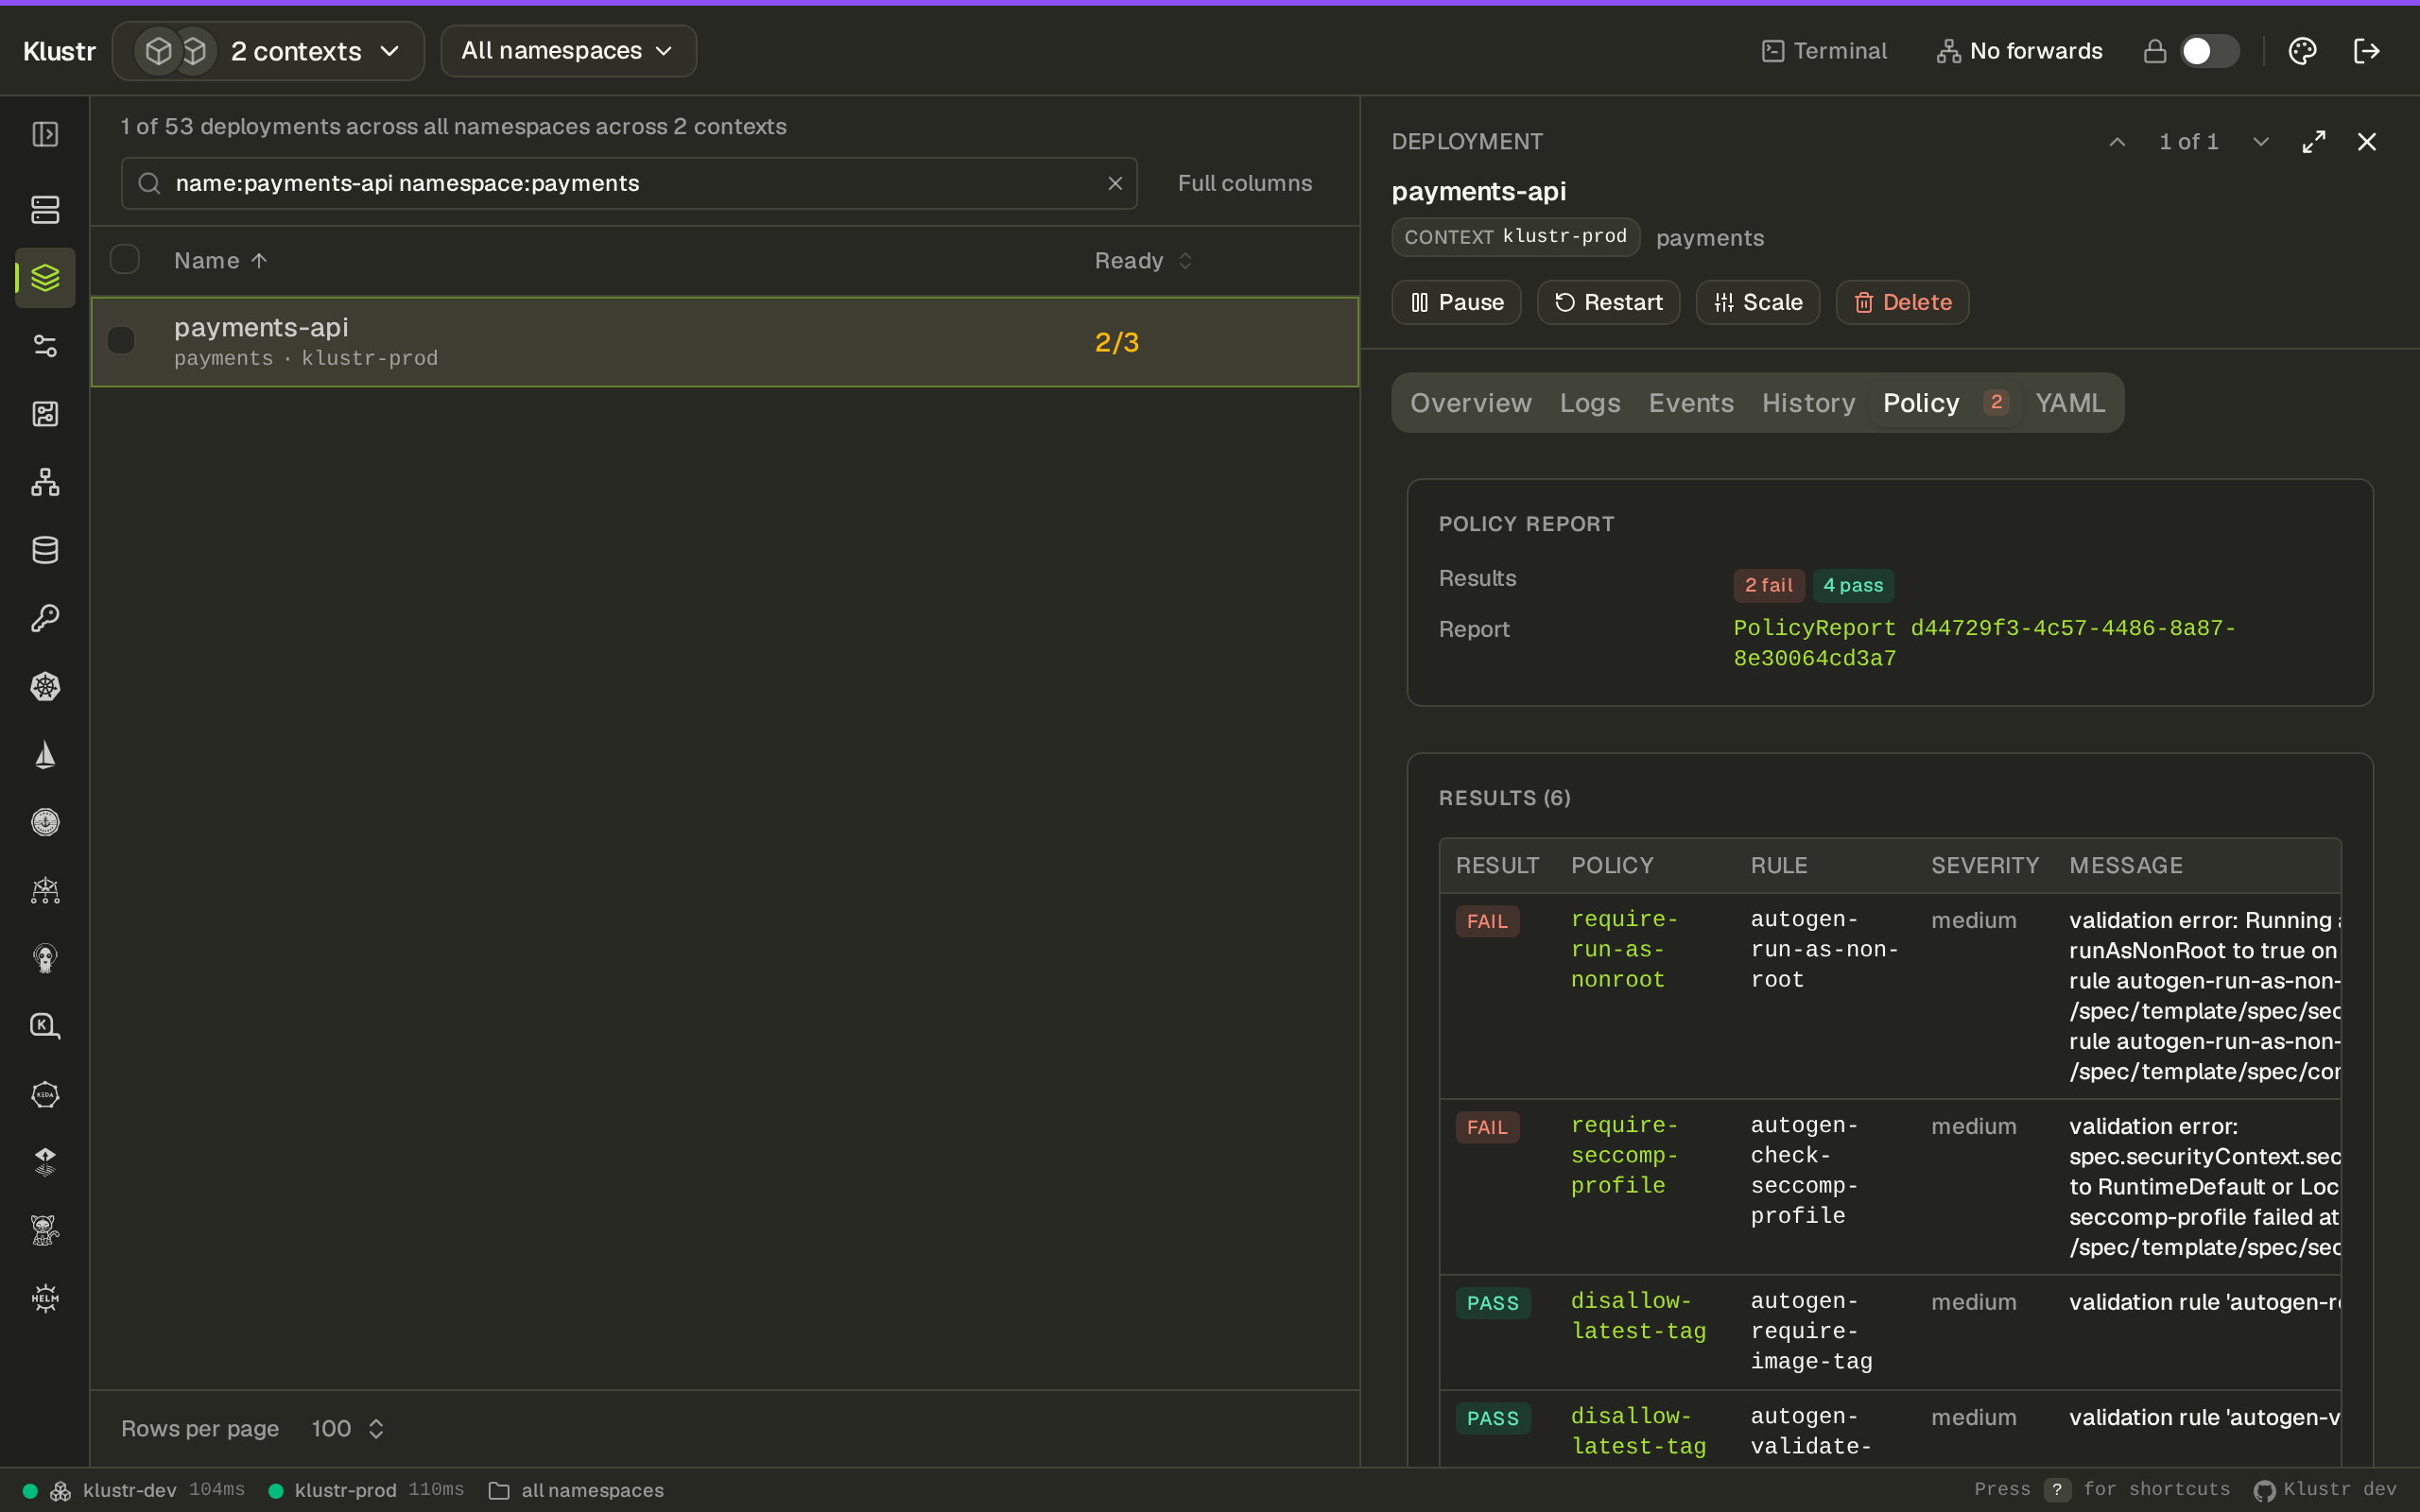
| Kyverno — a Deployment's own policy report on its Policy tab, the failing count on the tab label |
Install
macOS (Apple Silicon)
The release build is signed with a Developer ID Application certificate and notarized by Apple, so Gatekeeper opens it directly — even offline.
Homebrew
brew tap sametkum/klustr
brew install klustr
After the initial brew tap, future updates are just brew upgrade klustr (or brew upgrade for everything), and brew search klustr / brew info klustr start finding it.
Manual
Download the latest darwin-arm64 tarball from the Releases page, then:
tar -xzf klustr-*-darwin-arm64.tar.gz
mv klustr.app /Applications/
open /Applications/klustr.app
Linux (amd64)
The Linux binary links against webkit2gtk-4.1 + gtk-3. Ubuntu 24.04+, Fedora 39+, Arch and most other modern distros ship those runtime libraries by default; on Ubuntu 22.04 install libwebkit2gtk-4.1-0 libgtk-3-0 first.
Arch / CachyOS / Manjaro / Endeavour (AUR)
paru -S klustr-bin
# or
yay -S klustr-bin
The klustr-bin PKGBUILD uses the prebuilt release tarball, so install completes in seconds. paru -Syu keeps it up to date.
Debian / Ubuntu (.deb)
The .deb pulls in the runtime dependencies automatically and registers a klustr desktop entry.
VERSION="$(curl -fsSL https://api.github.com/repos/SametKUM/klustr/releases/latest | grep -oP '"tag_name":\s*"\K[^"]+')"
DEB="klustr_${VERSION#v}_amd64.deb"
curl -LO "https://github.com/SametKUM/klustr/releases/download/${VERSION}/${DEB}"
sudo apt install "./${DEB}"
Manual (tarball)
Download the latest linux-amd64 tarball from the Releases page, then:
tar -xzf klustr-*-linux-amd64.tar.gz
install -Dm755 klustr ~/.local/bin/klustr
klustr
Windows
Download the latest windows-amd64 zip from the Releases page, extract it and run klustr.exe. Klustr is tested on Windows 11, which ships the WebView2 runtime it renders with.
The Windows build is not code-signed yet. On first launch SmartScreen shows "Windows protected your PC": choose More info, then Run anyway. With Smart App Control on, Windows blocks unsigned apps outright.
Quick start
- Klustr reads
~/.kube/configat launch. - On first run, pick a context — or check two or more to view them aggregated as one cluster. Save a recurring selection as a named group for one-click reconnect, and toggle Auto-connect on a card to pin it as the default.
- Browse via the sidebar, click any row for a detail dialog, use
⌘Kto open the command palette, or⌘Pto search pods by name. The header's Disconnect button drops you back to the picker at any time.
Documentation
Task-focused guides live at klustr.dev/docs (source: SametKUM/klustr.dev):
- Getting started — contexts, namespaces, read-only mode
- Multi-context & aggregated mode — many clusters as one, groups, tags
- Credential helpers — aws-vault and other exec plugins under a GUI launch
- Cluster & workloads overviews — capacity donuts, workload health, events feed
- Workloads & debugging — logs, exec, port-forward, node shell
- Terminal — the built-in shell drawer and external terminal apps
- Helm · GitOps: Argo CD & Flux · Tekton Pipelines · Gateway API · Kyverno & policy reports · Platform integrations · Custom Resources
Build from source
mise install     # installs Go, Node, Wails CLI pinned in .mise.toml
wails dev        # hot-reload dev session

# or a production build for your host platform
wails build -trimpath -clean
Architecture (short version)
| Layer | Choice |
|---|---|
| Desktop | Wails v2 (Go + native webview) |
| Backend | Go 1.27 + client-go (typed clientset + dynamic) + sigs.k8s.io/gateway-api |
| Frontend | React 19 · TypeScript · Vite |
| UI | Tailwind CSS · shadcn/ui |
| State | Zustand (real-time) · TanStack Query (mutations only) |
| Tables | TanStack Table |
| Live data | client-go informers → Wails events → Zustand → React |
Full design notes, conventions and the "add a new resource kind" recipe live in AGENTS.md.
Roadmap
- Every built-in resource kind (incl. full RBAC: ServiceAccounts, Roles, RoleBindings, ClusterRoles, ClusterRoleBindings)
- Access Review — subject → effective-permission matrix with binding trace, implicit-group expansion (
system:serviceaccounts:*,system:authenticated), wildcard / cluster-admin detection, live across every active context - Logs, exec, port-forwarding
- Node shell (privileged
nsenterpod), cordon/uncordon, PDB-aware drain - YAML edit / apply with diff, scale, restart, deployment pause/resume, HPA inline edit
- In-place pod resize (CPU/memory requests & limits via the
pods/resizesubresource, no recreation) - Rollout history with revision diff and one-click rollback (Deployments / StatefulSets / DaemonSets)
- Cross-resource navigation (related pods, owner/node links, back stack)
- Custom Resource Definitions (CRDs)
- Helm support — release browser, dry-run diff, install / upgrade / rollback / uninstall, repo management
- Gateway API — Gateways, HTTPRoutes, GRPCRoutes, GatewayClasses, ReferenceGrants (typed informers, status pills, listener / rule / RouteParentStatus tables)
- cert-manager — Certificates, Issuers / ClusterIssuers, CertificateRequests, Orders, Challenges (issuance-chain drill-down, ready/expiry status, one-click Renew)
- Istio — VirtualServices, DestinationRules, PeerAuthentications (served version read from the discovered CRD)
- Cilium — policies, endpoints, nodes, identities, CIDR groups, LB IPAM, L2 announcements, egress gateways and BGP (CRD-backed views)
- Karpenter — NodePools, NodeClaims, AWS EC2NodeClasses (provisioning status, resolved infrastructure and reference navigation)
- Flux image automation — ImageRepositories, ImagePolicies, ImageUpdateAutomations (tag/digest selection, Git update status, cross-namespace references)
- Tekton — PipelineRuns, TaskRuns, Pipelines, Tasks (task table, step logs, Cancel and Rerun)
- Kyverno — ClusterPolicies, Policies, ValidatingPolicies, PolicyExceptions, PolicyReports (per-policy violations, per-resource Policy tab)
- [


